Attacking and Detecting Attacks on Kubernetes Clusters
Explore Kubernetes security through live demonstrations of attacks, detection methods, and defense strategies using the DEF CON CTF cluster as a practical example.
Making Sense of a Confusing Detection and Response Solutions Landscape
Unravel the complex landscape of threat detection and response solutions with expert insights, research findings, and practical advice for implementing effective cybersecurity strategies.
Exposing Attacks Hiding in the Sheer Noise of False Positives - Using Data Science for Security Operations
Discover how data science transforms overwhelming security data into actionable insights, helping identify coordinated attacks amid false positives using open-source models and security knowledge encoding.
Malware Management Framework - We Detected WinNTI With It
Explore a comprehensive Malware Management Framework and its successful application in detecting WinNTI. Learn effective strategies for identifying and mitigating malware threats in cybersecurity.
Cyber Hygiene and Ransomware Defense Using BrickStor SP User Behavior Analytics
Discover how BrickStor SP's active defense and user behavior analytics combat evolving ransomware threats, building cyber resiliency through sophisticated protection mechanisms and attack prevention strategies.
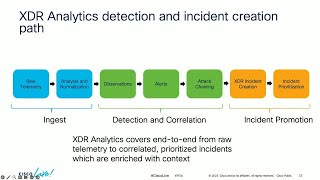
Security Analytics and Cisco XDR - An Overview
Discover the latest advancements in security analytics and XDR technology through a comprehensive technical overview of Cisco's newest security solutions and capabilities.
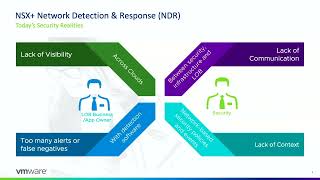
Minimize the Risk of Ransomware with VMware NSX+ Network Detection and Response
Discover how NSX+ Network Detection and Response protects multi-cloud environments through proactive threat detection, zero-trust defense implementation, and comprehensive security incident response capabilities.
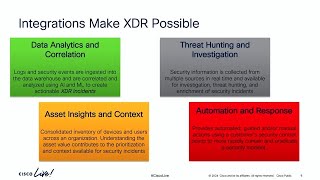
Cisco XDR Detection Analytics and Generative AI in Cybersecurity
Discover how Cisco XDR leverages generative AI and advanced analytics to enhance threat detection, correlation, and response capabilities in modern cybersecurity environments.
Bypassing EDR Detection: Userland Hooking Techniques and New Approaches
Explore advanced techniques for bypassing EDR solutions, including a new approach with Proof of Concept for understanding userland hooking and detection mechanisms.
Evolving into the Next-Gen SOC - Baby Steps to the Future
Discover how to transform traditional Security Operations Centers into agile, next-generation entities capable of addressing modern cyber threats and future challenges through practical, actionable steps.
Windows System Monitor (Sysmon) for Incident Investigation and Threat Response
Master Windows System Monitor (Sysmon) for incident investigation, learning to track program execution, registry writes, and DNS queries to effectively trace threat actor activities and enhance system security.
Driver Risk Scores: Threat Detection System for Vulnerable Device Drivers
Discover how Driver Risk Scores (DRS) system evaluates device driver vulnerabilities through seven key traits, enabling informed security decisions for system administrators and security teams.
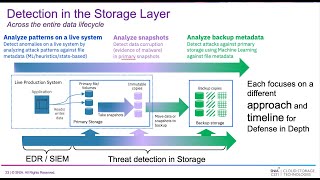
Cyberstorage and Extended Detection and Response - Threat Detection Through Storage
Discover how storage systems can enhance cybersecurity through threat detection and response, exploring Cyberstorage and XDR concepts for protecting valuable data assets from modern cyber threats.
Building a Dynamic Rules Engine with Kafka Streams
Develop a real-time threat detection system using Kafka Streams. Learn to handle dynamic rule modifications, implement external data feeds, and apply best practices for stream processing.
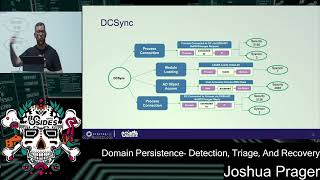
Domain Persistence - Detection, Triage, and Recovery
Explore Active Directory domain persistence techniques, focusing on detection, triage, and recovery strategies. Learn to identify attacks, reclaim control, and enhance Windows Security event auditing.

AWS AI Services Transforming DevSecOps - Amazon Q Insights
Explore how AWS AI services like CodeGuru, Amazon Q, and GuardDuty revolutionize DevSecOps, enhancing code quality, extracting insights, and bolstering security in AWS environments.
Unlocking the Power of Kubernetes - AI-Driven Innovations for Next-Gen Infrastructure
Explore AI-driven innovations in Kubernetes for efficient workload deployment, resource optimization, and enhanced security, revolutionizing infrastructure management for unprecedented efficiency and resilience.
DoubleDrive - Double Agents Hide Behind The Clouds
Explore cloud-based double agent techniques in IT security. Learn about innovative attack methods and defense strategies for protecting cloud environments.
A Needle in a Haystack: Finding Threats in Billions of Cloud Logs
Discover techniques for efficiently analyzing massive cloud audit logs to identify security threats using basic cloud tools and advanced platforms like OpenSearch and Kubernetes.
Below the Radar: Identifying Hidden Threats Within the Development Ecosystem
Explore critical threats in cloud-native environments, focusing on hidden exposed secrets in code. Learn about vulnerabilities in source code management, Kubernetes secrets, and Shadow IT, with mitigation strategies and tools.
Flying Under the Radar - New Security Evasion Techniques
Explore cutting-edge security evasion techniques used by threat actors, their evolution from traditional tools, and effective mitigation strategies to enhance your organization's cybersecurity posture.