Secure Your Supply Chain: Adding a Software Bill of Materials to Containers for Improved Vulnerability Scanning
Learn to enhance container security by implementing Software Bill of Materials (SBOM), improving vulnerability scanning, and adopting best practices for a more robust supply chain.
Hacking the Cloud Native Renaissance - Lowering Risk of Kubernetes Adoption
Explore Kubernetes adoption risks and security challenges in cloud-native systems. Learn from real-world hacks, container breakouts, and cloud compromises to enhance your system's resilience and protection.
Implementing a Multi-Tenant, Relationship-Based Authorization Model with OpenFGA
Explore implementing multi-tenant, relationship-based authorization using OpenFGA. Learn to model permissions, perform checks, and integrate with identity providers for enhanced security in cloud-native applications.
Container Images and Security 101: 5 Need to Know Facts
Explore 5 essential facts about container image formats, security tools, and best practices for confident application deployment in cloud and Kubernetes environments.
How I Met Your Software - An Image's Journey of Consuming and Securing Software in Cloud Native
Explore software consumption in cloud-native environments, from distribution choices to Kubernetes workloads. Learn about trade-offs, security considerations, and optimizing image deployment.
OIDC and CI/CD: Reducing Security Threats in Your CI Pipeline
Explore CI/CD security risks and learn strategies to reduce attack surfaces using OIDC, proper branch permissions, and credential management for enhanced supply chain protection.
Supply Chain Security in Kubernetes
Aprenda a proteger cargas de trabalho em Kubernetes usando ferramentas de segurança da cadeia de suprimentos, como Tekton Chains, para verificar a procedência e assinatura de imagens antes da implantação.
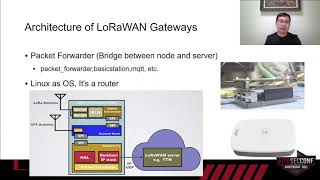
Security Analysis and Practical Attacks of LPWAN
Análisis de seguridad y ataques prácticos a redes LPWAN, enfocándose en LoRaWAN y NB-IoT. Explora vulnerabilidades en la cadena de suministro y módulos, compartiendo hallazgos y recomendaciones para mejorar la seguridad.
Enterprise Security Strategy Leveraging on Zero Trust Approach
Explore Zero Trust security strategies for enterprise protection, moving beyond traditional perimeter defenses to role-based, defense-in-depth approaches for safeguarding virtual assets in the modern digital landscape.
QuadBlockQuiz - Supply Chain Sandbox Edition
Explore supply chain security through an interactive quiz and sandbox environment, enhancing your understanding of potential vulnerabilities and defensive strategies.
PwdLess - Exploitation Tales from RouterLand
Explore IoT device security through an attacker's perspective, covering fuzzing, reverse engineering, and exploit development. Learn about vulnerabilities, remote execution techniques, and challenges in IoT security.
Supply Chain Security in Critical Infrastructure Systems - CXO Panel Discussion
Panel discussion on supply chain security in critical infrastructure systems, featuring industry experts exploring challenges and strategies for protecting vital networks and systems from cyber threats.
Open Source is Insufficient to Solve Trust Problems in Hardware
Exploring hardware trust issues, supply chain vulnerabilities, and potential solutions. Introduces Betrusted, an open-source platform aiming to enhance security for high-risk individuals.

Peek into the Future - The Security Operations Center of 2020
Explore the evolution of cybersecurity threats and the future of Security Operations Centers, focusing on extended risk management across supply chains, ecosystems, and customer touchpoints.
SolarWinds - What Really Happened?
Insightful analysis of the SolarWinds cyberattack, revealing unique perspectives on the incident's details, methods, and perpetrators, with valuable lessons for enhancing industry-wide cybersecurity measures.
Supply Chain Security in the Software Era
Explore software supply chain risks and gain insights on mitigating them through real-world examples and concrete recommendations for policy makers and executives.
Supply Chain Unchained - How To Be A Bad SaaS
Explore software supply chain vulnerabilities, focusing on SaaS security. Learn about access control, API restrictions, maturity evaluation, logging, cloud security, and code integrity.
Your Critical System Is - Not? - Vulnerable - CSAF, VEX, SBOM and the Future of Advisories
Explore the future of vulnerability advisories with CSAF, VEX, and SBOM. Learn about critical system security, risk assessment, and automation in the evolving landscape of cybersecurity.
AppSec - From Outsiders to Allies
Chris Wysopal explores AppSec's evolution from hacker-driven to a critical ally in software development, emphasizing the need for collaboration, shared accountability, and integrated security practices in modern development processes.
US Local Connection - Increasing Supply Chain Security of Defense Contractors
Explore DoD's Cybersecurity Maturity Model Certification, its impact on contractors, and how Microsoft's cloud solutions support CMMC compliance for enhanced supply chain security.
Production SecOps with Kubernetes in Docker
Learn to secure Kubernetes deployments in Docker, covering architecture, attack vectors, supply chain security, and best practices for robust production environments.