Pwning the CI with GitHub Action Workflows - Security Challenges and Exploits
Explore GitHub Actions vulnerabilities and CI security risks. Learn to identify and mitigate potential exploits in workflows and configurations to safeguard your development pipeline.
Securing the IaC Supply Chain
Explore securing Infrastructure as Code supply chains, applying software security principles to IaC pipelines. Learn about Crossplane's integration with Sigstore for enhanced provenance and attestations.
Building Supply Chain Policies with Gatekeeper and Ratify
Learn to enhance Kubernetes security using Gatekeeper and Ratify for supply chain policy enforcement. Explore admission controllers, CRD-based policies, and external data verification for robust cluster protection.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks, featuring runtime security profiling and build verification techniques.
Interactive Playground to Learn Kubernetes and Cloud Native Security
Explore Kubernetes security through hands-on scenarios in a vulnerable cluster environment. Learn about real-world vulnerabilities, CVEs, and security tools across infrastructure, supply chain, and runtime layers.
Top 10 Istio Security Risks and Mitigation Strategies
Explore top Istio security risks and mitigation strategies for cloud native applications. Learn to prioritize efforts, protect against attacks, and address critical vulnerabilities in service mesh deployments.
Securing Self-Hosted GitHub Actions with Kubernetes and Actions-Runner-Controller
Explore secure deployment of self-hosted GitHub Actions runners using Kubernetes and actions-runner-controller. Learn about cluster settings, controller configurations, and runner pod security for regulated environments.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks. Learn about runtime security, build profiling, and verification techniques to protect your software development process.
How to Build a Kubernetes Admission Controller from Scratch - Tutorial
Learn to build a Kubernetes admission controller from scratch, exploring fundamentals, installation, and Python implementation. Gain hands-on experience in enhancing cluster security and policy enforcement.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
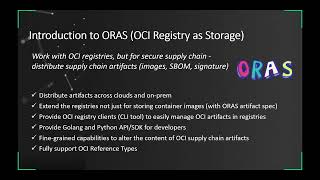
Secure Container Supply Chain with Notation, ORAS, and Ratify
Explore tools for securing container supply chains: Notation for signing artifacts, ORAS for distributing OCI artifacts, and Ratify for verifying container images.
Operating Tekton with Secure Defaults
Explore secure approaches for Tekton Pipelines, balancing flexibility with robust safeguards. Learn to implement Trusted Tasks and remote resource resolution for enhanced security in CI/CD workflows.
Container Security: Supply Chain, Authorization, and Runtime Protection
Explore container security: supply chain integrity, deployment authorization, and runtime protection. Experts discuss in-toto, TUF, Open Policy Agent, and container escape prevention.
Delivering Secure and Compliant Software Components with OCM and GitOps
Explore Open Component Model and GitOps for secure, compliant software delivery. Learn to automate deployment, enhance supply chain security, and manage artifacts in high-security environments.
A Checklist for Security from Container to Kubernetes - An End-to-End Overview
Comprehensive overview of container and Kubernetes security, covering lifecycle, supply chain, infrastructure, features, and potential attacks. Practical insights for robust cloud-native security implementation.
Enforcing a Secure Supply Chain on Kubernetes
Explore implementing and enforcing a secure supply chain in Kubernetes using open-source projects, including Sigstore keyless workflow and signature verification policies.
Notary - State of the Container Supply Chain
Explore container supply chain security with Notary v2, addressing challenges, discussing progress, and examining future roadmaps for enhanced artifact management and policy enforcement.
Scratch Containers and the Supply Chain Trouble
Explore scratch containers, their benefits in reducing vulnerabilities, and potential challenges in software composition analysis. Learn about security implications for containerized applications.
Cleaning up Vulnerable Images from Kubernetes Nodes
Explore Eraser, an open-source solution for automating the scanning and removal of vulnerable images from Kubernetes nodes, enhancing supply chain security in cloud-native environments.
Kubernetes Supply Chain Security - Building a Secure Software Factory
Explore Kubernetes supply chain security, software factory approaches, and defense strategies against attacks. Learn about signing, verification, and lessons from SUNBURST to enhance cloud-native security.
Open Tools for Secure Supply Chains in Kubernetes - From Release Engineering
Explore open-source tools for secure software supply chains, focusing on Kubernetes' journey to SLSA Level 3 compliance and how other projects can leverage these tools for enhanced security.