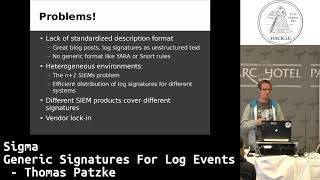
Sigma - Generic Signatures for Log Events
Explore generic signatures for log events with Sigma, a YAML-based format for sharing and converting log signatures across different SIEM systems and query languages.
Building the Super-Dynamic Demo Center
Modernize field sales engineering demos using Docker and CI pipeline for efficiency, flexibility, and new use cases. Transition from manual DevOps to Docker Service-based demo center with Swarm Mode and Splunk analytics.
How a Large Media Company Uses Splunk for Analytics-Driven Container Performance and Logging
Discover how BILD GmbH leverages Splunk for container performance monitoring, logging, and troubleshooting in their news portal infrastructure, offering insights for developers and operations teams.
Weaponizing Splunk - Using Blue Team Tools for Evil
Explore how Splunk, a popular security tool, can be exploited for malicious purposes. Learn about vulnerabilities, attack surfaces, and practical demonstrations of potential threats.
Cloud Threat Hunting
Proactive cloud threat detection techniques, including honeyclouds, integrated monitoring, and AI-driven behavioral analysis for mitigating orchestration attacks and cross-tenant threats.
Splunk for IR and Forensics
Explore Splunk's capabilities for incident response and forensics, including log analysis, dashboards, alerts, and statistical analysis for effective cybersecurity investigations.
Splunking the Clouds - Finding the Needle in AWS & Azure
Explore cloud security techniques for AWS and Azure, focusing on identifying and addressing potential vulnerabilities using Splunk's powerful data analysis capabilities.
Kafka on Kubernetes - From Evaluation to Production at Intuit
Explore Intuit's journey of running Kafka on Kubernetes in AWS, covering evaluation, testing, configuration, and integration with monitoring tools. Learn about challenges faced and solutions implemented.
Lessons Learned from Building and Running MHN - the World's Largest Crowdsourced Honeynet
Explore insights from managing the world's largest crowdsourced honeynet, covering architecture, community growth, and global attack patterns in cybersecurity.
Garbage in Garbage Out - Generating Useful Log Data in Complex Environments
Explore effective log data generation in complex environments, focusing on meaningful data, thresholds, and log management systems for improved security and analysis.
So You've Inherited a Security Department - Now What
Learn essential strategies for managing an inherited security department, covering OSINT tools, best practices, and key areas like compliance, user education, and vulnerability scanning.
Weaponizing Splunk - Using Blue Teams for Evil
Explore how attackers can exploit Splunk for malicious purposes, including data extraction and command control, in this eye-opening cybersecurity presentation.
Security Instrumentation - Be the Hero Getting Value from Security
Explore security instrumentation techniques to enhance organizational defenses, measure effectiveness, and demonstrate value in cybersecurity investments.
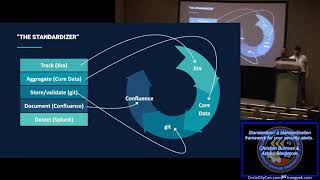
Standardizer - A Standardization Framework for Your Security Alerts
Learn about Standardizer, a framework for security alert standardization, covering metadata, core data, transformations, and application processes.
Finding the Issues in Microservices Applications
Discover techniques for identifying and resolving issues in complex microservices architectures using rich observability data, real-time analytics, and advanced monitoring tools.
Annotating Log Data for Machine Learning
Explore an NLP-based log analysis system for automated error triage and fault categorization, streamlining root cause analysis in complex log data.
Log Aggregation
Explore real-time log aggregation with Humio for efficient system monitoring. Learn about its unique features, query language, and advantages over alternatives for critical distributed systems.
Build-Time Auto-Instrumentation in Android Using OpenTelemetry
Discover how to implement OpenTelemetry's build-time auto-instrumentation for Android applications, exploring bytecode weaving techniques and client-side telemetry generation without manual code modifications.