SPDX 3.0 Overview - Introduction to Software Package Data Exchange
Explore the latest updates and enhancements in SPDX 3.0, the open standard for software bill of materials, and learn how it improves software supply chain transparency and security.
Open Source Security and Supply Chain Innovations - Keynote Sessions
Explore cutting-edge topics in open source security, including supply chain protection, Sigstore, SPDX, eBPF, SLSA, and memory safety, presented by industry leaders and experts.
Software Supply Chain with the Yocto Project
Explore software supply chain security using Yocto Project. Learn about SBOMs, reproducible builds, CVE tracking, and extending quality assurance for embedded Linux systems.
Complete Compliance Toolchain for Yocto Projects - Software Composition Analysis and SBOM Automation
Discover how to implement a comprehensive compliance toolchain for Yocto projects, featuring advanced tools like Fossology, Scancode, SPDX, and specialized solutions for managing large-scale software composition analysis.
Application of the Upcoming SPDX Safety Profile
Explore the SPDX Safety Profile for managing safety-critical projects, enhancing traceability, and maintaining documentation consistency across various tools and lifecycles.
SBOMs Go Global: Current State and Emerging Trends
Explore the global impact and emerging trends of Software Bill of Materials (SBOMs) with insights from industry expert Kate Stewart.
PEP 639 - Towards Licensing Standardization in Python Packaging
Explore PEP 639's proposal for standardizing license metadata in Python packaging, addressing current pitfalls and introducing SPDX syntax for improved clarity and consistency.
From Complexity to Clarity: Addressing Challenges in AI BOMs for Compliance
Explore strategies for implementing AI Software Bill of Materials (SPDX 3.0) to navigate compliance challenges and create accurate, machine-readable documentation for AI systems.
SBOM Implementation Reality: From Crawl to Walk - SPDX Lite Profile for the First Step
Discover how to create Software Bill of Materials (SBOMs) efficiently using SPDX Lite profile, featuring practical JSON examples and implementation strategies for meeting regulatory requirements in software supply chains.
Open Source Software Supply Chain Security - Understanding Threats and Best Practices
Explore critical threats to open source software supply chains, industry best practices for security, and practical strategies for protecting against vulnerabilities and cyberattacks.
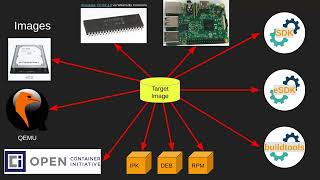
Software Bill of Materials (SBoM) and Supply Chain with the Yocto Project - Generating and Using SBoMs
Explore Software Bill of Materials generation, usage, and future in Yocto Project, emphasizing supply chain security and reproducible builds.
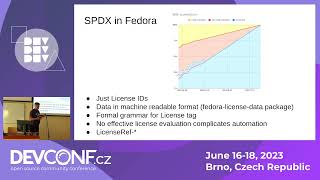
Software Bill of Materials (SBoM) for Dummies
Explore Software Bill of Materials (SBoM), its importance, and implementation in Fedora. Learn about US government mandates, hidden pitfalls, and the SPDX migration.
Case Study - 10+ Years of Developing an SBOM System - Dos and Don'ts
Explore the evolution of SBOM systems, key lessons learned, and best practices for implementation. Gain insights into various solutions and open-source tools for effective software component management.