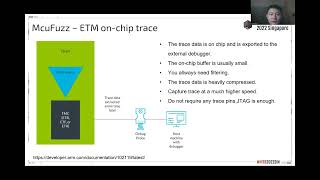
Fuzzing the MCU of Connected Vehicles for Security and Safety
Fuzzing techniques for MCU security in connected vehicles, using ARM ETM and code coverage-guided approach to enhance vulnerability detection and system robustness.
Burpsuite Team Collaborator - Enabling Collaborative App Testing
Explore collaborative app testing with Burpsuite Team Collaborator. Learn features, sharing capabilities, and see a live demo for enhanced security assessments and teamwork.
You're Just Complaining Because You're Guilty - A Guide for Citizens and Hackers to Adversarial Testing of Software Used in the Criminal Justice System
Explore adversarial testing of criminal justice software, empowering citizens and hackers to challenge and verify systems that impact lives and liberty.
Watching the Watchers - Exploiting Vulnerable Monitoring Solutions
Explore vulnerabilities in monitoring solutions and learn techniques to exploit them, enhancing your cybersecurity skills and understanding of potential risks in surveillance systems.
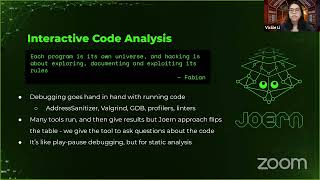
DIY Static Code Analyzer - Building Your Own Security Tools with Joern
Learn to build custom security tools using Joern for static code analysis, enhancing your ability to detect vulnerabilities and improve software security.
Introduction to Fuzzing
Explore the fundamentals of fuzzing, a powerful software testing technique, in this comprehensive workshop led by expert Dhiraj Mishra.
Logic Against Sneak Obfuscated Malware
Explore SMT solvers for binary analysis and code deobfuscation in IT security. Learn practical applications, limitations, and solutions for enhancing malware analysis capabilities.
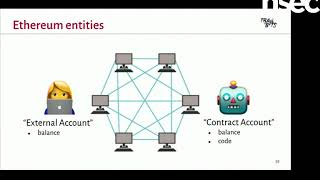
Binary Analysis, Meet the Blockchain
Explore symbolic execution for Ethereum smart contract analysis, addressing technical challenges and introducing Manticore, an open-source tool for enhancing contract security audits.
Researching the Unisoc Baseband
Exploring Unisoc baseband security: reverse-engineering and fuzzing LTE protocol stack to uncover vulnerabilities in budget smartphone chipsets, disrupting radio communication.
Reverse Engineering of Black Box Binaries with Symbolic and Concolic Execution Technique
Explore symbolic and concolic execution techniques to simplify reverse engineering of complex binaries. Learn to use the angr framework for efficient crackme solving and deobfuscation.
Zooming in on Zero Clicks Exploits
Dive into Zoom's security analysis, exploring reverse engineering challenges, large system understanding, and fuzzing techniques for non-relocatable binaries in video conferencing software.
Instrumenting System Applications on Android Images
Instrumenting Android system apps on stock images using Frida for dynamic analysis. Explores various approaches, their limitations, and a successful method for analyzing Google Play Protect Services.
PreVice - Static Detection of Hooking Capabilities in Machine Code
Explore static analysis techniques for detecting hooking capabilities in Windows executables, including Detours, import, and syscall hooking, with insights from scanning millions of files.
Meet Salinas - The First Ever SMS-Commanded Car Infotainment RAT
Discover how researchers created the first SMS-controlled malware for car infotainment systems, exploring vulnerabilities and potential threats in modern vehicle technology.
Pwning Intel PIN
Exploring vulnerabilities in Intel PIN's dynamic binary instrumentation framework, challenging assumptions of isolation and stealthiness, and demonstrating potential security risks in instrumented programs.
Sum Total of ISA Knowledge - Analyzing Your Binary Analysis Tools
Explore techniques to measure and verify architecture support in binary analysis tools, enhancing firmware reverse engineering through selective application of dynamic analysis methods.
Sandbagility - Reverse Engineering Framework for Windows Dynamic Analysis
Hybrid framework for Windows malware analysis combining dynamic and sandbox approaches. Offers stealthy, adaptive solution to reduce analysis time, demonstrated with WannaCry case study.
Rattle - An Ethereum EVM Binary Analysis Framework
Explore Rattle, an innovative framework for analyzing Ethereum smart contracts, enhancing auditability and security in blockchain interactions through advanced binary analysis techniques.
Under the Hood of Wslink Multilayered Virtual Machine
Análisis detallado de la máquina virtual multicapa Wslink, explorando técnicas de ofuscación avanzadas y presentando un enfoque semiautomático para desobfuscar el malware de forma eficiente.
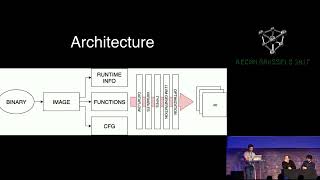
Analyzing iOS Apps - Road from AppStore to Security Analysis Report
Toolset for detecting vulnerabilities in iOS apps: download and decrypt, decompile, statically analyze, and present results. Focuses on high-level semantics reconstruction and common mobile app security flaws.
Using WPP and TraceLogging Tracing to Facilitate Dynamic and Static Windows
Explore advanced Windows tracing techniques using WPP and TraceLogging for enhanced dynamic and static analysis in cybersecurity investigations.