Defeating the Transparency Feature of DBI
Techniques to break transparency in dynamic binary instrumentation tools, exposing limitations and enabling detection of analysis environments for malware and binary applications.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.
Dynamic Flash Instrumentation for Fun and Profit
Explore dynamic analysis of malicious Flash files using binary instrumentation, enabling faster and more detailed automatic analysis without decompilation.
Contemporary Automatic Program Analysis
Explore automatic program analysis techniques for vulnerability discovery, from historical context to cutting-edge methods, with practical examples and demos for effective security research.
Runtime Analysis of Vulnerabilities and Generation of Exploits
Runtime analysis tool for detecting vulnerabilities and generating exploits. Leverages program execution to identify dataflows, usable for both offensive and defensive purposes. Includes live demonstrations and open-source release.
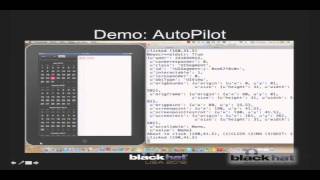
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.
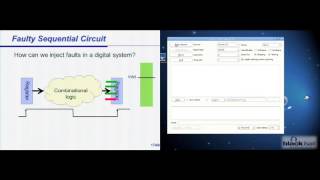
Torturing OpenSSL
Explore hardware vulnerabilities in secure systems through a side-channel attack on RSA signatures, demonstrating how induced faults can compromise software-secure systems and extract private keys.
File Disinfection Framework - Striking Back at Polymorphic Viruses
Explore an open-source framework for combating polymorphic viruses through advanced static analysis and emulation. Learn innovative techniques for file disinfection, malware analysis, and incident response.
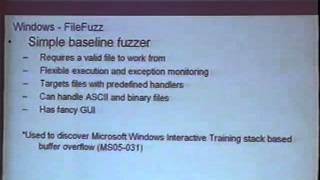
The Art of File Format Fuzzing
Explore advanced techniques for file format fuzzing, uncovering vulnerabilities in software applications through systematic input manipulation and analysis.
Appliance Firewalls - A Detailed Review
Comprehensive review of network firewall appliances, examining features, vendor claims, and real-world test results of nearly two dozen devices. Uncovers truths behind marketing promises.
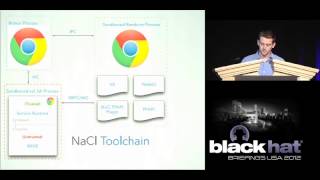
Google Native Client - Analysis of a Secure Browser Plugin Sandbox
Explore Google's Native Client sandbox for Chrome, its architecture, security features, and potential vulnerabilities. Learn about PPAPI and a tool for fuzzing PPAPI interfaces.
Web Application Brute Forcing 101
Learn techniques for web application brute forcing, exploring vulnerabilities and security measures to protect against unauthorized access attempts.
How to Grow a TREE from CBASS
Innovative binary analysis toolset for cross-platform programs. Integrates with IDA Pro, enabling interactive visualization and on-demand analysis for efficient reverse engineering and vulnerability detection.
Dude, Where's My Laptop?
Analysis of laptop and mobile device security solutions, exploring their effectiveness against theft and data protection claims. Reveals vulnerabilities and challenges common anti-theft measures.
When Security Gets in the Way - Pen Testing Apps That Use Certificate Pinning
Explore tools and techniques for defeating certificate pinning in mobile apps during black-box testing, enabling interception of SSL traffic on both iOS and Android platforms.
Detecting Bugs Using Decompilation and Data Flow Analysis
Explore Bugwise, a free online service for detecting software bugs through decompilation and data flow analysis, showcasing its success in finding vulnerabilities in Debian Linux.
Hunting the Shadows - In Depth Analysis of Escalated APT Attacks
In-depth analysis of APT attacks targeting Taiwan, showcasing automated detection systems, forensic techniques, and insights into attacker operations. Includes release of collaborative APT classification platform.
BinaryPig - Scalable Malware Analytics in Hadoop
Scalable malware analytics framework using Hadoop for processing large volumes of malware samples. Enables efficient feature extraction, machine learning, and data exploration for security researchers.
Abusing Web APIs Through Scripted Android Applications
Exploiting Android app vulnerabilities to abuse web APIs, using JRuby for scripting and Burp Suite for testing. Demonstrates attacks bypassing security measures and exposes potential weaknesses in mobile app ecosystems.
AMF Testing Made Easy
Reshaping AMF fuzzing with automated gray-box testing. Learn to build custom AMF messages, dynamically generate objects, and improve fuzzing coverage for complex applications using the Blazer Burp Suite plugin.
Fixing - Making Holes in Binaries
Explore techniques for modifying binary files to fix vulnerabilities or create new exploits. Learn about reverse engineering and binary manipulation for security research.