A Hacker's Guide to Reducing Side-Channel Attack Surfaces Using Deep Learning
Explore deep-learning techniques to identify and reduce side-channel attack vulnerabilities, leveraging AI explainability for efficient implementation assessment and improved security.
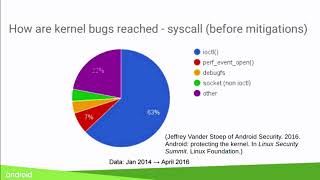
DIFUZE - Android Kernel Driver Fuzzing
Explore Android kernel driver fuzzing with DIFUZE, a tool for identifying vulnerabilities in third-party driver code. Learn techniques to improve Android security infrastructure and discover potential weaknesses.
Code Deobfuscation - Intertwining Dynamic, Static and Symbolic Approaches
Explore advanced code deobfuscation techniques combining dynamic, static, and symbolic approaches to enhance software analysis and reverse engineering capabilities.
Command Injection in F5 iRules
Explore command injection vulnerabilities in F5 iRules, focusing on syntax, exploitation techniques, and security implications for BigIP F5 products used in high-performance web traffic routing.
The Crash Course - A Non-Programmer's Guide to Fuzzing
Hands-on workshop for non-programmers to learn fuzzing techniques. Covers environment setup, tools like AFL and Honggfuzz, instrumentation, input selection, and crash analysis. Suitable for beginners to intermediate level.
Security Research and Disclosure - The Unauthorized Biography
Explore the evolution of security research and disclosure, from historical "unbreakable locks" to modern challenges in IoT, blockchain, and AI, with insights on ethical hacking and vulnerability reporting.
Bug Bounty - Why Is This Happening
Explore bug bounty programs' challenges and realities from multiple perspectives, offering insights into their evolution, limitations, and potential for improvement in cybersecurity.
Unleashing D* on Android Kernel Drivers
Explore techniques for detecting vulnerabilities in Android kernel drivers using static analysis and fuzzing, with focus on DR.CHECKER and DIFUZE tools.
Drone Hijacking and Other IoT Hacking with GNU Radio and SDR
Explore IoT security vulnerabilities using SDR and GNU Radio. Learn to intercept, sniff, and hijack wireless devices like drones and keyboards through practical demonstrations and attacks.
Clusterfuzz
Explore Chrome's open-source Clusterfuzz system for real-time security bug detection, distributed fuzzing techniques, and insights into exploitable crash prevention across platforms.
Fuzzing the Easy Way Using Zulu
Explore fuzzing binary protocols with Zulu, a GUI-based tool for easy capture, mutation, and replay. Learn its features and successful bug-finding applications.
O'Dea Assertions Untwining the Security of the SAML Protocol
Explore SAML protocol security, including XML signature attacks, attribute implementation, and fuzzing techniques. Learn to identify and mitigate vulnerabilities in SSO systems.
SMS to Meterpreter - Fuzzing USB Modems
Explore innovative attacks on USB data modems, including fuzzing techniques and SMS payload execution. Learn about vulnerabilities, reverse engineering, and USB sniffing for offensive security research.
Smarter Ways to Gain Skills
Explore innovative approaches to skill acquisition in cybersecurity, including apprenticeship models, mind maps, and data-driven learning, as presented at BSidesPhilly 2017.
Aiding Static Analysis - Discovering Vulnerabilities in Binary Targets through Knowledge Graph
Explore advanced techniques for vulnerability detection in binary targets using knowledge graphs, static analysis, and specialized tools like Binary Ninja and Kraken.
Bug Hunting in RouterOS
Explore RouterOS vulnerabilities, including developer backdoors, key negotiation, and protocol analysis. Learn about CVEs and policy discovery techniques for enhanced network security.
Android App Penetration Testing 101
Learn Android app penetration testing essentials, including tools, methodologies, and practical techniques for identifying vulnerabilities and securing mobile applications.
Subverting Trust in Windows - A Case Study of the How and Why of Engaging in Security Research
Explore Windows security research through a case study on subverting trust, covering dynamic analysis, code signatures, and PowerShell, with insights on validating trust and lessons learned.
Building Unity Projects with Unity Cloud Build
Discover Unity Cloud Build's automated app building, testing, and distribution features for streamlined game development and efficient team collaboration.
Strangling the Monolith - Applied Patterns & Practices from the Trenches
Practical strategies for incrementally modernizing legacy systems, focusing on the strangler pattern, domain-driven design, and team topologies to evolve towards a reactive architecture.
Programming’s Greatest Mistakes
Explore programming's greatest mistakes, from exploding rockets to bankrupting companies, in this humorous and informative talk about costly errors and their consequences.