Do Certain Types of Developers or Teams Write More Secure Code?
Explore factors influencing secure code development, including team dynamics, developer experience, and human factors. Gain insights into improving software security practices.
SBOM SmackDown - Conquering Software Supply Chain Risks with OWASP CycloneDX
Explore Software Bill of Materials (SBOM) and learn how OWASP CycloneDX standard enhances software supply chain transparency, enabling better risk-based decisions and compliance with government mandates.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
OWASP CycloneDX - Software Bill of Materials Standard
Explore OWASP CycloneDX, a lightweight software bill of materials (SBOM) standard, with experts Steve Springett and Patrick Dwyer. Learn about its features, applications, and importance in modern software development.
OWASP Dependency Track - Software Composition Analysis and Vulnerability Management
Explore OWASP Dependency Track: manage software components, analyze vulnerabilities, and enhance security with features like Software Bill of Materials, policy engine, and dependency graphs.
What Shall We Do With a Vendor SBOM? - Understanding Software Bill of Materials
Explore the practical applications of Software Bill of Materials (SBOM) in cybersecurity, covering procurement, vulnerability disclosure, threat intelligence, and forensics.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
Scaling Security in Leading Companies - DevOps and CI/CD Best Practices
Discover pro-tips and actionable lessons from mature security teams on scaling security in modern software development. Learn effective strategies for buy-in, engineering projects, analysis integration, and production monitoring.
Don't Feed the Hippos - Improving Security Communication with Developers
Explore common security communication failures and learn effective strategies for collaborating with developers to address software vulnerabilities and enhance overall security practices.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
Secure Coding Lessons for Mobile Apps - Insights from the Trenches
Explore common mobile app coding pitfalls, their real-world impacts, and learn effective strategies to enhance security. Includes demonstrations of attacker techniques and protective code samples.
Trusted Types: End-to-End Injection Safety at Scale
Learn about Google's approach to achieving high-level XSS safety through integrated tools and developer-friendly practices, with insights on implementing similar security in open-source stacks.
Looking Towards the Future of Open Source Vulnerability Management
Explore the evolving landscape of open source security, focusing on vulnerability management strategies, industry trends, and best practices for effective remediation and continuous security integration.
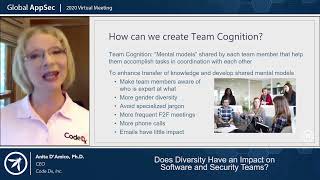
Impact of Diversity on Software and Security Teams
Explore the impact of diversity on software and security teams, examining its influence on team dynamics, problem-solving, and overall effectiveness in the tech industry.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
DevSecOps in 2031: How Robots and Humans Will Secure Apps Together
Explore the future of DevSecOps in 2031, where humans and robots collaborate to secure applications. Learn about AI pair programming and innovative approaches to tackle evolving cybersecurity challenges.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
Automated Security Testing With OWASP Nettacker
Learn automated security testing techniques using OWASP Nettacker, a powerful open-source tool for vulnerability assessment and information gathering in web applications and networks.