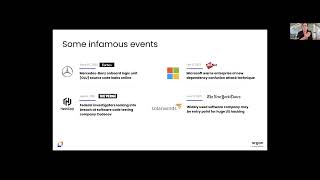
Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
Evolving Threat Modeling Through the Open Threat Model Format
Explore the Open Threat Model Format and its role in advancing threat modeling practices for improved cybersecurity risk assessment and mitigation strategies.
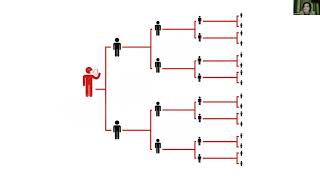
Reducing Software Vulnerability at a Global Scale
Explore strategies for reducing software vulnerabilities on a global scale, leveraging collective efforts of millions to enhance cybersecurity and protect digital ecosystems.
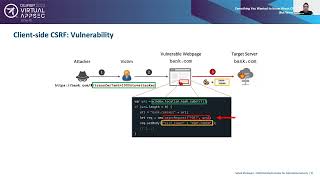
Everything You Wanted to Know About Client-Side CSRF But Were Afraid to Ask
Explore client-side CSRF vulnerabilities, detection challenges, and advanced analysis techniques using hybrid property graphs for improved web application security.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
The Power of DevSecOps in Web3 and Blockchain
Explore DevSecOps principles in Web3 and blockchain, focusing on security integration for decentralized applications and smart contracts development.
Vulnerabilities as Ingredients and OWASP Top 10 as Seasoning
Explore how vulnerabilities and OWASP Top 10 interact in application security, using a culinary analogy to demystify complex concepts and enhance understanding of secure development practices.
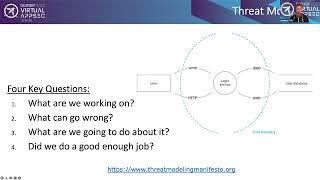
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.
Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
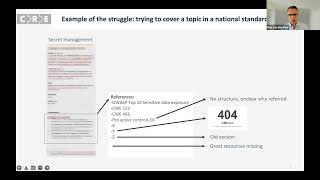
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
Security Begins with Secure Development Environments
Explore supply chain security threats in development environments, focusing on vulnerabilities in Visual Studio Code extensions and their potential for remote code execution.
Scaling AppSec through Education
Strategies for scaling application security through developer education, addressing the imbalance between security teams and developers and emphasizing code review for early bug detection.
AppSec Champions Programs - Best Practices and Survey Results
Explore AppSec champions programs: research findings, best practices, and strategies for influencing developers to write secure code. Learn to implement and improve these programs in your organization.
Five Philosophies for Building Better Application Logs
Discover five philosophies for creating application logs that enhance breach readiness and forensic capabilities, empowering developers to build more secure and analyzable systems.
Top Ten Proactive Controls for Secure Software Development
Explore essential software security controls for developers, covering authentication, access control, validation, and more. Learn proactive strategies to build robust, secure applications.
Telecom User Group and Cloud Native Network Functions Testbed - Introduction and Deep Dive
Explore the evolution of telecom network functions to cloud-native, discussing challenges, architecture, and performance testing in Kubernetes environments.
Automotive Industry Collaboration Through Open Source Development - Panel Discussion
Automotive industry leaders discuss the benefits and challenges of open source development, its impact on product innovation, and the need for increased collaboration to drive the industry forward.
How to Govern and Maintain Compliance Using Open Source Identity Management Components
Explore open-source identity management with midPoint for efficient governance, compliance, and automation. Learn integration, role-based access control, and advanced features through practical scenarios and demos.
The Interoperability Challenge in Telecom and NFV Environments
Explore interoperability challenges in telecom and NFV, covering ETSI NFV testing, NIA campaigns, vendor collaboration, and OpenStack's role. Learn about latest developments and how to contribute.