Securing Software That Will Change the World
Explore innovative technologies and learn strategies to secure software that will shape the future. Gain insights from global engineers on protecting transformative systems.
Human vs AI: How to Ship Secure Code
Discover how AI tools like GitHub Copilot and ChatGPT can enhance secure coding practices through real-world examples, tips, and best practices for developers.
Zero Trust Principles in DevSecOps
Explore Zero Trust security principles in DevSecOps, focusing on continuous verification, automated tools, and real-time threat detection. Learn implementation strategies and cultural shifts for improved security.
The Impact of Policy-as-Code on the Software Supply Chain
Explore DevSecOps principles for securing the software supply chain. Learn to automate, version, and implement controls as code for resilient software ecosystems.
A Glimpse into DevSecOps - Building a Secure NodeJS Service
Explore DevSecOps through building a NodeJS service, focusing on security integration throughout development and deployment. Learn practical insights and best practices for robust, secure software creation.
DevSecOps Unveiled: Integrating Security in the Development Lifecycle
Explore DevSecOps principles and practices for seamlessly integrating security into the development lifecycle. Learn to foster collaboration, automation, and shared responsibility for proactive vulnerability management.
SLSA: Enhancing Software Supply Chain Security - More Than Just a Garnish for Your Pipelines
Explore SLSA principles for securing software supply chains. Learn threat models, security levels, and how to contribute to this OpenSSF project for enhanced DevSecOps processes.
Building Your First DevSecOps Pipeline
Demystify DevSecOps and build a functional pipeline with cutting-edge security testing, including SCA, SAST, and DAST tooling. Supercharge software security and achieve true "Shift Left" success.
5 Open Source Security Tools All Developers Should Know About
Discover five essential open-source security tools for CI/CD pipelines. Learn to integrate SAST, secrets detection, SCA, IaC security, and DAST with practical code examples and demos.
Securing Applications in SDLC and Cloud-Native Web and API Protection - Sessions 1 and 2
Learn secure coding practices, identify vulnerabilities, and integrate security into SDLC. Explore cloud-native WAAP for effective web app and API protection using machine learning.
Securing Applications in the Software Development Life Cycle (SDLC) - Beginner
Aprenda prácticas de codificación segura para mitigar riesgos de seguridad y proteger datos en el desarrollo de software moderno.
Software Supply Chain Attacks - Understanding Risks and Prevention
Explore software supply chain attacks: their nature, prevalence, types, recent examples, and best prevention practices. Gain insights into associated risks and protective measures.
Software Supply Chain Security - Key Terms, Players, and Projects - Part 2
Explore key terms, players, and projects in software supply chain security. Gain insights on open-source visibility, SBOMs, and initiatives addressing complex security challenges in the open-source pipeline.
Tackling Software Supply Chain Security as an Organization - Episode 128
Explore organizational approaches to software supply chain security with experts discussing solutions, initiatives, and best practices for managing risks and improving visibility.
Software Supply Chain Security: Definition and Importance - Episode 1
Explore the key pillars of software supply chain security in this comprehensive podcast episode. Gain insights into problem definition, essential terms, and practical implementation strategies for enhancing your organization's security posture.
Malicious Packages and Malicious Intent - Episode 123
Explore malicious attacks, open source security, and practical tips for improving company safety with Liran Tal, director of developer advocacy at Snyk and Github Star.
Detection as Code - Buzzword or Panacea?
Explore the reality of Detection-as-Code in cybersecurity. Separate hype from facts and understand its potential benefits for blue teams and threat detection programs.
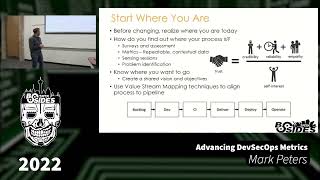
Advancing DevSecOps Metrics - Creating a Clear Path to Improved Performance
Integrate a clear path to improved performance by advancing DevSecOps metrics. Learn to deconstruct core metrics for accelerated delivery and increased customer value.
Why You Can Still Get Hacked Even After Signing Your Software Artifacts
Explore artifact poisoning tactics in software supply chains and learn prevention methods, including secure artifact signing, to protect your CI/CD pipeline from malicious injections.
Defense in Depth: Refocusing on Defensive Security Techniques
Explore defensive product security techniques, emphasizing defense-in-depth and supply chain security. Learn key aspects to consider in your application security strategy.
Breaking Chains: Overcoming Impostor Syndrome in Open Source Contributions
Discover strategies to overcome impostor syndrome and confidently contribute to open source projects. Learn to break mental barriers and unleash your potential in the tech community.