Keynote on Web Application Security
Insightful keynote address exploring cutting-edge cybersecurity trends, challenges, and strategies in the rapidly evolving digital landscape.
Building Secure Containers for Mobile Devices
Explore secure container solutions for BYOD environments, covering application wrapping, design challenges, iOS runtime analysis, and implementation best practices for mobile data protection.
AppSec at DevOps Speed and Portfolio Scale
Explore a revolutionary approach to application security using passive sensors for real-time vulnerability detection, enhanced architecture, and proactive collaboration across entire IT portfolios.
Verifying Software for Security Bugs - Dynamic Analysis and Fuzzing Testing
Learn dynamic analysis and fuzzing techniques to verify software security, including mitigations and vulnerability checks. Explore BinSecSweeper, an open-source tool for binary analysis on Windows and Linux.
OWASP Hackademic - Teaching Application Security Through Practical Challenges
Practical environment for teaching application security through realistic scenarios with known vulnerabilities. Students discover and exploit vulnerabilities, gaining hands-on experience from an attacker's perspective.
Dynamic Source-Sink Analysis for Java Applications - From the Ground Up
Dynamic source-sink analysis for Java applications to detect security vulnerabilities, aimed at developers for use during development, not production. Demonstrates live detection of issues like log manipulation.
IEEE Computer Society's Center for Secure Design - Helping Design More Secure Software
Explore common software design flaws and learn strategies to create more secure applications with insights from the IEEE Computer Society's Center for Secure Design workshop.
11,000 Voices - Experts Shed Light on 4-Year Open Source and AppSec Survey
Experts discuss findings from a 4-year study on open source security practices, revealing surprising trends in policy enforcement, vulnerability tracking, and organizational preparedness for security threats like Heartbleed.
AppSec Training Program Fine-Tuning Based on Survey Data - OWASP AppSecUSA 2014
Explore data-driven insights on AppSec training effectiveness, developer awareness, and learning preferences to optimize security programs and enhance defensive coding practices.
BSIMM: A Decade of Software Security Evolution - Keynote
Explore the evolution of software security over a decade, from early concepts to modern practices, highlighting the BSIMM framework for measuring and improving security initiatives in software development.
AppSecUSA 2014 - Breakers Track Sessions
Explore cutting-edge web and mobile security topics, including mobile attacks, use-after-free exploitation, static analysis, runtime manipulation, and top hacking techniques from AppSecUSA 2014.
Continuous Security Testing in DevOps Environments
Explore continuous security testing in DevOps, addressing challenges and presenting an open-source framework using Behavior Driven Development for effective communication and automation.
Leveling Up an Application Security Program
David Rook shares insights on enhancing application security at Riot Games, covering assessment, implementation of controls, secure coding guidance, and maintaining a security community in a fast-paced environment.
Fix the Damned Software - Improving Application Security Design
Explore strategies for building security into software development, moving beyond vulnerability discovery to secure design and implementation. Learn from industry experience and BSIMM data.
Static Analysis for Dynamic Assessments - OWASP AppSecUSA 2014
Explore techniques for using static analysis tools in dynamic web vulnerability assessments without source code, enhancing detection of security weaknesses in complex applications.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
Adventures in Reviewing Mountains of Code
Explore strategies for efficiently reviewing large codebases, including experiments, tools, and unexpected challenges encountered during a 2.6 million line code assessment.
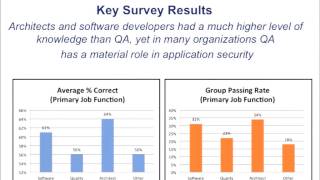
Can AppSec Training Really Make Developers Security-Smart?
Explore the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and practical application in software security programs.
Surviving an Application DoS - Strategies and Open Source Defense Framework
Explore strategies to defend against Application-Level DoS attacks using a new open-source Node.js framework. Learn to identify threats, analyze traffic patterns, and implement active defense measures.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
NIST Missions and Impacts on US Industry, Economy, and Citizens - Lecture
Explore NIST's mission, impact on US industry, and cybersecurity initiatives. Learn about current programs, projects, and R&D activities in this premier scientific institution.