Building a Secure Future: Lessons from Past and Present Information Security Challenges
Explore the future of information security, examining past lessons, current challenges, and emerging technologies like quantum cryptography to build a more secure digital world.
Software Supply Chain Lifecycle Management: Reducing Attack Vectors and Enabling Rugged DevOps
Exploring software supply chain lifecycle management to reduce attack vectors and enable rugged DevOps, focusing on IoT security, third-party software risks, and standards-based automation for threat detection.
Increasing Web Security with the Power of HTTP Headers
Explore how HTTP headers can enhance web security, focusing on practical implementation strategies and best practices for developers and security professionals.
Pentesting Voice Biometrics Solutions - AppSec EU 2017
Explore pentesting techniques for voice biometrics, including tools for IVR automation, voice fuzzing, and bypassing algorithms. Learn security requirements and compare with traditional password methods.
Combining Security Risks of Native and Web Development in Hybrid Apps - AppSec EU 2017
Explore security risks in hybrid app development, combining native and web technologies. Learn defensive programming and testing strategies for secure cross-platform mobile applications.
How to Slay a Dragon - A Three-Step Strategy for Solving Complex Security Problems
Discover a three-step strategy for tackling complex security challenges in Chrome, focusing on incremental progress, accepting imperfections, and considering long-term costs.
OWASP Zap - Introduction and Usage Guide
Explore OWASP Zap's capabilities for web application security testing with David Scrobonia's comprehensive overview, highlighting key features and best practices for effective vulnerability detection.
Threat Model-as-Code: Integrating Security into the Software Development Lifecycle
Integrating threat modeling into software development lifecycle using "Automaton" framework, enabling actionable outputs and automated security testing for improved product security.
Empowering the Employee - Incident Response with a Security Bot
Explore how a Slack bot engages employees in incident response, enhancing security awareness and efficiency while providing valuable insights for quick, appropriate action.

Identity Theft: Attacks on SSO Systems
Explore vulnerabilities in SAML-based SSO systems, including XML signature attacks and user directory flaws. Learn how these issues can lead to identity theft and authentication bypasses in modern organizations.
Monitoring Application Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface evolution, and learn to integrate security testing into CI/CD pipelines using metrics-based policies.
Embedding GDPR into the Software Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, threat modeling, and breach notification processes.
Securing C Code That Seems to Work Fine
Explore strategies for securing C codebases in high-performance environments, balancing best practices with startup culture. Learn from real-world successes and failures in implementing application security controls.
Detecting CSRF Vulnerability Reliably - Programmatic Approach
Explore a programmatic approach to reliably detect CSRF vulnerabilities in web applications, overcoming common shortcomings of existing tools and improving automated security testing.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.
Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
A Seat at the Table: Effective Security Collaboration in DevOps - AppSecCali 2019
Discover effective collaboration strategies for security professionals in the DevOps era, focusing on new skills, approaches, and speed to engage early and add value in software development.
Baking Security Into the Software Development Lifecycle - CISO Panel
CISOs discuss strategies for integrating security into rapid application development, sharing real-world experiences on managing evolving methodologies and pressures to publish securely.
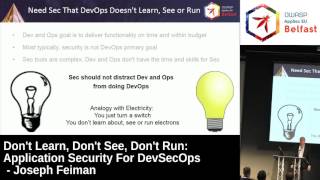
Application Security for DevSecOps - Don't Learn, Don't See, Don't Run
Explore the future of DevSecOps with insights on seamless security integration, emerging technologies, and adoption strategies for the next three years in application development.
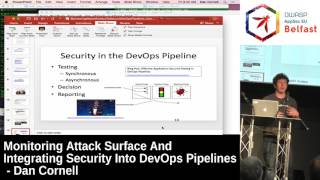
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface, and learn to integrate security testing into CI/CD pipelines for effective DevOps practices.