The Missing Link: How to Collect and Leverage Software Bill of Materials (SBOMs)
Discover how Schneider Electric efficiently manages software security through SBOM collection and implementation, with real-world examples from Log4j and OpenSSL vulnerability responses.
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.
Inside Llama 3 Red Team Process - AI Safety and Security Assessment
Delve into Meta's AI Red Team's comprehensive approach to testing Llama 3's safety, exploring methodologies, automated attacks, and emerging security challenges in AI systems.
Reflections on a Decade in Bug Bounties - From Novice to Seasoned Hunter
Gain insights into the evolution of bug bounty hunting through a decade-long journey, from basic vulnerability reporting to crafting critical impact chains, with perspectives from both hunter and triage sides.
QuickShell: Remote Code Execution Attack Chain Analysis in Quick Share
Uncover critical security vulnerabilities in Google's Quick Share protocol, including an RCE attack chain, HTTPS MITM techniques, and protocol analysis for both Windows and Android platforms.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.
WHAD: A Framework for Wireless Protocol Hacking and Analysis
Discover WHAD, a versatile framework for wireless protocol hacking that enables hardware interoperability and simplified tool development for security researchers exploring wireless vulnerabilities.
Using Testcontainers for Better Integration Tests in Java Microservices
Discover how to create robust integration tests using Testcontainers framework, enabling independent testing of Java microservices with Docker-based infrastructure services like databases and message brokers.
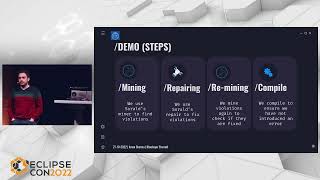
Automated Static Analysis Warning Resolution Using Software Bots - A Sorald Demo
Discover how to automate fixing SonarQube violations using Sorald, a software bot that monitors GitHub repositories and submits patches through pull requests, streamlining code maintenance.
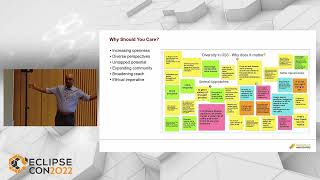
Open Source Code of Conduct - Building Inclusive Technology Communities
Discover how Open Source Codes of Conduct foster inclusive tech communities, promote diversity, and create welcoming environments for all contributors, especially underrepresented groups.
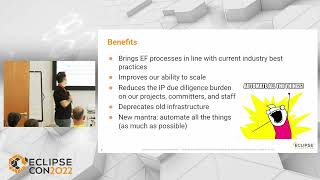
Revising the Eclipse Foundation's Intellectual Property Due Diligence Process
Discover the modernized IP due diligence tools and processes at Eclipse Foundation, streamlining license compliance and reducing manual effort for project committers through automated solutions.
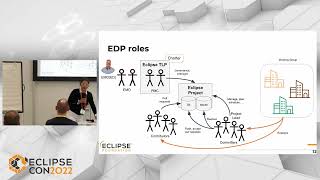
Eclipse Development Process: Creating and Managing Open Source Projects
Discover the essential steps and workflows of creating and managing open source projects at Eclipse Foundation, including specifications, releases, and community engagement processes.
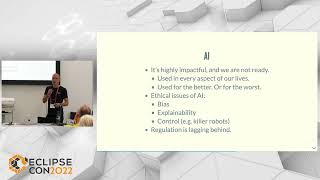
Software Ethics in a Software World - Understanding Ethical Implications in Software Development
Explore the critical landscape of software ethics, its impact on daily life, and how developers can foster responsible practices for building a better digital world.
Open Source Software Supply Chain Security - Understanding Threats and Best Practices
Explore critical threats to open source software supply chains, industry best practices for security, and practical strategies for protecting against vulnerabilities and cyberattacks.
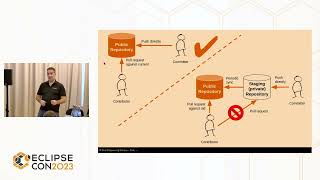
Intellectual Property Due Diligence at Eclipse - Past, Present and Future
Explore the evolution and significance of Eclipse Foundation's IP due diligence process, from historical challenges to current practices and future improvements in open source software compliance.
What's New in PDE - From Manifest-First to Code-First
Discover how to transition from manifest-first to code-first development in PDE, exploring OSGi annotations, automated manifest generation, and seamless project conversion strategies.
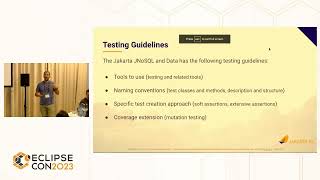
Data-Driven Testing with Jakarta Persistence Specifications and NoSQL
Master data-driven testing techniques using Jakarta Persistence, exploring JUnit Jupiter, AssertJ, and TestContainer frameworks to create robust domain-driven tests with NoSQL technologies.
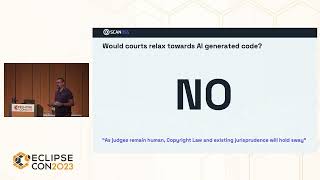
Open Source Licensing in the Era of AI-Assisted Coding
Explore the intersection of AI-assisted coding and open source licensing, focusing on compliance challenges, risk management, and practical solutions for modern software development.
Migrating Eclipse Trace Compass to VSCode Extension for Theia
Explore the migration journey of Trace Compass from Eclipse plug-in to VSCode extension, examining architectural changes, challenges, and future possibilities for enhanced trace visualization capabilities.
From Fragmentation to Connection - Building Bridges Across Communities with Chat Services
Discover how Matrix chat service bridges development communities, enabling seamless collaboration through federation, bridges, and integration with CI/CD tools and IDEs for more effective open-source contributions.
High-Performance Graphical View Filtering with Sprotty - Techniques for Information Visualization
Discover techniques for optimizing graphical network visualizations using Sprotty, focusing on smart filtering, nested graphs, and client-side performance optimization for complex data representation.