Why AI-Generated Talk Abstracts Were Rejected for NDC Oslo
Discover why AI-generated talk abstracts were rejected at NDC Oslo. Gain insights into effective abstract writing and understand the importance of human creativity in conference submissions.
Practical Tips for Defending Web Applications in the Age of DevOps
Practical tips for adapting application security to modern DevOps practices, covering static analysis, dynamic scanning, and security visibility for rapid development cycles.
Quantifying Risk in Consumer Software at Scale - Consumer Reports' Digital Standard
Explore methodologies for quantifying software security risks, predicting vulnerabilities, and evaluating consumer products using the Digital Standard developed by Consumer Reports and CITL.
Defeating the Transparency Feature of DBI
Techniques to break transparency in dynamic binary instrumentation tools, exposing limitations and enabling detection of analysis environments for malware and binary applications.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.
Dynamic Flash Instrumentation for Fun and Profit
Explore dynamic analysis of malicious Flash files using binary instrumentation, enabling faster and more detailed automatic analysis without decompilation.
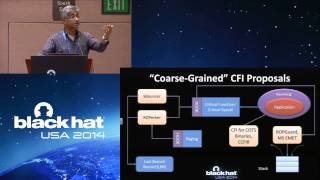
The Beast is in Your Memory
Explore advanced exploitation techniques and control-flow integrity mechanisms. Learn about Return-Oriented Programming, its countermeasures, and how to bypass emerging CFI solutions.
Contemporary Automatic Program Analysis
Explore automatic program analysis techniques for vulnerability discovery, from historical context to cutting-edge methods, with practical examples and demos for effective security research.
Building Safe Systems at Scale - Lessons from Six Months at Yahoo
Insights on building secure systems for large-scale internet companies, addressing challenges of surveillance, user privacy, and evolving security threats in the digital landscape.
Runtime Analysis of Vulnerabilities and Generation of Exploits
Runtime analysis tool for detecting vulnerabilities and generating exploits. Leverages program execution to identify dataflows, usable for both offensive and defensive purposes. Includes live demonstrations and open-source release.
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.
Torturing OpenSSL
Explore hardware vulnerabilities in secure systems through a side-channel attack on RSA signatures, demonstrating how induced faults can compromise software-secure systems and extract private keys.
File Disinfection Framework - Striking Back at Polymorphic Viruses
Explore an open-source framework for combating polymorphic viruses through advanced static analysis and emulation. Learn innovative techniques for file disinfection, malware analysis, and incident response.
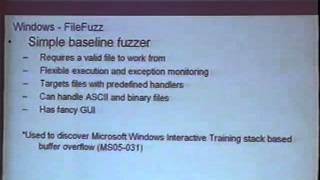
The Art of File Format Fuzzing
Explore advanced techniques for file format fuzzing, uncovering vulnerabilities in software applications through systematic input manipulation and analysis.
Injection Flaws - Stop Validating Your Input
Explore injection flaws and learn why input validation alone is insufficient for security. Discover effective strategies to protect against these vulnerabilities in web applications.
CISO Q&A with Jeff Moss
Insightful CISO panel discussion exploring top security challenges, industry trends, and emerging threats in cybersecurity landscape. Covers certifications, zero-day research, and open source risks.
Appliance Firewalls - A Detailed Review
Comprehensive review of network firewall appliances, examining features, vendor claims, and real-world test results of nearly two dozen devices. Uncovers truths behind marketing promises.
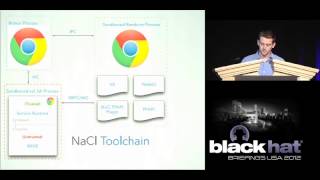
Google Native Client - Analysis of a Secure Browser Plugin Sandbox
Explore Google's Native Client sandbox for Chrome, its architecture, security features, and potential vulnerabilities. Learn about PPAPI and a tool for fuzzing PPAPI interfaces.
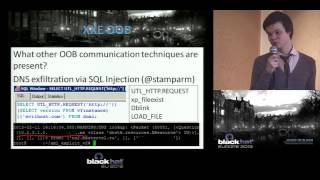
XML Out-of-Band Data Retrieval
Explore innovative XML out-of-band data retrieval techniques for accessing files and resources from victim's machines, even with normal output from vulnerable applications.
SSL Future Authenticity
Exploring SSL's history, current authenticity issues, recent infrastructure attacks, and potential solutions, with a focus on fixing trust relationships in this fundamental protocol.
Web Application Brute Forcing 101
Learn techniques for web application brute forcing, exploring vulnerabilities and security measures to protect against unauthorized access attempts.