Software Assurance Automation Throughout the Lifecycle
Explore software assurance automation strategies across the development lifecycle, enhancing security and efficiency in software production.
Why Do Developers Make Dangerous Software Errors
Explore why developers create risky software, the importance of secure coding practices, and strategies for implementing effective software assurance in modern technology development.
AppSec Inception - Exploiting Software Culture
Explore software security culture and its exploitation with insights from Aspect Security's CEO Jeff Williams in this thought-provoking talk on application security challenges.
Application Security & User Experience
Explore the intersection of application security and user experience, focusing on balancing robust protection with seamless interactions in software design.
Speeding Up Security Testing Panel
Panel discussion on accelerating security testing processes, featuring insights from industry experts on best practices, tools, and strategies for efficient vulnerability assessment.
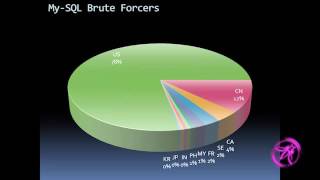
Keeping Up with the Web Application Security
Explore strategies for maintaining robust web application security in an ever-evolving digital landscape. Learn from industry experts about current threats and effective countermeasures.
Six Key Metrics - A Look at the Future of AppSec
Explore six crucial metrics shaping the future of application security. Gain insights into emerging trends and strategies for enhancing your organization's AppSec practices.
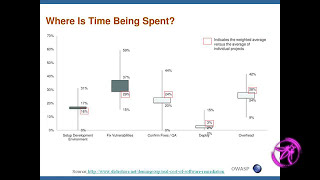
Application Security Debt and Application Interest Rates
Explore application security debt and interest rates with Chris Wysopal from Veracode. Learn strategies to manage and mitigate security risks in software development.
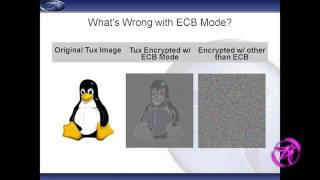
Enterprise Security API ESAPI 2.0 Crypto Changes
Explore ESAPI 2.0's cryptographic enhancements and the OWASP Project Portal, featuring insights from security experts Kevin Wall and Jason Li.
Secure Programming Support in IDE
Explore IDE-integrated tools for enhancing secure programming practices, focusing on automated vulnerability detection and developer support during coding.
Runtime Manipulation of Android and iOS Applications
Explore runtime analysis and manipulation techniques for mobile app security testing, focusing on tools for iOS and Android to enhance your mobile security toolbox.
How to Take Over a Production System in the Cloud
Explore real-world cloud security vulnerabilities, their root causes, and effective mitigation strategies through examples and demonstrations. Learn to protect your cloud systems from potential threats.
SBOM is Here - Making Progress - Not Excuses
Explore the progress and implementation of Software Bill of Materials (SBOM) in cybersecurity, discussing challenges, opportunities, and practical strategies for effective adoption and utilization.
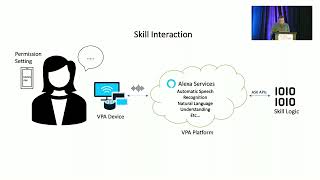
SkillDetective - Automated Policy-Violation Detection of Voice Assistant Applications in the Wild
Automated tool for detecting policy violations in voice assistant apps, analyzing 54,055 Alexa skills and 5,583 Google actions, identifying over 6,000 violations across 52 policy requirements.
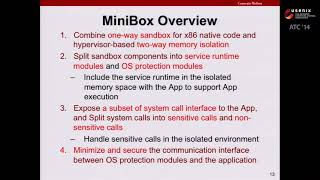
MiniBox - A Two-Way Sandbox for x86 Native Code
Explore MiniBox, a groundbreaking two-way sandbox for x86 native code, offering mutual protection between applications and operating systems in cloud computing environments.
T-Fuzz - Fuzzing by Program Transformation
Innovative fuzzing technique that removes input checks to explore deeper code paths, improving bug discovery in software. Combines program transformation with symbolic execution for effective results.
Angora - Efficient Fuzzing by Principled Search
Innovative fuzzing technique combining mutation-based speed with high-quality input generation, outperforming existing fuzzers in bug detection and branch coverage through advanced constraint-solving methods.
Hackers vs. Testers - A Comparison of Software Vulnerability Discovery Processes
Explore the processes, skills, and challenges of software testers and white-hat hackers in identifying security vulnerabilities, based on a comparative study of 25 professionals.
How the BIOS Assures Its Handling of Inputs
Explore BIOS input handling, firmware interfaces, and analysis techniques for formal validation and vulnerability detection, including static, dynamic, and symbolic execution approaches.
Eliminating Input-Based Attacks by Deriving Automated Encoders and Decoders from Context-Free Grammars
Learn to derive automated encoders and decoders from context-free grammars to eliminate input-based attacks, enhancing security in complex language communication systems.
SymCerts - Practical Symbolic Execution for Exposing Noncompliance in X.509 Certificate Validation
Explore practical symbolic execution techniques to uncover noncompliance in X.509 certificate validation implementations, enhancing security in SSL/TLS protocols and IoT systems.