Fuzzing the Stack for Fun and Profit
Explore stack fuzzing techniques for vulnerability discovery and exploitation in this hands-on talk from DefCamp 2019, covering the latest research and practices in information security.
How to Fuzz like a Hacker
Aprenda técnicas avançadas de fuzzing para identificar vulnerabilidades de segurança em sistemas e aplicações, apresentadas por especialistas no DefCamp 2018.
Securing the Openness - The Operator Challenge
Exploración de desafíos de seguridad para operadores de telecomunicaciones, abordando la apertura de redes y la protección de infraestructuras críticas en un entorno digital en evolución.
Bad Software Is Eating the World! Let's Fix It!
Explore strategies to address the prevalence of flawed software in our digital world and learn practical approaches to improve software quality and security.
Crypto as a Global Business
Exploración de la criptografía como negocio global: tendencias, oportunidades y desafíos en el mercado internacional de seguridad de la información.
OSSTMM - The "Measure, Don't Guess" Security Testing Methodology
Explore the OSSTMM security testing methodology, emphasizing precise measurement over guesswork. Learn practical approaches to enhance your organization's information security practices.
Cyber Security in Real Business World
Explore real-world cybersecurity challenges and solutions in business environments. Gain insights from industry experts on latest practices, research, and emerging threats in information security.
Fuzzing Closed Source Applications
Explore techniques for fuzzing closed source applications to uncover vulnerabilities and improve security. Learn practical approaches to test proprietary software without access to source code.
Wie Hackt Man Einen Analogrechner
Einblick in unkonventionelles Computing und Analogrechner: Zukunftstechnologie, Anwendungen in KI und Quantencomputing, Vorstellung des Open-Source-Analogrechners "The Analog Thing" und Hacking-Möglichkeiten.
Dependency-Management für faule Software-Entwickler
Automatisierung des Dependency-Managements in langlebigen Softwareprojekten: Einsatz von Tools wie Renovate zur effizienten Aktualisierung von Bibliotheken und Verbesserung der Sicherheit.
TextExerciser - Feedback-Driven Text Input Exercising for Android Applications
Iterative, feedback-driven system for generating text inputs in Android app testing. Utilizes app-provided hints to improve input generation, increasing code coverage and vulnerability detection.
ProFuzzer - On-the-fly Input Type Probing for Better Zero-day Vulnerability Discovery
Innovative fuzzing technique that automatically probes input fields, adapts mutation strategies, and enhances zero-day vulnerability discovery without prior input specifications.
Fuzzing File Systems via Two-Dimensional Input Space Exploration
Explores innovative fuzzing technique for file systems, addressing challenges in input space exploration, operation generation, and bug reproduction. Introduces JANUS, a feedback-driven fuzzer with improved efficiency and reproducibility.
Introduction to Bug Hunting
Learn essential techniques and strategies for identifying and reporting software vulnerabilities, enhancing your skills in ethical hacking and cybersecurity.
Scraping After HiQ Labs v. LinkedIn
Explore recent legal developments affecting web scraping's legality, focusing on the HiQ Labs v. LinkedIn case and its implications for data collection practices.
Building Production-Grade End to End Encrypted Applications
Insights on building end-to-end encrypted applications, addressing challenges in security, compliance, abuse prevention, availability, and observability for privacy-focused collaborative products.
HSMs in Plain Envelopes - A Code Signing Story
Explore the challenges of code signing for open source developers, addressing outdated mechanisms and high costs while examining the complexities and frustrations involved in the process.
How Do You Trust Your Open Source Software?
Explore OpenSSF Scorecard, an automated tool assessing software security heuristics. Learn how it evaluates dependencies and identifies areas for improving security posture in open source projects.
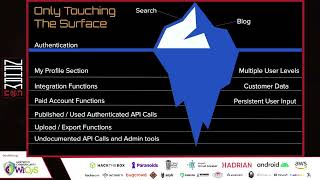
The Bug Hunter's Methodology - Application Analysis v1
Comprehensive guide to application analysis for bug hunters, covering advanced techniques, tools, and methodologies to identify vulnerabilities and maximize bounty rewards.
Using Chromedp to Hunt for Prototype Pollution
Learn to use Chromedp in Go for detecting prototype pollution at scale, enhancing your ability to identify and address this client-side security vulnerability efficiently.

Microsoft Ignite 2021 - Empowering Hybrid Work and Innovation
Explore the future of hybrid work, cloud innovation, and cybersecurity with Satya Nadella. Learn to empower teams, build next-gen apps, and protect your organization in a changing digital landscape.