When the Cops Come A-Knocking - Handling Technical Assistance Demands from Law Enforcement
Guidance on handling law enforcement demands for technical assistance, covering types of requests, legal authority, and response options for companies protecting user data and privacy.
Exploiting Linux and Pax ASLR's Weaknesses on 32-Bit and 64-Bit Systems
Uncover vulnerabilities in Linux and PaX ASLR implementations, exploring low entropy, distribution issues, and object correlations. Learn to bypass Full ASLR and discover ASLR-NG, a new design addressing current weaknesses.
Triaging Crashed with Backward Taint Analysis for ARM Architecture
Explore tools for analyzing crashes on Linux and ARM, using dynamic binary instrumentation and backward taint analysis to determine exploitability. Learn about ARM-Tracer and ARM-Analyzer for efficient crash analysis.
Fuzzing Android - A Recipe for Uncovering Vulnerabilities Inside System Components in Android
Explore a fuzzing approach to uncover vulnerabilities in Android's core system components. Learn about data generation, test execution, logging, and triage mechanisms for effective vulnerability detection.
The Tactical Application Security Program - Getting Stuff Done
Aprenda a implementar um programa de segurança tático e eficaz, focando em avaliações ágeis, resposta a incidentes e gerenciamento de bugs. Descubra por que abordagens táticas podem ser mais efetivas que estratégias de longo prazo.
Assessing and Exploiting BigNum Vulnerabilities
Explore vulnerabilities in multi-precision integer arithmetic used in cryptography implementations. Learn bug patterns, exploitation techniques, and strategies for automated vulnerability detection.
Return to Where? You Can't Exploit What You Can't Find
Explore advanced techniques for detecting and preventing memory corruption vulnerabilities, including execute-only memory and code pointer hiding, to enhance software security against sophisticated exploitation methods.
Broadcasting Your Attack - Security Testing DAB Radio in Cars
Explore vulnerabilities in DAB radio systems in cars, potential security risks, and implications for automotive cybersecurity using Software Defined Radio and custom testing tools.
ROPInjector - Using Return Oriented Programming for Polymorphism and Antivirus Evasion
Explore advanced polymorphism techniques using Return Oriented Programming for antivirus evasion, with practical demonstrations of the ROPInjector tool and its effectiveness against detection methods.
Universal Android Rooting Is Back
Explore universal Android rooting through kernel exploitation, focusing on a Use-After-Free bug affecting all Linux versions. Learn about innovative techniques for 64-bit devices and bypassing modern kernel mitigations.
Hey, Your Parcel Looks Bad - Fuzzing and Exploiting Parcelization Vulnerabilities in Android
Explore Android's Binder IPC vulnerabilities through fuzzing and exploitation techniques. Learn to identify, analyze, and exploit "BadParcel" issues for privilege escalation in high-privilege processes.
Break Out of The Truman Show - Active Detection and Escape of Dynamic Binary Instrumentation
Explore active detection techniques for Dynamic Binary Instrumentation, focusing on exploiting weaknesses and escaping control. Learn to identify and overcome DBI environments in cybersecurity.
Android Commercial Spyware Disease and Medication
Explores Android vulnerabilities exploited by spyware and proposes a detection method using fuzz testing to mitigate risks and protect user privacy on smartphones.
The Tactical Application Security Program - Getting Stuff Done
Practical approach to application security: lightweight team, agile methods, and operational excellence. Covers assessments, bug handling, and private bug bounty programs, with actionable advice for managers and practitioners.
Attacking SDN Infrastructure - Are We Ready for the Next-Gen Networking?
Exploring SDN vulnerabilities through attacks on control plane, channel, and data plane. Demonstrates critical exploits affecting network availability and confidentiality, and introduces SDN security projects.
AndroBugs Framework - An Android Application Security Vulnerability Scanner
Explore AndroBugs Framework, a free Android vulnerability analysis system. Learn to identify and mitigate security risks in Android apps before release, enhancing app safety and user protection.
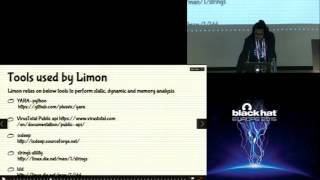
Automating Linux Malware Analysis Using Limon Sandbox
Explore automated Linux malware analysis with Limon sandbox. Learn to collect, analyze, and report runtime indicators using static, dynamic, and memory analysis techniques for comprehensive threat assessment.
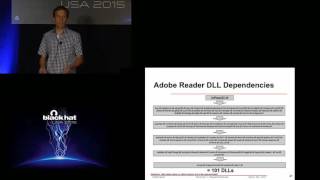
Breaking Payloads With Runtime Code Stripping and Image Freezing
Innovative defensive strategy to break attack payloads by removing unused code and APIs from application processes, enhancing security without runtime overhead or file modifications.
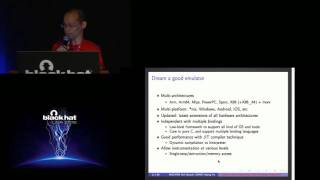
Unicorn - Next Generation CPU Emulator Framework
Versatile CPU emulator framework supporting multiple architectures and platforms. Offers clean API, thread-safety, and language bindings for building advanced security tools and research.
Web Application Security Crossfire
Explore web application security challenges and solutions through expert insights in this panel discussion from Black Hat USA 2004.
Trust No-One, Not Even Yourself - The Weak Link Might Be Your Build Tools
Explore security vulnerabilities in build tools and development environments, emphasizing the importance of vigilance in software creation processes.