Data & Software Sharing Guidance for Early Career Researchers - AGU Journal Requirements
Learn best practices for citing and sharing research data and software, focusing on AGU journal requirements and tools that simplify the process for early career researchers.
Managing the Reactive World with RxJava - Jake Wharton
Explore asynchronous programming with RxJava: model reactive sources, handle data streams, and learn about Java 9's Flow API for building robust, responsive applications.
Why Bother Assessing Popular Software
Explore assessing popular software like Adobe Reader, discussing fuzzing, sandboxes, and JavaScript APIs. Learn approaches for complex targets and making a security impact.
Penetration Testing Must Die
Explore the limitations and challenges of penetration testing in cybersecurity, discussing its effectiveness, terminology issues, and potential alternatives for improving security assessments.
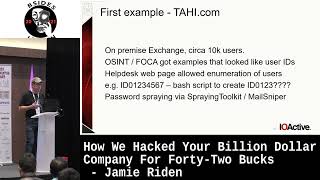
How We Hacked Your Billion Dollar Company For Forty-Two Bucks
Discover how a small investment can expose major vulnerabilities in billion-dollar companies. Learn about red teaming, user enumeration, and password spraying techniques used by ethical hackers.
Securing Cloud Delivery Pipelines - Findings From A Blue-Red Team Security Simulation
Explore findings from a blue/red team security simulation focused on securing cloud delivery pipelines, with insights on tooling, advanced attackers, and best practices.
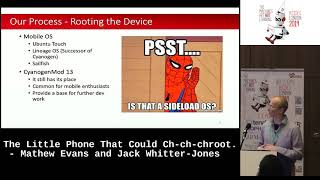
The Little Phone That Could Ch-ch-chroot
Explore cost-effective Red Team tactics using a covert disposable phone for reconnaissance, including device rooting, functionality, and anti-forensics techniques.
Assessing the Embedded Devices On Your Network
Explore embedded device security challenges, threat modeling, and assessment techniques through a VoIP phone case study. Learn hardware tricks, debugging methods, and potential mitigations for vulnerabilities.
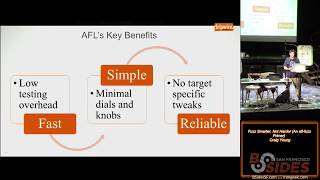
Fuzz Smarter, Not Harder - An AFL-Fuzz Primer
Comprehensive guide to efficient fuzzing using afl-fuzz, covering instrumentation techniques, optimization strategies, and crash analysis for effective bug hunting and software security testing.
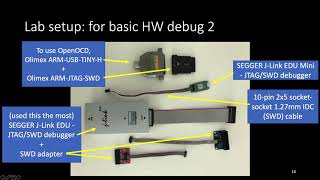
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
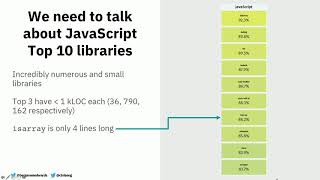
The Devils in the Dependency - Data Driven Software Composition Analysis
Análisis de datos sobre el uso de bibliotecas de código abierto en aplicaciones, examinando vulnerabilidades, dependencias y patrones de actualización para mejorar la seguridad del software.
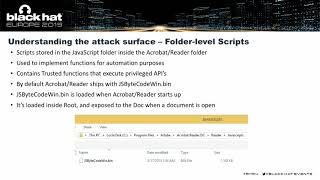
Tackling Privilege Escalation with Offense and Defense
Explore privilege escalation in JavaScript engines, focusing on offensive techniques and defensive strategies. Learn about vulnerabilities, attack surfaces, and security model improvements.
What the Fuzz
Explore cutting-edge fuzzing technologies, their potential, and future developments through demos, CVEs, and research insights from experts in the field.
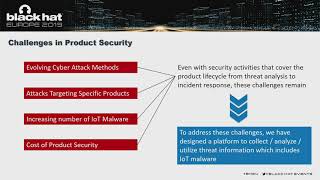
Understanding the IoT Threat Landscape
Explore IoT threat landscape, malware analysis, and Panasonic's approach to developing resilient products and an IoT SOC. Learn about security testing and the IoT Intelligence Platform.
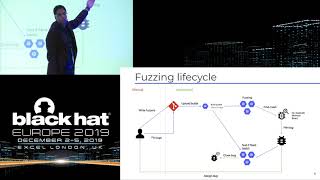
ClusterFuzz - Fuzzing at Google Scale
Explore Google's massive fuzzing infrastructure, ClusterFuzz, and learn how it finds thousands of security vulnerabilities across Google products and open-source projects.
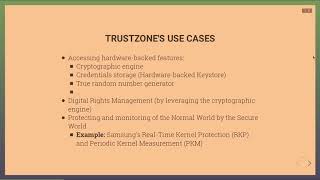
Breaking Samsung's ARM TrustZone
Explore Samsung's TrustZone vulnerabilities and learn techniques to exploit trusted components, execute high-privilege code, and bypass security measures in ARM-based systems.
BluePill - Neutralizing Anti-Analysis Behavior in Malware Dissection
Explore BluePill, a customizable tool for neutralizing anti-analysis techniques in malware. Learn how it defeats evasive samples and executable protectors, enhancing malware dissection capabilities.
Mac-A-Mal - An Automated Platform for Mac Malware Hunting
Automated platform for macOS malware analysis, featuring kernel-level behavioral monitoring and extending Cuckoo sandbox capabilities. Supports various sample types and detects evasion techniques.
Static Detection and Automatic Exploitation of Intent Message Vulnerabilities in Android
Explore Android app vulnerabilities, static analysis techniques, and automated exploitation methods for intent message flaws. Learn to identify and mitigate security risks in mobile app development.

IoT Malware - Comprehensive Survey, Analysis Framework and Case Studies
Comprehensive exploration of IoT malware, covering its evolution, analysis frameworks, and real-world case studies. Insights into vulnerabilities, detection methods, and future challenges in securing connected devices.
A New Era of SSRF - Exploiting URL Parser in Trending Programming Languages
Explore a new SSRF exploit technique targeting URL parsers in popular programming languages. Learn about protocol smuggling, fuzzing tools, and discover vulnerabilities in widely-used libraries.