X11 and Wayland - A Tale of Two Implementations
Explore the journey of implementing X11 window manager and Wayland compositor 'hikari', covering design goals, programming choices, libraries, and challenges faced in development.
Verwaltung von Projekten mit Gitea
Einführung in Gitea als selbstkontrollierte Alternative zu GitHub. Vorstellung der Vorteile, Installation und Best Practices für Projektverwaltung mit Git, geeignet für Anfänger und Fortgeschrittene.
Verwaltung von Projekten mit Gitea
Einführung in Gitea als selbstkontrollierte Alternative zu GitHub. Vorstellung der Vorteile, Installation und Best Practices für Projektverwaltung mit Git, geeignet für Anfänger und Fortgeschrittene.
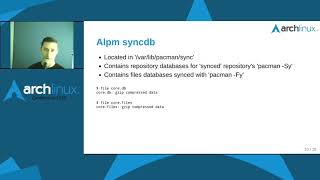
Pytest-Pacman - Generating Test Data for Libalpm with Python
Explore generating test data for libalpm using Python, focusing on creating local and sync databases for pyalpm testing without relying on pacman or internet fetching.
Wie klimafreundlich ist Software?
Einblicke in die Forschung zur Umweltrelevanz von Software und Ausblick auf Umweltzertifizierung. Präsentation von Messergebnissen, Erläuterung der Forschungsmethodik und Vorstellung geplanter Umweltzeichen-Kriterien für ressourceneffiziente Software.

Emulate - Fuzz - Break Kernels
Introducción a la fuzzing de kernels usando unicorefuzz: emulación de CPU para encontrar bugs en parsers del kernel de forma simple y efectiva.

Dämliche Dinge mit Git Repositorys anstellen
Entdecken Sie unkonventionelle Git-Anwendungen und lernen Sie, warum diese problematisch sind. Erfahren Sie bessere Alternativen für effektives Versionskontrollmanagement.
Swiss Cybervoting Pitfalls
Análisis crítico del sistema de voto electrónico suizo, sus desafíos técnicos y no técnicos, y las controversias surgidas durante las pruebas de intrusión pública desde la perspectiva de un investigador de seguridad.
Implementing a Harmonized Shipping Label Generator
Explore the implementation of harmonized shipping labels in the EU, addressing challenges and proposing solutions for this new regulatory requirement.
Android Rootkits - Analysis from Userland and Kernelland
Explore Android rootkit analysis using memory forensics, dynamic binary instrumentation, and machine learning for actionable threat intelligence in userland and kernelland.
Using Ancient Math to Speed Up Security Assessments of Windows Executables
Discover how to accelerate Windows executable security assessments using Euclidean Distance and Bayes Theorem, enabling rapid triage and efficient risk reduction in regulated environments.
Fuzzing Ruby and C Extensions
Explore fuzzing techniques for Ruby and C extensions, focusing on security implications and using AFL fuzzer to identify vulnerabilities in Ruby language and gems.
The SecDevOpronomicon - Arcane Secrets for Scaling Your Company’s Security
Uncover arcane secrets for scaling security efforts in fast-paced development environments. Learn high-value engineering techniques, custom analyses, and CI/CD pipeline integration to enhance SecDevOps practices.
Your Secrets are Showing - How to Find if Your Developers are Leaking Secrets
Discover tools and techniques to identify and prevent sensitive information leaks in source code repositories, both within corporate networks and on public platforms.
Sharks in the Water - Open Source Component Risk and Mitigation
Explore open source component risks and mitigation strategies, focusing on supply chain vulnerabilities, recent hacks, and preventive measures through education and automated tooling.
Privacy Nightmares while Using ML - AI in Your Applications
Explore privacy challenges in ML/AI applications and learn about a framework that integrates data security with machine learning technologies to address potential nightmares.
Automating Web Application Bug Hunting
Discover techniques for automating web application vulnerability scanning to enhance bug bounty hunting and application security analysis efficiency.
Deploying Two-Factor Authentication to Millions of Users
Comprehensive guide on implementing two-factor authentication for large-scale websites, covering design, architecture, and various methods like TOTP, push notifications, and FIDO security keys.
How to Build an Application Security Program
Practical insights on creating and improving application security programs, drawing from 20 years of experience across various sectors. Covers successful strategies and pitfalls to avoid.
Lyft Cartography - Automating Security Visibility and Democratization
Explore Lyft's open-source security intelligence platform for asset tracking, relationship mapping, and automated decision-making. Learn how it improves visibility and empowers teams to enhance security posture.
Fuzzing Malware for Fun & Profit
Explore coverage-guided fuzzing to find vulnerabilities in malware, potentially stopping DDoS attacks and controlling botnets. Learn about netAFL tool and see real-world exploitation demos.