Navigating the Software Supply Chain Defense Landscape
Explore software supply chain security tools and frameworks, their integration, and how to select the right combination for comprehensive protection against rising cyber threats.
Fresh SLSA and GUAC - Understanding Open Source Package Risks and Transparency
Explore open source package risks, transparency, and tools like GUAC, SLSA, and SBOMs to enhance software supply chain security and make informed decisions on dependencies.
Eating the Open Source Security Sandwich with Skootrs
Explore Skootrs, an open-source tool simplifying adoption of security practices for software developers through automation and guardrails.
SLSA: A Security Paradigm for Software Supply Chain Integrity
Explore SLSA levels, software supply chain security basics, and tools like Cosign to enhance artifact integrity and benefit your organization.
Securing the Software Supply Chain: An In-Depth Exploration of SLSA
Explore SLSA's impact on software supply chain security, covering fundamentals, trust, transparency, security levels, industry effects, and future trends.
Securing Python Projects Supply Chain
Explore best practices and tools for securing Python projects' supply chain, from development to distribution. Learn about cryptographic signatures, SBOMs, and SLSA attestations.
SLSA: Enhancing Software Supply Chain Security - More Than Just a Garnish for Your Pipelines
Explore SLSA principles for securing software supply chains. Learn threat models, security levels, and how to contribute to this OpenSSF project for enhanced DevSecOps processes.
Let Devs Be Devs Without Sacrificing Security
Explore flexible, secure CI pipelines using Tekton, Chains, and Enterprise Contract to balance developer innovation with robust security measures for various software targets.
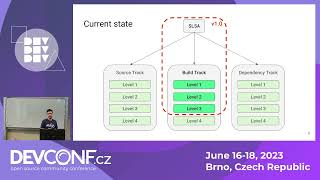
SLSA - A Supply Chain Security Framework
Explore SLSA framework for securing software supply chains, mitigating vulnerabilities, and ensuring code integrity from development to deployment.
Cloud Native Security Landscape - Myths, Dragons, and Real Talk
Explore cloud-native security across the software lifecycle, from open-source creation to runtime threat detection. Learn about key projects, developer-security team collaboration, and separating real risks from myths.
Cloud Native Supply Chain Security: Beyond SBOMs - Perspectives and Practices
Insights on cloud native supply chain security beyond SBOMs. Experts discuss straightforward approaches, simple security practices, and future perspectives using open-source tools and frameworks.
Open Source Security and Supply Chain Innovations - Keynote Sessions
Explore cutting-edge topics in open source security, including supply chain protection, Sigstore, SPDX, eBPF, SLSA, and memory safety, presented by industry leaders and experts.
Releasing Kubernetes Less Often and More Securely - SIG Release Update
Discover the latest updates from Kubernetes SIG Release, including efforts to enhance security, streamline release processes, and achieve SLSA compliance. Learn about roadmap, vision, and opportunities to contribute.
Trust in Honk, Tie Up Your YAML - A Kpack Experience for Container Image Building
Explore kpack for building container images on Kubernetes, leveraging Cloud Native Buildpacks and enhancing supply chain security through declarative resources and automated processes.
Building Images for the Secure Supply Chain
Techniques and tools for building secure container images, including distroless philosophy, updating dependencies, using apko for reproducibility, and signing with Sigstore.
Securing the IaC Supply Chain
Explore securing Infrastructure as Code supply chains, applying software security principles to IaC pipelines. Learn about Crossplane's integration with Sigstore for enhanced provenance and attestations.
How SIG Release Cooks Trustworthy Artifacts From Raw Source Code - Kubernetes Build Process
Explore how Kubernetes SIG Release transforms source code into trusted artifacts, focusing on SLSA compliance, community-controlled infrastructure, and expanded artifact signing.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
Open Tools for Secure Supply Chains in Kubernetes - From Release Engineering
Explore open-source tools for secure software supply chains, focusing on Kubernetes' journey to SLSA Level 3 compliance and how other projects can leverage these tools for enhanced security.
Software Supply Chain Security for Those in a Rush
Concise overview of software supply chain security concepts like SBOM, SLSA, and GUAC. Gain insights into emerging cybersecurity threats and their importance in the industry.

SLSA, SigStore, SBOM & Software Supply Chain Security - What Does It All Mean?
Demystifying software supply chain security: SLSA, SigStore, and SBOM explained. Learn about tools and methodologies to secure software from development to production in this comprehensive overview.