Hardware Security
Explore cutting-edge hardware security research and innovations presented at CHES 2023, covering topics like side-channel attacks, countermeasures, and secure hardware design.
Side-Channel Evaluation and Distinguishers
Explore cutting-edge research on side-channel attacks and defenses in cryptography, featuring expert presentations on evaluation techniques and distinguishers at CHES 2023.
Fifty Years of Academic Research in Cryptography and Twenty-Five Years of CHES
Explore 50 years of academic cryptography research and 25 years of CHES in this insightful talk by renowned expert Bart Preneel, covering key developments and milestones in the field.
Fault Resistance II
Explore advanced fault resistance techniques in cryptographic hardware at this CHES 2024 session, chaired by Naofumi Homma.
Masking Faults in Cryptographic Hardware - CHES 2024 Session
Explore fault-resistant masking techniques in cryptographic hardware, examining cutting-edge research and implementations presented at CHES 2024.
Post-Quantum Cryptography for Embedded Systems - Welcome and Session I
Explore post-quantum cryptography for embedded systems in this CHES 2024 session, featuring welcome remarks and cutting-edge research presentations on securing future technologies.
Leakage in Cryptographic Hardware and Embedded Systems
Explore cutting-edge research on leakage in cryptographic hardware and embedded systems at this CHES 2024 session, chaired by Thorben Moos.
Machine Learning - CHES 2024
Explore cutting-edge applications of machine learning in cryptography and hardware security at this CHES 2024 session, chaired by Fatemeh Ganji.
Glitches in Cryptographic Hardware - CHES 2024 Session
Explore cutting-edge research on glitches in cryptographic hardware at CHES 2024, chaired by Shahin Tajik. Gain insights into the latest developments and potential vulnerabilities in secure systems.
PQC IV High-End - Post-Quantum Cryptography Implementation
Explore cutting-edge post-quantum cryptography developments in this CHES 2024 session, focusing on high-end implementations and advancements in the field.
Masking in Post-Quantum Cryptography
Explore post-quantum cryptography masking techniques and their applications in secure hardware implementations at this CHES 2024 session chaired by Svetla Nikova.
Exposing and Exploiting AACSv2 UHD DRM - Full AACSess
Exposing vulnerabilities in AACSv2 DRM for UHD Blu-ray, including side-channel attacks on Intel SGX, leading to the first full compromise and unofficial playback of UHD-BD discs.
Jailbreaking TETRA Digital Radios and Base Stations - Security Analysis and Vulnerabilities
Dive into reverse engineering TETRA radio systems, uncovering cryptographic vulnerabilities, exploiting security flaws, and gaining control of Motorola MTM5x00 radios and base stations through practical demonstrations.
Web Timing Attacks That Actually Work - Practical Techniques and Tools
Discover practical web timing attack techniques to uncover server secrets, masked vulnerabilities, and hidden attack surfaces using efficient, real-world methods and open-source tools.
Shesha: Multi-head Microarchitectural Leakage Discovery in New-generation Intel Processors
Discover how Shesha framework automates detection of transient execution attacks in Intel processors, exploring new vulnerabilities in instruction set extensions and cryptographic implementations.
GoFetch: Breaking Constant-Time Cryptographic Implementations Using Data Memory-Dependent Prefetchers
Explore groundbreaking research on data memory-dependent prefetchers and their impact on cryptographic security, focusing on vulnerabilities in Apple M-series processors and constant-time implementations.
Go Go Gadget Hammer: Flipping Nested Pointers for Arbitrary Data Leakage
Explore a novel Rowhammer exploit technique targeting nested pointer dereferences in code patterns, demonstrating enhanced data leakage capabilities and improved attack primitives in Linux kernel security.
SpecLFB: Eliminating Cache Side Channels in Speculative Executions
Discover how SpecLFB leverages Line-Fill-Buffer to eliminate cache side-channel vulnerabilities in speculative executions, offering an efficient defense mechanism with minimal performance impact.
Neural Network Extraction Through Physical Side Channels - A Systematic Review
Explore physical side-channel analysis attacks on deep neural networks, examining threat models, attack methodologies, and practical limitations for model extraction and input recovery on hardware accelerators.
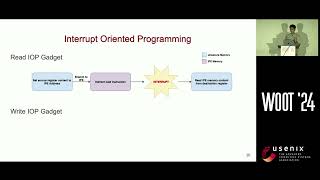
RIPencapsulation: Defeating IP Encapsulation on TI MSP Devices
Uncover critical security vulnerabilities in TI MSP devices' IP Encapsulation, exploring attack methods that compromise proprietary code and confidential data in IoT Trusted Execution Environments.
Amplifying Threats: The Role of Multi-Sender Coordination in SMS-Timing-Based Location Inference Attacks
Explore how multiple SMS senders can enhance location inference attacks through timing side channels, revealing improved accuracy and potential security vulnerabilities in mobile networks.