Intermediate ASP.NET Core - Service Registration and User Management - Episode 40
Learn to optimize service registration, handle user creation, and implement cart clearing in ASP.NET Core for an online shop application.
Transactional Microservices with Vitess - Coordination Without State
Learn to implement distributed ACID transactions in microservices using Vitess, enabling seamless migration from monolithic architectures while maintaining data consistency and reliability.
PHP Security Redefined - AppSecUSA 2015
Explore PHP's security evolution, best practices, and tools for safer application development, with insights on PHP 7's improvements and community-driven security initiatives.
Top 10 Security Best Practices for Securing Microservices
Comprehensive guide to securing microservices, covering TLS, authentication, authorization, DDoS protection, monitoring, encryption, and more. Essential for developers and architects building scalable, secure APIs.
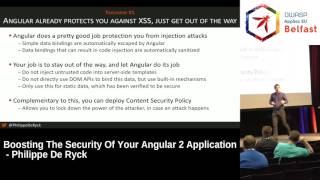
Boosting the Security of Angular Applications
Boost Angular 2 app security: Learn about script-based threats, defenses, session management, CSRF, cookie flags, Authorization headers, and JWT tokens. Gain practical knowledge to effectively secure your applications.
OWASP Application Gateway: Introduction and Usage for Secure Web Applications
Explore OWASP Application Gateway: a modern HTTP reverse proxy for secure web apps. Learn its benefits, implementation, and customization for enhanced application security.
How the Latest MASVS and MSTG Specs Enhance Mobile Penetration Testing
Explore mobile security challenges, attack surfaces, and best practices using OWASP guidelines. Learn to leverage tools and frameworks for effective mobile app security testing and policy development.

Build a Complete Login System With PHP and XML
Learn to create a fully functional membership site using PHP and XML, covering user authentication, registration, and data management.
CodeIgniter from Scratch - Day 5
Learn to build dynamic web applications using CodeIgniter framework. Master essential concepts, best practices, and advanced techniques for efficient PHP development.
Ruby on Rack: The Magic Between Request and Response
Explore Rack's inner workings, versatility, and middleware magic in Ruby web development. Gain insights on session management, authentication, and caching for more efficient and enjoyable coding.
Refactoring Sessions with Dependency Inversion in ASP.NET Core - Online Shop Tutorial Episode 37
Learn to refactor ASP.NET Core applications by applying dependency inversion principles and extracting session logic, improving code organization and maintainability.

Creating a Signup System in PHP - Learn PHP Full Course for Beginners 2023
Learn to build a PHP signup system with error handling, MySQL integration, and MVC pattern. Covers database connection, session management, and user-friendly error messaging.
Connecting Multiple ChatGPT Sessions with Dynamic Instruction Prompt Templates
Master advanced prompt design techniques to connect and optimize multiple ChatGPT sessions using Dynamic Instruction Prompt Templates (DIPT), enabling continuous learning and improved effectiveness across conversations.
OpenShift WebConsole - Bring Your Own OIDC Provider
Explore OpenShift WebConsole's adaptation for direct OIDC provider integration, addressing multi-server session challenges and authentication implementation in cluster environments.
Introducing the ASVS 4.0
Explore OWASP ASVS 4.0 updates, new controls, and industry applications. Learn about modern web app security, architecture changes, and a novel attack technique.
Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and best practices to protect your APIs. Learn to assess and improve API security for better data protection and user account safety.
Web Application Session Strength
Explore web application security, focusing on session management, token creation, and potential vulnerabilities. Learn strategies to protect against common threats and enhance overall application security.
Getting Single Page Application Security Right
Explore SPA security challenges and solutions, covering XSS, CSP, session management, and CSRF in RESTful APIs. Learn practical strategies for building secure web applications using modern frameworks.
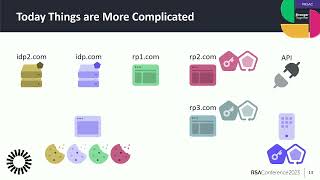
Signing Out and Session Management in 2023
Explore modern sign-out challenges and solutions in identity management, including backchannel logout, session-bound tokens, and strategies to address third-party cookie deprecation.
The Dirty Little Secrets They Didn't Teach You In Pentesting Class
Uncover advanced penetration testing techniques, from domain admin strategies to post-exploitation tactics. Learn covert persistence methods and efficient data discovery for enhanced cybersecurity assessments.
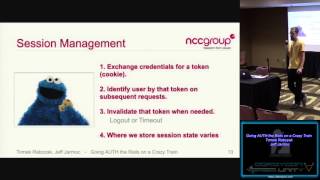
The 3 Way09 Going AUTH the Rails on a Crazy Train
Explore authentication vulnerabilities in Ruby on Rails applications, focusing on common pitfalls and effective security measures for web developers.