Running an API Gateway on Istio - Pitfalls and Learnings
Explore challenges and solutions for running large-scale API Gateway on Istio, including performance optimization, cost management, and implementing region failovers using Argo workflows.
Ambient Operations: Automating Istio Orchestration with Argo
Explore automating Istio upgrades using Argo, leveraging Ambient Mode for declarative management. Learn to build an operations platform for seamless testing and rollout across environments.
Unraveling Istio - A Tale of Scale, Challenges and Triumphs at DevRev
Explore DevRev's journey with Istio service mesh, from implementation challenges to scaling solutions. Learn best practices for maximizing Istio's potential in globally-distributed SaaS products.
Kiali Beyond the Graph - Troubleshooting Istio
Explore Kiali's advanced features for troubleshooting Istio, including Wizards and Envoy inspection. Learn tips to quickly onboard and resolve issues in your service mesh.
Bridging Trust Between Multi-Cluster Meshes
Explore secure communication between Kubernetes clusters using SPIFFE, SPIRE, and Istio. Learn to establish trust, manage identities, and configure seamless inter-cluster interactions in multi-cluster mesh architectures.
Challenges and Best Practices for Upgrading Istio in Production Environments
Explore challenges and best practices for upgrading Istio in production environments. Learn strategies for compatibility assessment, phased upgrades, and thorough testing to minimize risks and ensure service continuity.
Architecting Ambient Mesh for Scale
Explore Ambient mesh's architecture for improved Istio scalability, covering sidecar removal, Kubernetes controller redesign, and new configuration protocols for enhanced service mesh performance.
Identity, Istio, and Zero-Trust Environments - Choosing the Right Solution
Explore Istio's identity solutions for zero-trust environments, comparing certificate authority configurations and integrations to help you choose the best option for your specific business needs.
Lessons from Scaling AI-Powered Translation Services Using Istio
Explore how Lilt leveraged Istio to scale AI-powered translation services, improving system stability and product velocity through microservices architecture and Kubernetes integration.

Painless Multi-Tenant Kafka on Kubernetes with Istio - ASML Case Study
Explore multi-tenant Kafka on Kubernetes using Istio for seamless authentication and access control. Learn to implement secure data sharing and resource management in a self-service platform.
Practical Security in the Brave New Kubernetes World
Explore Kubernetes security vulnerabilities through hands-on recon and exploitation of clusters, sidecars, and supporting infrastructure. Learn practical techniques for compromising and persisting in real-world K8s environments.
Containers, Microservices, Serverless - On Being Serverless or Serverful
Explore the evolution of microservices, from Netflix OSS to service mesh with Envoy and Istio. Learn about serverless architecture and building a FaaS platform using Apache OpenWhisk on OpenShift.
What's a Service Mesh?
Explore service meshes: their definition, benefits, and future in distributed systems. Learn how they enhance visibility, reliability, and security in cloud environments.
Network Security for Apps on OpenShift
Explore network security strategies for OpenShift apps, covering secure tiers, external connections, and ingress protection. Learn practical solutions for enterprise-level container platform security.
Running at Light Speed - Cloud Native Security Patterns
Explore cloud native security patterns for containerized microservices, covering multi-tenancy, authentication, authorization, and encryption. Learn architectural guidance for secure software design in cloud environments.
Kubernetes for the Hybrid Enterprise
Explore Azure's Kubernetes solutions for hybrid enterprises, covering architecture, modernization, management, deployment, governance, and monitoring in distributed environments.
Service Meshing with Docker Desktop and WebAssembly
Service meshing with Docker Desktop and WebAssembly: Implement multi-tenancy and rate limiting using infrastructure. Learn to deploy service meshes, leverage Consul and Envoy's capabilities, and utilize WASM for user authentication and authorization.
Command and KubeCTL - Real-World Kubernetes Security for Pentesters
Explore Kubernetes security challenges, attack techniques, and practical advice for pentesters and security practitioners in containerized environments.
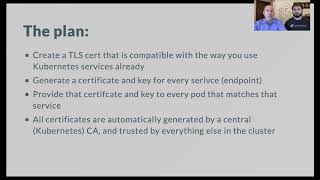
Achieving Mutual TLS - Secure Pod-to-Pod Communication Without the Hassle
Explore secure pod-to-pod communication using Mutual TLS, focusing on certificate management, implementation in Golang and Java applications, and integration with Kubernetes for streamlined security.
Container Networking Untangling Services Meshes and SDNs
Explore service meshes and SDNs in container networking, comparing Istio, Linkerd, Conduit, and OpenContrail for Kubernetes integration, scalability, routing, and security policy enforcement.
Developing & Debugging WebAssembly Filters for Envoy
Explore WebAssembly filter development for Envoy: writing, testing, debugging, and shipping. Gain insights into tooling and processes used by early adopters in service mesh environments.