Driving Your Own Vulnerability: How to Navigate the Road of BYOD Attacks
Explore Windows driver vulnerabilities and BYOD attack prevention through real-world case studies, understanding threat categories and security implications for effective system protection.
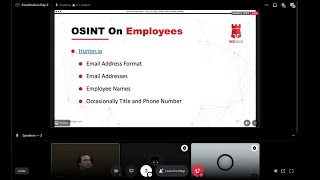
Open Source Intelligence Gathering for Security Testing - Recon 101
Master essential OSINT techniques and reconnaissance tools to efficiently gather critical intelligence about organizational infrastructure and potential security vulnerabilities without active network engagement.
The Perils of Generative AI: Implications for Open Source Intelligence
Explore how Generative AI and Large Language Models impact Open Source Intelligence (OSINT), examining challenges, risks, and strategies for maintaining data integrity in intelligence gathering.
Cracking Cicada 3301: A Journey Through the Liber Primus Cryptographic Challenge
Delve into the fascinating journey of cryptographers attempting to solve Cicada3301's Liber Primus, exploring collaborative puzzle-solving techniques, community persistence, and cryptographic challenges since 2014.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.
WINE Pairing with Malware - Using Linux Tools for Malware Analysis
Discover how to leverage WINE and Linux tools for malware analysis, extracting forensic evidence, and testing offensive security techniques without expensive sandboxes.
Leveraging macOS Networking Frameworks to Heuristically Detect Malware
Discover advanced techniques for detecting macOS malware through network monitoring, exploring low-level APIs, private frameworks, and user-mode extensions for comprehensive threat detection.
Getting a Migraine - Unique System Integrity Protection Bypass on macOS
Delve into advanced MacOS security exploitation, exploring System Integrity Protection bypass techniques, undeletable malware creation, and essential detection strategies for security teams.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.
OSINT for Physical Security Intelligence - Rapid Data Collection and Analysis
Master efficient OSINT techniques for physical security, focusing on rapid intelligence gathering, predictive analysis, and actionable insights for critical situation assessment and risk management.
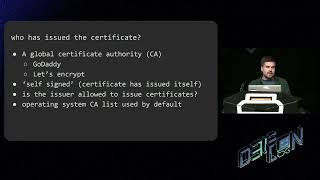
Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.
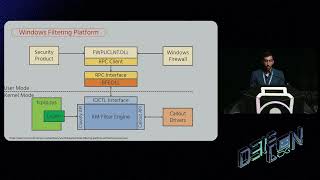
Abusing Windows Filtering Platform for Privilege Escalation - Undetected Attack Techniques
Discover an innovative Windows privilege escalation technique that exploits the Windows Filtering Platform, enabling stealthy system-level access through network traffic manipulation and kernel component abuse.
NTLM Authentication Vulnerabilities and Exploits - A Final Analysis
Dive into critical NTLM authentication vulnerabilities, exploring new bugs, bypass techniques, and security control gaps in Windows systems before Microsoft phases out this protocol.
Finding and Exploiting Local Security Vulnerabilities in 1Password for MacOS
Explore critical security vulnerabilities in 1Password's MacOS app, including local vault exploitation, IPC weaknesses, and Chrome extension flaws that could compromise password security.
HookChain: A New Perspective for Bypassing EDR Solutions
Discover a sophisticated EDR bypass technique combining IAT Hooking, dynamic SSN resolution, and indirect system calls to redirect Windows subsystem execution flow while remaining undetected by traditional security measures.
DriverJack: Turning NTFS and Emulated ROFs into an Infection
Discover advanced exploitation techniques targeting NTFS and emulated filesystem vulnerabilities, exploring novel attack vectors that bypass Windows security measures and maintain system persistence.
QuickShell: Remote Code Execution Attack Chain Analysis in Quick Share
Uncover critical security vulnerabilities in Google's Quick Share protocol, including an RCE attack chain, HTTPS MITM techniques, and protocol analysis for both Windows and Android platforms.
Defeating ATM Disk Encryption - Security Vulnerabilities in Vynamic Security Suite
Delve into critical ATM security vulnerabilities, focusing on Diebold Nixdorf's VSS encryption weaknesses, exploitation methods, and essential defense strategies for financial systems protection.
Windows Downdate: Downgrade Attacks Using Windows Updates
Discover how to exploit Windows Update vulnerabilities to craft downgrade attacks, bypass security features, and compromise system integrity - from kernel to virtualization stack.

Counter Deception: Defending Yourself in a World Full of Lies
Discover practical strategies to detect and defend against digital deception across network layers, from electromagnetic spoofing to false narratives, while developing critical skills to discern truth in our interconnected world.
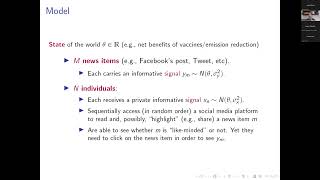
Crowding Out the Truth: A Simple Model of Misinformation
Explore a theoretical framework examining how misinformation spreads and impacts truth in digital spaces through computational modeling and political analysis.