Scare - Static Code Analysis Recognition Evasion
Explore techniques to evade static code analysis tools, including covert data flow, deep call stacks, and taint laundering. Learn how malicious code can be camouflaged to avoid detection.
LangSec for Penetration Testing - How and Why
Explore LangSec principles for enhancing penetration testing effectiveness, focusing on input handling vulnerabilities and improving security assessments through language-theoretic approaches.
Privacy in Healthcare - The Good, the Bad, and the Ugly
Explore the complexities of privacy in healthcare, examining positive aspects, challenges, and concerning issues in this informative DefCamp 2019 presentation on information security.
Logrotten - It's Not a Bug
Sicherheitslücke in Logrotate: Ausnutzung, Auswirkungen und Reichweite. Demonstration der Schwachstelle, Einfluss auf andere Softwarepakete und aktueller Stand von Logrotate werden diskutiert.
SoK - Sanitizing for Security
Overview of dynamic bug-finding tools (sanitizers) for C/C++, their security vulnerability coverage, performance, and trade-offs.
Introduction to Bug Hunting
Learn essential techniques and strategies for identifying and reporting software vulnerabilities, enhancing your skills in ethical hacking and cybersecurity.
What I Learned About Security Working Minimum Wage at Hollywood Video
Insights on security management drawn from teenage work experience at Hollywood Video, relating retail theft prevention to modern cybersecurity practices and principles.
Cameras, CACs & Clocks - A Story of Millions of Interrogated and Hacked xIoT Devices
Demonstración en vivo de ciberataques a dispositivos IoT, con hallazgos de investigación de seguridad y técnicas de mitigación de amenazas para proteger contra actores maliciosos.
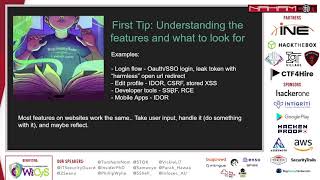
Putting Your Mind to It - Bug Bounties for 12 Months
Insights into successful bug bounty hunting strategies and experiences over a 12-month period, focusing on mindset, persistence, and effective techniques for finding vulnerabilities.
Automated Analysis and Verification of TLS 1.3 - 0-RTT, Resumption and Delayed Authentication
Explore automated analysis of TLS 1.3, focusing on 0-RTT, resumption, and delayed authentication. Learn about security verification using the Tamarin prover for this crucial protocol.
H@cktivityCon 2020 - From an 'IVI in a Box' to a 'Car in a Box'
Explore car hacking techniques, from 'IVI in a box' to 'CAR in a box', with insights on safely experimenting without damaging your own vehicle. Learn from real-world experiences and practical tips.
Crash & Pay - How to Own and Clone Contactless Payment Devices
Explore NFC payment vulnerabilities, cloning techniques, and security mechanisms. Learn to set up a testing lab and conduct fraudulent transactions using off-the-shelf devices.
Discovering and Exploiting Novel Security Vulnerabilities in Apple ZeroConf
Uncovers critical security flaws in Apple's ZeroConf frameworks, demonstrating vulnerabilities in Multipeer Connectivity, Bonjour, and services like AirDrop, allowing impersonation and man-in-the-middle attacks.
VoIP Wars - The Phreakers Awaken
Explore cutting-edge VoIP attacks, vulnerabilities, and security testing techniques for modern unified communications, with focus on cloud-based solutions and enterprise networks.
Ways to Die in Mobile OAuth
Comprehensive analysis of OAuth vulnerabilities in mobile apps, revealing widespread implementation flaws and security risks. Offers insights for developers to enhance mobile OAuth security.
How I Used to Rob Banks
Explore ethical hacking techniques and security vulnerabilities in banking systems through real-world stories and lessons from a professional penetration tester.
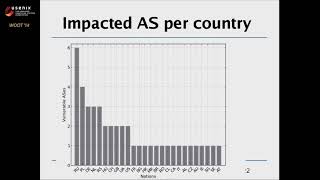
Through the Looking-Glass, and What Eve Found There
Exploring security vulnerabilities in looking-glass web applications used by Autonomous Systems, revealing potential exploits that could lead to remote command execution on backbone routers and compromise Internet infrastructure.
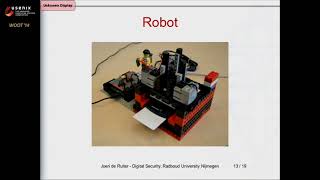
Automated Reverse Engineering Using Lego
Innovative use of Lego robots for automated reverse engineering of smartcard readers, revealing security vulnerabilities through state machine learning and fuzzing techniques.
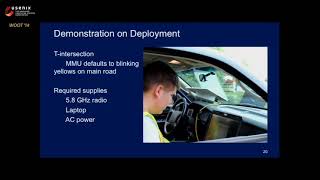
Green Lights Forever - Analyzing the Security of Traffic Infrastructure
Researchers expose security vulnerabilities in traffic signal systems, demonstrating potential for disruption and safety risks. Recommendations for improving embedded systems security are provided.
SoK - Decentralized Finance - DeFi Attacks
Comprehensive analysis of DeFi attack vectors, vulnerabilities, and security challenges in blockchain-based financial systems, offering insights for researchers and practitioners in the field.
Competitive Hacking as Team Sport - An Introduction to Capture the Flag
Discover virtual Capture the Flag: a team-based hacking competition exploring security vulnerabilities across various technologies. Learn to solve challenges and form teams for exciting weekend events.