Cognitive Security and Social Engineering: A Systems-Based Approach
Explore cognitive security's unique approach to protecting systems, considering interconnectedness and multiple scales. Learn about the Cognitive Security Attack Cycle and strategies for disrupting attacks.
The Zephyr Project Security Overview, Progress, and Status
Explore Zephyr's security journey, current improvements, and future plans. Learn about vulnerability management, from reporting to public disclosure through the CVE system.
TOTPs Are Not As Secure As You Might Believe
Explore vulnerabilities in Time-based One-Time Passwords (TOTPs) and learn strategies to enhance their security in authentication systems.
SUDO Security Policy Bypass Vulnerability - CVE-2019-14287
Explanation and demonstration of the sudo security policy bypass vulnerability (CVE-2019-14287), including how it works and can be exploited. Includes practical examples and technical details for cybersecurity professionals.
CVEs are Alive, but Do Not Panic! - Kernel Security Update 2024
Explore the world of CVEs in kernel security, understanding their impact and learning how to approach them without unnecessary alarm.
Bug Bounty Hunting - Ethical Hacking for Software Security
Explore legal hacking, vulnerability disclosure, and ethical security practices. Learn to write effective reports and analyze published exploits.
Breaking Bad Multifactor - MFA Bypasses and How to Assess the Risks
Explore MFA bypass techniques and risk assessment strategies to enhance cybersecurity defenses and protect against evolving threats in authentication systems.
Surprising Ways to Escalate Privileges in Entra ID
Explore common pitfalls and privilege escalation techniques in Entra ID. Learn to identify, prevent, and monitor security risks through practical demonstrations and expert insights.
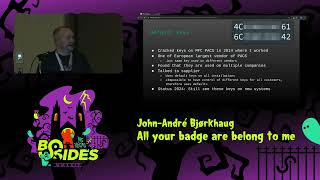
All Your Badge Are Belong to Us - Vulnerabilities in RFID Access Control Systems
Explore RFID access control vulnerabilities, their real-world exploitation, and implications. Gain insights into why insecure systems persist and learn key considerations for selecting secure solutions.
How We Accidentally Became Hardware Hackers - A Journey Through Cybersecurity
Journey from servers to hardware hacking: Two engineers share lessons learned through mistakes, encouraging aspiring hackers to embrace trial and error in hardware development and security.
Attacking Primary Refresh Tokens Using MacOS Implementation - TROOPERS24
Explore techniques for attacking Primary Refresh Tokens through MacOS implementation, presented by security experts at TROOPERS24 conference in Heidelberg.
Hacking Arcades for Fun - Insert Coin
Explore arcade game vulnerabilities and hacking techniques in this engaging talk on security flaws in gaming systems, offering insights for both enthusiasts and security professionals.
Is Embarrassing a Public Official via Security Disclosures a Hacking Crime?
Explore the legal and ethical implications of disclosing security vulnerabilities in government systems and the potential consequences for whistleblowers.
Updates of Yocto-Based Projects - YPDD 2023
Discover strategies for seamlessly updating Yocto-based projects, addressing security, minimizing debt, and integrating new features with practical examples.
Detecting and Fixing CVE Security Issues in Yocto-Based Embedded Linux Distributions - Mikko Rapeli
Detect and fix CVE security issues in Yocto-based embedded Linux distributions using CVE checker. Learn best practices, common problems, and effective solutions for maintaining high-quality software projects.
Rules of Engagement for Forking a Dependency
Explore guidelines for forking dependencies when facing security vulnerabilities, balancing community responsibility with timely fixes.
Making Community Decisions Without Consensus
Explore strategies for making critical community decisions when consensus is unattainable, using the Xen Project's approach to the XSA-7 security issue as a case study.
Physical Intrusion - Access Uncontrolled
Explore techniques and strategies for physical security breaches, focusing on unauthorized access methods and countermeasures in various environments.
What's in a Name? Exploring MojoBlob Registry and Service Side Dispatch
Explore MojoBlob Registry's code structure, service-side dispatch, and potential security vulnerabilities in Windows naming conventions.
GhostToken - Exploiting Google Cloud Platform to Create Unremovable Trojan Apps
Uncover a critical GCP vulnerability that enables malicious apps to become invisible and unremovable from Google user accounts, exploring OAuth 2.0, exploitation techniques, and security implications.
Data-Oriented Programming - On the Expressiveness of Non-Control Data Attacks
Explores data-oriented programming technique for non-control data attacks, demonstrating Turing-completeness and constructing expressive exploits in x86 programs, bypassing ASLR and DEP defenses.