Security for Non-Unicorns
Strategies for uncovering, preventing, and managing security issues in legacy systems and code for established companies. Practical approaches to improving security in non-startup environments.
Hunting For Bugs, Catching Dragons
Explore advanced techniques for identifying and exploiting software vulnerabilities, with insights from a renowned security researcher on discovering high-impact bugs.
Warning Ahead - Security Storms are Brewing in Your JavaScript
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 security concerns. Learn about emerging threats and their impact on enterprise security.
Ingress Egress - The Emerging Threats Posed by Augmented Reality Gaming
Explore emerging security threats from augmented reality games like Ingress, examining potential risks and vulnerabilities in this evolving digital landscape.
The Rise of the Citizen Developer - Assessing the Security Impact of Online App Generators
Assessing security risks of online app generators for citizen developers, revealing vulnerabilities in generated apps and their impact on the mobile ecosystem's overall health.
Mind the Gap - Studying the Insecurity of Provably Secure Embedded Trusted Execution Architectures
Explore vulnerabilities in embedded trusted execution architectures and learn about potential security gaps in provably secure systems.
What Happens in Windows 8 Stays in Windows 8
Explore Windows 8's security features and vulnerabilities in this DefCamp conference talk. Gain insights into the operating system's architecture and potential risks for information security professionals.
Anti Virus Firewall Bypass Techniques
Learn advanced techniques for bypassing antivirus and firewall systems, enhancing your cybersecurity skills and understanding of network protection vulnerabilities.
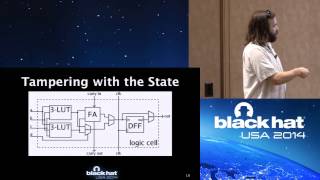
Secure Product Development
Explore hardware security validation techniques, Verilog vulnerabilities, and bug resolution methods in open-source core designs. Learn to identify and address security issues in integrated circuits.
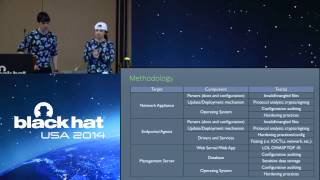
Stay Out of the Kitchen - A DLP Security Bake-Off
Explore flaws in Data Loss Prevention solutions, including administrative interfaces and inspection engines. Learn about vulnerabilities in DLP systems and their potential for bypass.
Libinjection - A C Library for SQLI Detection and Generation Through Lexical Analysis
Innovative C library for SQL injection detection using lexical analysis, offering high precision and accuracy. Trained on real attacks, it categorizes threats and provides templates for new attack detection.

Exploiting Lawful Intercept to Wiretap the Internet
Explores security vulnerabilities in Cisco's lawful intercept technology, demonstrating how attackers could exploit these weaknesses for unauthorized surveillance. Offers recommendations for network operators and interface redesign.
We Have You by the Gadgets
Explore Windows gadget platform vulnerabilities and attack vectors. Learn about creating malicious gadgets, exploiting legitimate ones, and uncovering flaws in published gadgets.

SSRF vs Business Critical Applications
Explore SSRF vulnerabilities in business-critical applications, focusing on SAP systems. Learn about XXE Tunneling and its potential to bypass security restrictions, with practical examples and attack scenarios.
Trust Transience - Post Intrusion SSH Hijacking
Explore post-intrusion SSH hijacking techniques and their implications for network security. Learn about trust transience and advanced exploitation methods in this cybersecurity deep dive.
Evading Deep Inspection for Fun and Shell
Explore TCP/IP reassembly vulnerabilities in security devices and learn evasion techniques to bypass deep packet inspection, potentially compromising network defenses.
Bluetooth Smart - The Good, The Bad, The Ugly, and The Fix
Comprehensive exploration of Bluetooth Smart technology, covering its design, vulnerabilities, and proposed security enhancements, with live demonstrations and open-source tool implementations.
Java & Java Virtual Machine Security Vulnerabilities & Exploitation Techniques
Explore Java and JVM security vulnerabilities, exploitation techniques, and potential risks in this comprehensive presentation by Last Stage of Delirium.
MS SQL Server Security Overview
Comprehensive overview of MS SQL Server security, covering authentication modes, vulnerabilities, discovery techniques, privilege escalation, and best practices for securing databases and preventing SQL injection attacks.
Professional Source Code Auditing
Comprehensive guide to professional source code auditing techniques, covering best practices, tools, and methodologies for identifying vulnerabilities and ensuring code security.
How to Fix a Broken Window
Learn techniques to repair and secure compromised Windows systems, focusing on practical methods for system administrators to restore functionality and enhance security.