Are You Deploying and Operating with Security in Mind?
Explore container security threats and mitigation strategies for Java applications. Learn about code scanning, dependency verification, and best practices for secure deployment and operation.
Assert Yourself - How to Leverage Security Tools to Increase Quality of Testing
Explore security testing concepts and learn to use open-source tools to enhance existing test strategies for web applications, demystifying vulnerabilities and integrating security into your workflow.
Cracking the Code to Secure Software
Learn principles from Domain Driven Design to create secure code while focusing on business features. Discover how to use Domain Primitives, Entity Snapshots, and security testing to harden your code and prevent Domain DoS attacks.
Start Writing Security Tests Now
Automate security testing in your application using frameworks to eliminate common vulnerabilities and streamline pentesting, focusing on complex security issues.
Security in the Delivery Pipeline
Modern approaches to integrate security testing throughout the software delivery pipeline, emphasizing continuous security practices for improved quality and safety in DevOps environments.
ToyFail
Exploring security and privacy concerns in internet-connected toys, revealing shocking findings from an investigation and sharing methods for testing device security.
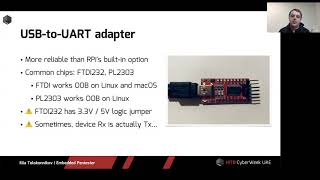
CI - CD With SAST And DAST For Embedded Devices
Explore automated security testing for embedded devices using FOSS, commercial tools, and creative solutions. Learn to implement CI/CD with SAST and DAST for multiple device families at scale.
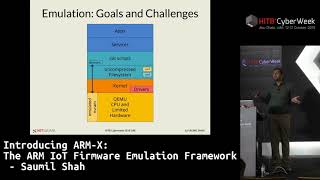
Introducing ARM-X - The ARM IoT Firmware Emulation Framework
Explore ARM-X, an IoT firmware emulation framework for testing and vulnerability discovery. Learn its evolution, use cases, and future directions in IoT security research and development.
House of Cards - How Not to Collapse When Bad Things Happen
Discover how to build resilient enterprise security by actively testing defenses, validating controls, and learning from simulated scenarios to prepare for real-world threats and challenges.
New Farming Methods for the Epistemological Wasteland of Application Security
Explore innovative approaches to application security, focusing on early-stage security testing and practical tools for immediate implementation in development processes and delivery pipelines.
Speeding Up Security Testing Panel
Panel discussion on accelerating security testing processes, featuring insights from industry experts on best practices, tools, and strategies for efficient vulnerability assessment.
Runtime Manipulation of Android and iOS Applications
Explore runtime analysis and manipulation techniques for mobile app security testing, focusing on tools for iOS and Android to enhance your mobile security toolbox.
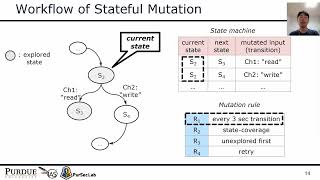
FuzzUSB - Hybrid Stateful Fuzzing of USB Gadget Stacks
Explore hybrid stateful fuzzing techniques for USB gadget stacks, enhancing security testing and vulnerability detection in USB device implementations.
Start Writing Security Tests Now
Learn methodologies and frameworks for automating security testing in your applications, enabling developers to address common vulnerabilities and collaborate more effectively with pentesters.
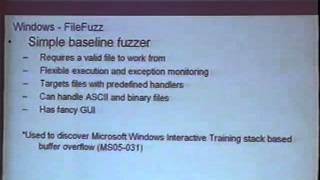
The Art of File Format Fuzzing
Explore advanced techniques for file format fuzzing, uncovering vulnerabilities in software applications through systematic input manipulation and analysis.
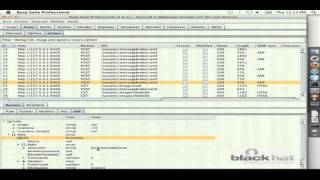
AMF Testing Made Easy
Reshaping AMF fuzzing with automated gray-box testing. Learn to build custom AMF messages, dynamically generate objects, and improve fuzzing coverage for complex applications using the Blazer Burp Suite plugin.
Fixing - Making Holes in Binaries
Explore techniques for modifying binary files to fix vulnerabilities or create new exploits. Learn about reverse engineering and binary manipulation for security research.
The Nessus Project
Explore the Nessus Project, a powerful vulnerability scanner, and learn about its features, capabilities, and applications in network security and penetration testing.
Realtime Communications, Realtime Risks
Explore WebSocket security risks, vulnerabilities in enterprise applications, and a new Burp Suite extension for improved pentesting of real-time communications.
Up and Running with Backtrack Workshop
Comprehensive workshop on utilizing Backtrack for ethical hacking and penetration testing, covering essential tools and techniques for cybersecurity professionals.
Intro to Scanning - Nmap, Hping, Amap, TCPDump, Metasploit, etc.
Learn essential network scanning tools like Nmap, Hping, Amap, TCPDump, and Metasploit for cybersecurity. Gain practical skills in network analysis and vulnerability assessment.