Annihilation Attacks for Multilinear Maps - Cryptanalysis of Indistinguishability Obfuscation over GG
Explore cryptanalysis techniques for multilinear maps and indistinguishability obfuscation, focusing on annihilation attacks and their implications for cryptographic security.
Separate Separations of CPA and Circular Security for Any Cycle Length
Explores circular insecurity in cryptography, focusing on cycle lengths in (Ring-)LWE. Covers applications, constructions, and separation techniques for enhancing cryptographic security.
Cryptanalyses of Candidate Branching Program Obfuscators
Explore cryptanalysis techniques for branching program obfuscators, examining vulnerabilities and potential attacks on these cryptographic constructions.
Toward Fine Grained Blackbox Separations Between Semantic and Circular Security Notions
Explores fine-grained blackbox separations between semantic and circular security notions in cryptography, discussing encryption, seed circular security, and fully blackbox constructions.
Cold Boot Attacks on Ring and Module LWE Keys Under the NTT
Explore cryptographic vulnerabilities in lattice-based schemes, focusing on cold boot attacks against Ring and Module LWE keys transformed by the Number Theoretic Transform.
On the Memory-Tightness of Hashed ElGamal
Explore the memory-tightness of Hashed ElGamal encryption, examining its security properties and implications for cryptographic systems.
The Kubernetes Bug Bounty Program - What Researchers and Users Need to Know
Explore Kubernetes' Bug Bounty Program: its implementation, scope, rewards, and impact on cluster security. Learn how researchers can contribute and users can benefit from this initiative.
Combining the Power of Builders and Breakers in Cybersecurity - USENIX Enigma 2018
Exploring the evolving relationship between companies and security researchers in bug bounty programs, examining challenges, benefits, and future implications for cybersecurity.
Event-based Fuzzing, Patch-based Research, and Comment Police - Finding Bugs Through a Bug
Discover innovative bug-hunting techniques: event-based fuzzing, patch analysis, and comment inspection. Learn to leverage known vulnerabilities for deeper security research in Chrome and Android.
ChatGPT and Cybersecurity - Will AI Replace Security Experts?
Explore SK쉴더스 EQST의 생성형 AI 해킹 위협 연구 결과와 사이버보안 분야에서의 ChatGPT 활용 가능성 및 한계점에 대한 전문가의 심층 분석과 통찰.
Prudent Evaluation Practices for Fuzzing - SoK
Explore best practices for evaluating fuzzing techniques in software security testing, focusing on methodologies and metrics for accurate assessment.
Secrets and Shadows: Leveraging Big Data for Vulnerability Discovery
Discover innovative approaches to large-scale vulnerability detection using unconventional data sources, focusing on forgotten cloud assets and leaked secrets to identify critical security weaknesses in major organizations.
Jens Spahn's Credit Score Is "Very Good"
Sicherheitsforschung als Methode direkter Aktion: Fallstudien zur Maximierung der Auswirkungen von Schwachstellen durch öffentliche Offenlegung, unter Berücksichtigung ethischer Aspekte und Sicherheit.
Empowering Security Teams with Generative AI: GPT Models - Lecture 12
Explore how GPT models and large language models can enhance security research through few-shot learning, code generation, and retrieval augmentation techniques for security teams.

The Darkest Side of Bug Bounty - Understanding Problems and Solutions in Bug Bounty Programs
Uncover the hidden challenges, secrets, and realities of bug bounty programs through expert insights on navigating relationships between hunters, clients, and platforms.
LinkDoor - A Hidden Attack Surface in the Android Netlink Kernel Modules
Explore Netlink vulnerabilities in Android kernel modules, uncovering security threats and exploitation techniques. Learn to analyze and mitigate risks in this overlooked attack surface.
RFID Security Research - Early Insights and Implications
Early RFID security research by Adam Laurie, exploring vulnerabilities in RFID passports and predicting the need for RFID-blocking wallets. A pioneering look at RFID technology's security implications.
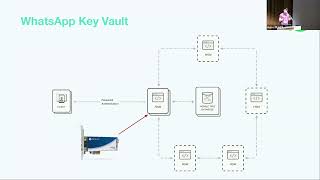
Building and Breaking Secure Systems
Explore techniques for constructing and deconstructing secure systems, focusing on vulnerabilities, attack methods, and robust defense strategies.
Empowering Security Teams with Generative AI: Fundamentals and Applications of GPT Models
Explore how GPT models can enhance security research through few-shot learning, code generation, and retrieval augmentation. Gain insights and practical examples to leverage AI in empowering security teams.
Entendendo o Cybersecurity Color Wheel - Conceitos e Aplicações
Explore a roda de cores da segurança cibernética, uma representação simbólica dos aspectos multifacetados da proteção digital, com especialistas em cibersegurança e pesquisa de segurança.
Credential Management Strategies and Obstacles During Password Manager Setup
Explore user behaviors and challenges in password manager adoption, focusing on setup strategies, security implications, and recommendations for improving credential management systems.