Demystifying the Secure Enclave Processor
Explore Apple's Secure Enclave Processor: its hardware design, SEPOS architecture, data exchange mechanisms, and potential vulnerabilities in this in-depth technical analysis.
Keystone Engine - Next Generation Assembler Framework
Explore Keystone, a multi-architecture assembler engine with clean API, native support for various platforms, and bindings for multiple programming languages. Ideal for reverse engineering and security research.
DPTrace - Dual Purpose Trace for Exploitability Analysis of Program Crashes
Explore advanced crash analysis techniques combining backward and forward taint propagation to enhance exploitability assessment and speed up vulnerability triage for security researchers and exploit writers.
Smart Speaker Shenanigans - Making the SONOS One Sing
Exploring ARM Trusted Firmware, secure boot, and encryption vulnerabilities in smart devices. Demonstrates exploits on Lenovo clock and SONOS One, revealing secrets and breaking security boundaries.
Breaking the Black-Box Security Coprocessor in the Nintendo Switch - A Story of Vulnerability After Vulnerability
Explore the process of exploiting vulnerabilities in the Nintendo Switch's security coprocessor, leading to arbitrary code execution at the highest security level.
Breaking Managed Data Services in the Cloud
Exploring vulnerabilities in core cloud infrastructure, revealing cross-tenant boundary breaches in major cloud vendors' services and their potential impact on customer security.
Security Audits as an Integral Part of PHP App Development
Learn to integrate security audits into PHP application development, uncovering vulnerabilities and enhancing overall software security through expert insights and practical implementation strategies.
MacOS Security - Escaping The Sandbox & Bypassing TCC
Explore macOS security measures, including sandboxing and TCC, and learn about potential vulnerabilities and bypass techniques in third-party applications and system components.
Spoofing Your Location on iOS Without Jailbreaking
Explore a physical hardware device for GPS spoofing on non-jailbroken iPhones, offering a flexible and accurate solution beyond traditional app-based methods.
God Mode Unlocked - Hardware Backdoors in x86 CPUs
Unveiling a critical hardware backdoor in x86 CPUs allowing unprivileged users to bypass security checks and escalate to kernel-level access. Explores detection, prevention, and broader implications for processor security.
An Open-Source Toolkit for Model-Based Fuzzing of ARM CPUs
Explore model-based fuzzing for ARM CPUs using machine-parsable reference manuals. Learn about Scapula, an open-source tool for detecting specification violations in ARM-based platforms.
Launching Feedback-Driven Fuzzing on TrustZone TEE
Exploring TrustZone vulnerabilities in Samsung Galaxy smartphones using feedback-driven fuzzing on Trustonic trustlets, revealing potential security breaches in ARM's hardware isolation technology.
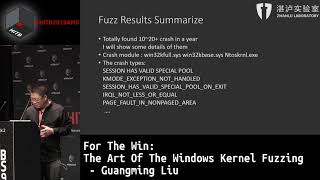
For The Win - The Art of the Windows Kernel Fuzzing
Explore advanced Windows kernel fuzzing techniques, including a new method and custom tool for discovering vulnerabilities in kernel objects and their relationships.
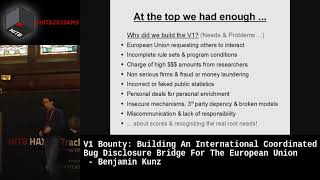
Bounty - Building a Coordinated Bug Disclosure Bridge for the EU
Exploring the creation of a new EU-endorsed bug bounty platform, focusing on international collaboration, security standards, and benefits for both hunters and companies.
Adventures in Security Research
Explore defensive security, journalism protection, and diverse tech challenges with insights on gun hacking, malware analysis, and mission-driven work from a seasoned security expert.
ProxyLogon is Just the Tip of the Iceberg - A New Attack Surface on Microsoft Exchange Server
Discover a new attack surface on Microsoft Exchange Server, exploring critical vulnerabilities beyond ProxyLogon and their implications for government and enterprise security.
iOS Kernel PAC, One Year Later
Análisis de la evolución y vulnerabilidades de la autenticación de punteros del kernel de iOS, con demostraciones de nuevos métodos para eludir la seguridad en iOS 13.3.
They're All Scorpions - Successful SecOps in a Hostile Workplace
Explore innovative approaches to SecOps in challenging business environments. Learn new security practices and research to effectively manage operations despite limited resources and organizational resistance.
Security Research Teams - How To Manage, Grow And Retain Them
Estrategias para gestionar, desarrollar y retener equipos de investigación en seguridad, abordando desafíos como la contratación, motivación y alineación con objetivos empresariales.
Flawed, but Like Democracy We Don't Have a Better System - The Experts' Insights on the Peer Review Process of Evaluating Security Papers
Experts discuss insights on the peer review process for security papers, exploring flaws and potential improvements in academic evaluation.
Ethics in Security and Privacy Research Panel
Explore ethical considerations in security and privacy research through expert insights and discussions on best practices, challenges, and future directions.