When CAN CANT
Explore CAN bus vulnerabilities and CANT software for automotive security research. Learn error handling, selective attacks, and advanced techniques for vehicle hacking and defense.
Opening Closed Systems With GlitchKit
Explore GlitchKit, an open-source solution for fault injection in closed systems. Learn techniques to bypass firmware protection and extract secrets through hardware hacking and reverse engineering.
Embedded Device Vulnerability Analysis Case Study Using Trommel
Comprehensive methodology for embedded device vulnerability analysis, covering firmware, web app, mobile app, and hardware. Includes case study and TROMMEL tool introduction.
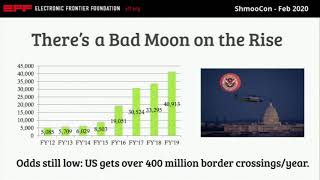
Crossing the Border With Your Electronic Devices
Explore legal and technological aspects of protecting digital privacy during border crossings, with insights on device security and traveler rights.
The Art of Exploiting UAF by Ret2bpf in Android Kernel
Explore Android kernel exploitation techniques, focusing on a Use-After-Free vulnerability in xt_qtaguid. Learn about KASLR bypass, rooting methods, and security measures against such attacks.
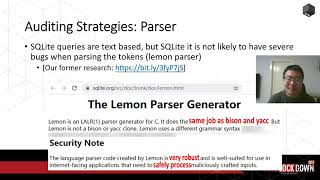
Exploring and Exploiting the SQLite
Explore SQLite vulnerabilities, auditing strategies, and fuzzing techniques. Learn about Magellan 2.0, shadow tables, and bypassing defense mechanisms for remote code execution in Chrome and SQLite binaries.
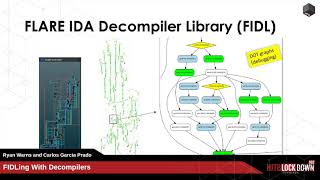
FIDLing with Decompilers
Explore decompilation basics, popular tools, and the Hex-Rays Decompiler. Learn about FIDL, a new library simplifying decompiler API usage, with practical examples and demos.
Bugrank - A Community Bug Bounty Platform
Introducing Bugrank: an open-source community bug bounty platform. Explore its design, architecture, and functions. Learn how to set up your own bug reporting system for enhanced cybersecurity.
The Insecurity of Cloudless Smart Door Systems
Explore vulnerabilities in cloudless smart door systems for large buildings, focusing on IP-gateway security risks and potential exploits in intercom-IP integration.
Radio Exploitation 101
Explore radio exploitation fundamentals, wireless attack types, and live demos. Learn to bridge IP network skills to wireless domain, understanding mechanics and awareness of radio-based network vulnerabilities.
Hacking in the Far East
Explore security challenges and hacking techniques in Japan, South Korea, and Hong Kong. Gain insights into corporate policies, smart cards, social engineering, and unique cultural aspects affecting cybersecurity in East Asia.
ARTist - A Novel Instrumentation Framework for Reversing and Analyzing Android Apps and the Middleware
Explore Android Runtime security with ARTist, a novel instrumentation framework for analyzing apps and middleware. Learn deployment, modules, and creation techniques.
Analyzing and Fuzzing for Qualcomm Hexagon Processor
Explore techniques for analyzing and fuzzing Qualcomm Hexagon processors, overcoming challenges in firmware analysis, emulation, and hardware-dependent targets for enhanced security research.
Hunting and Exploiting Recursive MMIO Flaws in QEMU KVM
Explore security vulnerabilities in QEMU/KVM hypervisors caused by recursive MMIO handling, uncovering a new attack surface with potential for critical exploits in cloud computing environments.
How the Wassenaar Arrangement's Export Control of "Intrusion Software" Affects Industry
Experts discuss implications of Wassenaar Arrangement's export control on "intrusion software" for cybersecurity industry, research, and privacy, drawing parallels to 1990s crypto wars.
Windows Kernel Graphics Driver Attack Surface
Explore the attack surface of Windows graphics drivers, including exposed ioctl's, driver internals, and security implications for researchers and developers.
The Big Chill - Legal Landmines that Stifle Security Research and How to Disarm Them
Legal challenges and risks in security research: exploring laws, cases, and potential solutions to protect researchers while promoting cybersecurity advancements.
PWNIE Awards
Celebrating excellence in information security with humor and recognition for groundbreaking achievements and epic fails in the cybersecurity industry.
Bypass Surgery - Abusing Content Delivery Networks
Exploring vulnerabilities in CDNs, this talk reveals attack patterns against high-availability websites, demonstrating potential risks and exploit development with far-reaching consequences.
A Pre-Auth RCE on Leading SSL VPNs
Unveiling critical vulnerabilities in leading SSL VPNs, including pre-auth RCEs and backdoors. Demonstrating exploitation techniques, post-exploitation strategies, and discussing mitigation measures for enterprise security.
Patchwerk - Kernel Patching for Fun and Profit
Explore techniques for patching and securing Linux kernels on IoT devices without source code. Learn to inspect, compile, and apply patches to vendor OEM kernels for vulnerability mitigation and reverse engineering.