Cybersecurity Tips, Tools and Techniques for Your Professional Toolbag
Rapid-fire showcase of cybersecurity apps, tools, and advanced techniques for testing, investigations, and administration. Optimize open-source tools for Windows and Linux to enhance your security program.
Granular Trust - Making It Work
Explore granular trust models for enhanced security, covering authentication, access levels, and emergency protocols. Learn to implement flexible, context-aware security systems.
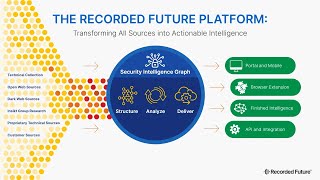
Intelligence Led Security Operations in Microsoft Azure Sentinel
Integrate Recorded Future with Azure Sentinel to quickly identify, prioritize, and action threats using external threat intelligence, maximizing existing security investments.
Unraveling the Recipe for Resilient Enterprise Security Operations
Explore strategies for resilient enterprise security operations, focusing on informed decision-making during critical incidents like ransomware attacks. Learn about risk indicators and active defense techniques.
Incident Response
Explore incident response and threat intelligence with Palo Alto Networks' SVP Wendi Whitmore, discussing cybersecurity consulting, ransomware trends, and prevention strategies.
Your Metrics Suck - 5 SecOps Metrics That Are Better Than MTTR
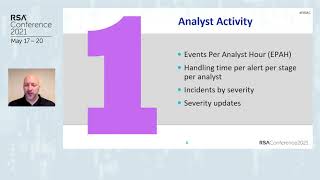
Explore effective SecOps metrics beyond MTTR, focusing on business confidence, driving change, and improving SOC performance. Learn about configuration, analyst activity, and process deviation.
The Network Is Going Dark - Why Decryption Matters for SecOps
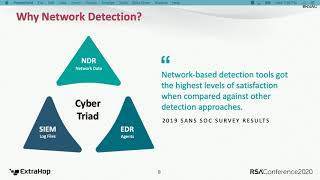
Explore strategies for decrypting encrypted network traffic, focusing on TLS 1.3 challenges and solutions like SSL fingerprinting and session-key forwarding for effective network security operations.
5G Trust Model - Recommendations and Best Practices for CSPs
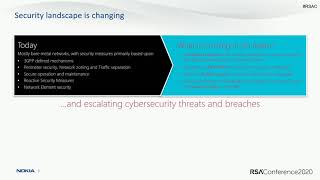
Explore 5G security paradigms, best practices, and recommendations for CSPs. Learn about new approaches, AI utilization, integration, orchestration, and automation in 5G security.
Embracing the Uncertainty of Attacks with Big Data Analytics
Exploring big data analytics to combat advanced cyber threats, reduce uncertainty, and transform security programs through intelligence-driven detection approaches and innovative strategies.
Back to the SOCless Future
Explore Twilio's journey towards automated security operations, featuring insights on scalable 24/7 monitoring and a serverless automation framework for effective threat response.
Experimenting with Real-Time Event Feeds
Explore innovative approaches to real-time event feeds in cybersecurity, challenging traditional SIEM methods and addressing high-volume data management for improved threat detection.
Adversary Detection Pipelines - Finally Making Your Threat Intel Useful
Learn to extract value from threat intelligence by implementing Adversary Detection Pipelines. Explore attribution challenges, leverage TTPs, and enhance security operations through practical case studies and intelligence-driven strategies.
Lessons Learned While Building a Privacy Operations Center at Headspace Health
Insights on creating a Privacy Operations Center in digital healthcare, addressing global regulations and overcoming challenges in data protection and compliance.
Teamwork and Security in Our Integrated Society
Explore the interdependence of security and societal attitudes with a retired FBI agent. Learn how teamwork can combat isolation and enhance safety in our integrated world.

Security Onion Cases - Introduction to Case Management Interface
Explore the new case management interface in Security Onion 2.3.100, enhancing investigation workflows and guiding future analyses with integrated platform features.

SOARing with Security Onion
Explore how Security Onion integrates with automation tools for enhanced incident response, enabling faster threat detection and improved security operations efficiency.
Constructing Your Playbook within Security Onion
Learn to build an effective security playbook using Security Onion, covering integration, shared resources, detections, templates, and Elastic Search for enhanced threat response.
Blue Team Visibility
Explore strategies for enhancing blue team threat detection capabilities, leveraging multiple data sources to stay ahead of sophisticated attackers in an ever-evolving cybersecurity landscape.
Empathy and Vulnerability in SecOps
Explore how empathy and vulnerability enhance SecOps, improving team collaboration, incident response, and security awareness programs for more effective and resilient operations.
Incident Response at Scale - Building a Next Generation SOC
Explore strategies for automating incident response processes in large-scale environments to improve efficiency, visibility, and organizational protection.
Adversary Detection Pipelines - Finally Making Your Threat Intel Useful
Learn to maximize your threat intelligence program's value, enhancing security across teams with practical strategies for effective adversary detection and intel utilization.