Honeypots 2.0 - A New Twist on Defending Enterprise Networks
Explore dynamic deception at scale using Python's Twisted framework for enhanced network defense, focusing on scalable honeypot technologies and their implementation in enterprise environments.
Six Degrees of Infiltration - Using Graph to Understand Your Infrastructure and Optimize Security Decision Making
Explore graph-based solutions for consolidating security intelligence and improving decision-making in complex infrastructures, using tools like Neo4j to enhance visibility and risk assessment.
The Bucket List - Experiences Operating S3 Honeypots
Insights from operating S3 honeypots: Discover who's hunting for exposed buckets, their methods, and how to protect your AWS assets through monitoring and defensive strategies.
Introduction to Windows Kernel Mode Debugging
Explore Windows kernel debugging essentials, including symbol servers, BSOD analysis, and live debugging. Learn practical approaches to diagnose CPU issues, deadlocks, and blue screens for improved software security.
An Open Source Malware Classifier and Dataset
Explore open-source malware classification using machine learning, featuring a diverse Windows PE file dataset, pre-trained models, and reproducible code for enhanced static malware detection research.
Crimeware Chaos - Empirical Analysis of HTTP-Based Botnet C&C Panels
Empirical analysis of HTTP-based botnet C&C panels, exploring design, technologies, and characteristics of crimeware control systems used by cybercriminals for managing botnets and other malicious operations.
Pensieve - Finding Malicious Artifacts in Container Environments
Explore techniques for forensic investigation in container environments, focusing on evidence retention and artifact gathering to understand adversarial activities.
Fighting Secrets in Source Code with TruffleHog
Discover TruffleHog: a tool for identifying secrets in source code, its applications in DevOps, and new approaches to detecting secrets in package managers like npm and pypi.
Data Driven Bug Bounty
Explore data-driven bug bounty programs: collecting metrics, analyzing vulnerabilities, and leveraging insights to enhance security processes and address weak spots effectively.
Netrepser - A JavaScript Targeted Attack
Explore Netrepser, a unique JavaScript-based espionage tool using freeware utilities for targeted attacks. Learn its techniques, impact, and how it blends into environments for data exfiltration.
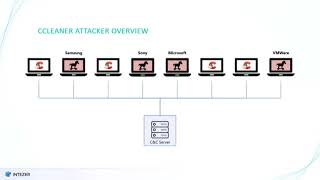
Supply Chain Attack Through CCleaner - Evidence Aurora Operation Still Active
Análisis detallado del ataque de cadena de suministro a CCleaner, explorando su sofisticación, objetivos y conexiones con el grupo APT17/Axiom, destacando la persistente amenaza de ataques estatales avanzados.
Starting a Security Program - Thrills and Spills
Insights on building a security program, emphasizing emotional intelligence, cross-team collaboration, and shared responsibility to achieve compliance and meet customer demands.
A Case Study of MacOS Supply Chain Compromise
Explore MacOS supply chain vulnerabilities and learn proactive defense strategies using open-source tools for threat detection and malware identification in network environments.
Building a Predictive Pipeline to Rapidly Detect Phishing Domains
Learn to build a predictive pipeline using Python and machine learning to detect phishing domains in real-time, leveraging Certificate Transparency logs and supervised learning techniques.
Security through Visibility - Organizational Communication Strategies for InfoSec Teams
Strategies for InfoSec teams to improve organizational visibility and communication, enhancing collaboration and security posture through practical, implementable techniques.
Building an Effective Intrusion Detection Program
Learn to build an effective intrusion detection program using affordable tools. Covers cloud apps, endpoints, network security monitoring, and crowdsourced incident response to catch breaches quickly.
Make Alerts Great Again
Strategies for creating effective, actionable security alerts: improving signal-to-noise ratio, standardizing definitions, and implementing self-service tools to enhance team efficiency and incident response.
The Cyber Insurance Emperor Has No Clothes
Explore the flaws in cyber insurance and its impact on security incentives, with insights on better alternatives for improving cybersecurity practices.
From Cockroaches to Marble Floors - What Happens When You Turn On the Lights?
Practical tools and methodologies to transform software security posture by eliminating false distinctions between security bugs and other defects, improving product quality and aligning teams.
Transform Your Presentation Skills
Enhance your public speaking with expert tips on confidence, audience engagement, and effective slide design for impactful presentations in the tech industry.
The GCP Metadata API - Security Considerations, Vulnerabilities, and Remediations
Explore GCP Metadata API security: risks, attacks, defenses, and best practices. Learn about service accounts, Kubernetes, and Cloud Build implications for your organization's cloud infrastructure.