Replacing Privileged Users with Just-in-Time Access Requests
Learn how to implement just-in-time access requests to enhance security and reduce privileged user risks in your organization's infrastructure.
Navigating the AI Frontier: Investing in AI in the Evolving Cyber Landscape
Explore AI's impact on cybersecurity through an investor's perspective, covering automation opportunities, ethical considerations, and risk management strategies for responsible AI deployment.

Implementation of DevSecOps in Cloud Engineering
Streamline cloud security with DevSecOps: automate processes, implement continuous monitoring, and integrate compliance as code for agile and secure deployments.
Securing the Software Supply Chain: Challenges and Solutions
Learn strategies to secure the software supply chain against attacks, prioritize security measures, and protect your organization from catastrophic data breaches.
Removing AWS Policy Review Fatigue with Automated Terraform Resource Analysis
Automate AWS policy control with Terraform resource analysis, reducing security review fatigue and improving developer productivity through early-stage static analysis in IaC pipelines.
The State of DevSecOps in 2023 - Challenges and AI Solutions
Explore DevSecOps failures and AI solutions in 2023. Gain insights from Ashish Rajan's 13+ years of cybersecurity experience, focusing on cloud security and enterprise risk management at scale.
What's Next for Security Professionals - Innovations in Threat Prevention and AI-Driven Security
Explore the convergence of security capabilities, AI-driven innovations, and insights from industry leaders to transform your organization's security approach.
Who Secures Our Code When an Army of Robots Is Writing It? - DevOps Security Challenges in AI-Driven Development
Explore challenges and solutions for securing AI-generated code, including paved roads, runtime protection, and security tool copilots. Learn about CodeModder, an open-source library for modern code modification.
How Security Can Keep Pace with Continuously Evolving Cloud-Native Applications
Explore dynamic security approaches for cloud-native apps, aligning with modern development lifecycles and infrastructure-as-code to ensure security evolves alongside rapid architectural changes.
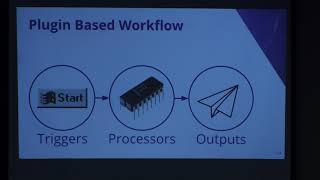
Orchestrating Security Tools with AWS Step Functions - 2018
Automate security reviews in CI/CD pipelines using AWS Step Functions. Learn to deploy serverless systems for integrating security tools like static analysis and container scanning into developer workflows.
Manual JavaScript Analysis is a Bug - Automating Security Assessments for Modern Web Applications
Automate JavaScript security assessments: Learn efficient methods for analyzing modern web apps, focusing on key areas and streamlining the process for better results.
Securing the Golden Path: Adding Guardrails for Developers Without Compromising Agility
Panel discussion on balancing security and agility in cloud-native development, exploring strategies for implementing guardrails without hindering developer productivity.
Dynamic Security Group Recommendations with Grouper and Dredge
Explore Netflix's innovative approach to AWS security group management using Grouper and Dredge, enhancing developer insights and ensuring least privilege network access.
OWASP ZAP Advanced Features for Web Application Security Testing
Explore advanced features of OWASP ZAP for web application security testing, including handling non-standard apps, client-side testing, fuzzing, scripting, and more with expert Simon Bennetts.
Using the O2 Platform to Automate Application Security Knowledge and Workflows
Explore the O2 platform for automating web application security reviews, enhancing visibility, and streamlining security workflows for both experts and non-experts.
OWASP Zed Attack Proxy: Latest Features and Developments - Lecture
Explore web application security with OWASP's Zed Attack Proxy. Learn key features, including Plug-n-Hack and Zest scripting, suitable for both novice and experienced penetration testers.
Building a Day1/Day2 Application Operations Platform on CNCF Projects
Explore building self-service platforms for cloud-native applications using CNCF projects. Learn about application lifecycle management, from development to operations, with practical examples and best practices.
ATOR - Authentication Token Obtain and Replace Burp Plugin V3
Streamline complex authentication testing with ATOR v3 Burp Plugin. Automate token handling, OTP validation for JavaScript frameworks. Simplifies configuration and debugging for efficient security assessments.
SOAR with Postee - Automated Incident Response for Cloud Native Risks
Automate incident response for cloud-native risks using Postee, enhancing security operations and streamlining threat management in modern infrastructures.
Microsoft Defender: Stop Attacks and Reduce Security Operations Workload with XDR
Comprehensive XDR solution preventing attacks, detecting threats, and automating security operations. Integrates Microsoft 365 Defender and Azure Defender for proactive threat hunting and customized detection tools.
Kubernetes Policy, Governance, and Compliance - A Working Group Policy Update
Explore Kubernetes policy management for simplified multi-cluster operations, automated security, and continuous compliance. Learn about the Policy Working Group's projects and how to contribute.