A Pragmatic Approach for Internal Security Partnerships
Strategies for effective security partnerships with engineering teams, focusing on shared risk views, automation, and integrating security into product roadmaps.
Baking Security Into the Software Development Lifecycle - CISO Panel
CISOs discuss strategies for integrating security into rapid application development, sharing real-world experiences on managing evolving methodologies and pressures to publish securely.
DevSecOps Roundup - An Overview of the Current State
Explore the current landscape of DevSecOps, examining key trends, challenges, and best practices in integrating security into the software development lifecycle.
Making Vulnerability Management Less Painful with DefectDojo
Streamline vulnerability management with DefectDojo: automate deduplication, reporting, and metrics for efficient AppSec programs. Learn how this open-source tool simplifies tedious tasks and enhances team productivity.
DASTProxy: Automated Security Testing Focused on Business Context
Explore DASTProxy: a tool for automated security testing that focuses on business context rather than crawling, enhancing efficiency and effectiveness in application security assessments.
Monitoring Application Attack Surface to Integrate Security into DevOps Pipelines
Explore integrating security into DevOps pipelines through application attack surface monitoring. Learn strategies from a recognized expert to enhance your organization's software security practices.
Automated Cyber Security Platform at Scale
Explore the vision and demo of an open-source Automated Security Platform, addressing sophisticated threats through security orchestration and automation to overcome data and process overload.
Securing Third Party Applications at Scale - AppSecCali 2019
Learn best practices for securing third-party applications at scale, including tooling, processes, and manual reviews. Gain insights from Salesforce's experience in reviewing over 4000 AppExchange applications to prevent vulnerabilities.
Leave It to the Machines - AI and ML in Container Security
Explore how AI and ML empower security teams to proactively secure container-based applications, shifting left security capabilities and streamlining the development process.
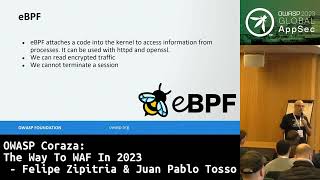
OWASP Coraza: The Way to WAF in 2023
Explore OWASP Coraza, a cutting-edge Web Application Firewall (WAF) solution, and learn how it enhances web security in 2023 through advanced features and implementation strategies.
OWASP DSOMM Project - Introduction to DevSecOps Maturity Model
Explore the OWASP DSOMM Project, a framework for enhancing software security practices and measuring DevSecOps maturity in organizations.
OWASP DefectDojo Project
Explore DefectDojo, an open-source vulnerability management tool. Learn its features, implementation, and how it streamlines security testing workflows for development teams.
Prevent Business Logic Attacks Using Dynamic Instrumentation
Dynamic instrumentation for preventing business logic attacks: Add sensors to source code, collect events, and automate responses in real-time. Extensible tool using open-source libraries, applicable across teams for tailored application security.
OWASP Glue Tool: Security Automation Made Easier
Learn about OWASP Glue Tool, a Ruby gem for security automation that coordinates multiple analysis tools and generates reports, simplifying the process of integrating security into development workflows.
Robots with Pentest Recipes - Automating Security Testing in DevOps
Explore automated security testing using Robot Framework to integrate tools like OWASP ZAP and Nmap. Learn to create easy-to-write test recipes for continuous delivery pipelines, enabling cross-team collaboration in application security.
Design Approaches for Security Automation
Explore criteria for designing and evaluating security automation tools, including build vs. buy decisions, deployment strategies, and effective implementation for organizational needs.
Enterprise-wide SSL Automation with Lemur and CloudCA
Explore enterprise-wide SSL automation using Lemur and CloudCA, enabling developers to easily manage SSL certificates and enhance security across applications.
Making Security Agile in CI/CD Environments
Integrating security into agile development and CI/CD pipelines. Learn strategies to automate security processes, leverage QA tests, and utilize tools for improved productivity in application security.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Adaptive Testing Methodology: Crowdsourced Testing for Customized Target Stack
Discover an efficient, customizable pentesting methodology that adapts to specific technology stacks and time constraints, improving consistency and effectiveness in vulnerability detection.
An SDLC for the DevSecOps Era
Explore an SDLC tailored for the DevSecOps era with insights on integrating security into modern development practices and organizational culture.