GitHub + Azure - Better Together
Explore GitHub and Azure integration for enhanced DevOps, focusing on secure development, automated delivery, and cloud deployment using GitHub Actions and Azure services.
How to Prepare for CSSLP Exam - CSSLP Exam Tips - Tips to Pass the CSSLP Exam
Expert guidance on CSSLP exam preparation, covering exam parameters, strategies, and key domains. Learn essential tips to excel in this prestigious application security certification.
Securing Software by Construction: From Research to Industry - Philly ETE 2016
Explore techniques for building secure software from the ground up, bridging the gap between academic research and industry practice in cybersecurity, and addressing challenges in commercializing long-term security solutions.
Bug Bounties and the Path to Secure Software Development
Explore bug bounties and vulnerability disclosure policies for secure software development, including implementation strategies, benefits, and best practices.
Climbing AppSec Mountains - How to Summit and Overcome Corporate Roadblocks
Explore strategies for overcoming corporate roadblocks in application security, focusing on early involvement in the software development lifecycle to prevent vulnerabilities and improve software quality.

Introduction to Inner-Loop Security - Shifting Left, but Better
Explore inner-loop security as the next evolution of "shift left," enabling developers to build secure-by-design products through improved methodologies and tools.
Dependency Hijacking Vulnerability in Microsoft Teams - Supply Chain Security Gaps
Explore real-world dependency hijacking in Microsoft Teams, understanding software supply chain vulnerabilities and learning strategies to protect infrastructure, SDLC, and code.
Trusted Types: End-to-End Injection Safety at Scale
Learn about Google's approach to achieving high-level XSS safety through integrated tools and developer-friendly practices, with insights on implementing similar security in open-source stacks.
SAASY SPLC - Secure Application Architecture for Software Product Line Configurations
Explore secure software development lifecycle practices for SaaS applications, focusing on unique challenges and effective strategies in cloud-based environments.
Idiot Proof Is Not Enough: Make It Villain Proof - Application Security
Learn strategies to secure applications against sophisticated attackers, going beyond basic safeguards to create robust, villain-proof systems.
PCI DSS and Secure Applications - Best Practices for Compliance
Explore best practices for developing secure applications compliant with PCI DSS requirements. Learn key practices, testing procedures, and evidence needed to meet compliance standards in payment card environments.
BSIMM: A Decade of Software Security Evolution - Keynote
Explore the evolution of software security over a decade, from early concepts to modern practices, highlighting the BSIMM framework for measuring and improving security initiatives in software development.
Google SLSA and NIST SSDF - Emerging Software Supply Chain Security Best Practices
Explore emerging best practices for software supply chain security, focusing on Google's SLSA framework and NIST's SSDF guidelines to enhance your organization's cybersecurity posture.
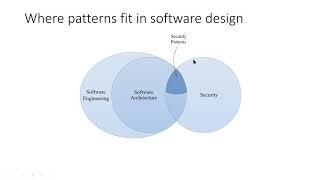
Building Secure Software Systems Using Security Patterns
Learn to create secure software systems using proven security patterns, enhancing your ability to design robust and protected applications in today's cybersecurity landscape.
OWASP SAMM - Interactive Introduction and Update
Explore OWASP SAMM, a framework for software assurance maturity modeling, with interactive insights and updates from industry experts.
The Internet is Broken: Breaking Down the Software Supply Chain
Explore modern software vulnerabilities, recent supply chain attacks, and actionable steps to build secure applications in an insecure internet environment.
Reproducible Builds with BuildKit for Software Supply Chain Security
Learn how BuildKit enables reproducible builds to enhance software supply chain security, ensuring verifiable and trustworthy Docker images through bit-for-bit identical reproduction from source code.
Beyond Guidelines - Designing and Implementing Robust Build Pipelines
Learn to design and implement secure build pipelines beyond standard guidelines. Explore practical tools and methods to enhance supply chain security and protect against rising attacks.
Every Journey to Securing the Software Supply Chain Starts with a Single Step
Explore NYU's journey in software supply chain security, uncovering challenges, best practices, and a roadmap for enhancing software security.
How Hacking Works - Web Edition
Explore web exploitation techniques and tools to enhance software security. Learn through gamified environments to build skills for safer development practices.
We Are Doing It Wrong: Threat Modeling
Explore common pitfalls in threat modeling and learn how to avoid them. Gain insights from real-world breaches and discover effective strategies for securing software development.