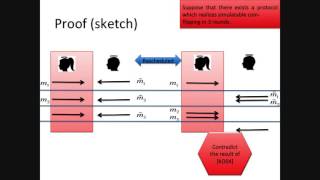
The Exact Round Complexity of Secure Computation
Explore the precise round complexity in secure computation, examining theoretical foundations and practical implications for cryptographic protocols.
Secure Computation from Elastic Noisy Channels
Explore secure computation using elastic noisy channels, covering ideal and real-world scenarios, unfair noisy channels, elastic erasure channels, and elastic binary symmetric channels.
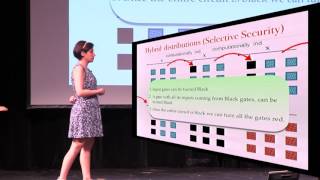
Adaptively Secure Garbled Circuits from One Way Functions
Explore adaptive security in garbled circuits, examining complexity, hybrid approaches, and encryption strategies for enhanced cryptographic protocols.
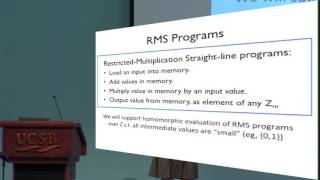
Breaking the Circuit Size Barrier for Secure Computation Under DDH
Explore secure computation techniques breaking circuit size barriers, including homomorphic encryption and secret sharing, with applications in branching programs and two-party computation.
TWORAM - Efficient Oblivious RAM in Two Rounds with Applications to Searchable Encryption
Explore efficient oblivious RAM techniques, their applications in searchable encryption, and advancements in non-interactive ORAM, focusing on the TWORAM algorithm and its impact on adaptive computation.
Two Message Oblivious Evaluation of Cryptographic Functionalities
Explore secure two-message protocols for oblivious evaluation of cryptographic functions, enhancing privacy and efficiency in multi-party computations.
On the Communication Required for Unconditionally Secure Multiplication
Explore unconditionally secure multiplication protocols, analyzing communication requirements and theoretical implications in cryptographic systems.
Size-Hiding Computation for Multiple Parties
Explore secure multi-party computation techniques for hiding data sizes, with applications in privacy-preserving data analysis and secure information sharing protocols.
Reactive Garbling - Foundation, Instantiation, Application
Explore reactive garbling schemes, their foundations, implementations, and applications in cryptography. Learn about secure computation techniques and their practical uses.
Constant Round Asynchronous Multi Party Computation Based on One Way Functions
Explore constant-round asynchronous multi-party computation protocols using one-way functions, enhancing secure distributed computing in asynchronous networks.
Group Based Secure Computation - Optimizing Rounds, Communication, and Computation
Explore optimizations for group-based secure computation, focusing on rounds, communication, and computation efficiency. Learn about homomorphic secret sharing and cryptographic frameworks.
Unconditional UC Secure Computation with Stronger Malicious PUFs
Explore unconditional UC secure computation using stronger malicious PUFs, as presented at Eurocrypt 2017. Learn about advancements in cryptographic protocols and their implications.
Improved Private Set Intersection against Malicious Adversaries
Explore advanced techniques for secure private set intersection, focusing on enhanced protection against malicious adversaries in cryptographic protocols.
Maliciously Secure Oblivious Linear Function Evaluation with Constant Overhead
Explore advanced cryptographic techniques for secure oblivious linear function evaluation, focusing on malicious security and constant overhead improvements.
JIMU Faster LEGO Based Secure Computation Using Additive Homomorphic Hashes
Explore a novel secure computation technique using additive homomorphic hashes, enhancing LEGO-based protocols for improved efficiency and security in cryptographic applications.
Overlaying Conditional Circuit Clauses for Secure Computation
Explore innovative techniques for enhancing secure computation through conditional circuit clause overlays, improving efficiency and functionality in cryptographic protocols.
Two-Round Multiparty Secure Computation from Minimal Assumptions
Explore minimal assumptions for two-round multiparty secure computation, covering protocol design, garbled circuits, and oblivious transfer in cryptographic applications.
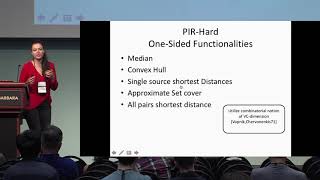
Limits of Practical Sublinear Secure Computation
Explore theoretical boundaries of efficient secure computation, focusing on sublinear communication complexity and its practical implications in cryptography.
SPDZ2k - Efficient MPC mod 2^k for Dishonest Majority
Efficient multiparty computation protocol for dishonest majority settings, operating modulo 2^k. Presents novel techniques for secure computation with improved efficiency.
Private Circuits - A Modular Approach
Explore modular approaches to private circuits, focusing on cryptographic techniques for secure computation and data protection in various applications.
Two Round Multiparty Secure Computation Minimizing Public Key Operations
Explore innovative techniques for efficient multiparty secure computation, focusing on minimizing public key operations in just two rounds of communication.