Enable Developer Self-Service Using Kubernetes and Control Planes Powered by Crossplane
Explore building internal developer platforms using Kubernetes and Crossplane. Learn to compose cloud infrastructure, prioritize security, and integrate key components for efficient developer self-service.
Testing a 3-Tier Application with Dagger's Go SDK
Explore Dagger's Go SDK for building and testing 3-tier applications. Learn about service dependencies, secret handling, step composition, and running pipelines locally, revolutionizing your CI/CD workflow.
Kubernetes Data Security and Management - Best Practices for State of the Art Protection
Master essential security practices for protecting databases on Kubernetes, from container scanning and encryption to operator-based protection and infrastructure hardening techniques.
Secure Secrets Management - Leveraging Laravel with HashiCorp Vault
Master secure secrets management by integrating Laravel with HashiCorp Vault to protect sensitive data like API keys and passwords while building robust web applications with enhanced security features.
Managing Secrets in GitOps - Best Practices and Tools
Explore strategies for managing sensitive assets in GitOps, including encryption, integration with secrets engines, and leveraging GitOps tools to enhance security in cloud-native environments.
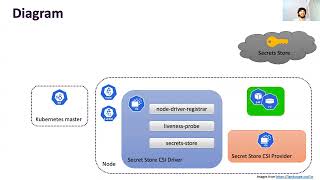
Secrets Store CSI Driver - Bringing External Secrets In-House
Explore how the Secrets Store CSI Driver enhances Kubernetes security by seamlessly integrating external secrets management systems with applications.
Optimizing Secrets Management - From Integration to Deletion
Improve secrets management lifecycle: integration, creation, rotation, and deletion. Learn strategies for enhancing security and efficiency in handling sensitive information.
Introduction to Kubernetes Security
Explore Kubernetes security essentials for operations and application development. Learn cluster access, network policies, secrets management, and secure container building techniques.
Scaling Secrets in Kubernetes: A Secure Multi-Cluster Approach - Conf42 CN 2024
Explore secure multi-cluster secret management in Kubernetes using External Secrets Operator and Sveltos. Learn benefits, implementation, and scalable solutions for managing secrets across multiple clusters.
How CircleCI's Team Uses Kubernetes to Deliver Demos
Explore CircleCI's approach to delivering enterprise demos using Kubernetes, addressing challenges, infrastructure as code, and security considerations.
Laravel on Kubernetes - Production Deployment Strategies
Explore deploying Laravel to Kubernetes, covering resource management, configurations, secrets, migrations, scheduled tasks, and safe updates for production-ready applications.
OWASP Secrets Management Cheat Sheet Overview - Best Practices for Secure Handling
Explore best practices for secrets management, including guidance for CI/CD pipelines, encryption, detection, and incident handling based on the OWASP Secrets Management Cheat Sheet.
Pets No Longer: How Kubernetes Clusters Become Cattle with Rancher Fleet
Explore Kubernetes cluster management at scale with Rancher Fleet, covering architecture, deployment strategies, and practical demonstrations for efficient multi-cluster operations.
GitHub Actions - Branch Protection, Automated Testing - Full Tutorial
Comprehensive tutorial on GitHub Actions, covering workflows, secrets, testing, and productivity enhancements. Learn to set up automated processes and improve development team efficiency.
Security Controls for Safe Chaos Experimentation
Explore security considerations in chaos engineering, including authentication, fault-blacklisting, runtime security, policy integration, and secrets management. Learn about new features in LitmusChaos 3.0 beta.
Protecting Your Crown Jewels with External Secrets Operator
Insights on integrating external secret management solutions with Kubernetes using External Secrets Operator, balancing security and productivity in regulated environments.
Mind the Gap - Integrating Cloud Services with Managed Kubernetes Environments
Explore techniques for integrating managed Kubernetes clusters with external cloud services, covering authentication, authorization, and security considerations for cloud-native applications.
Securing Kubernetes - Best Practices and Effective Strategies
Explore best practices for securing Kubernetes deployments, covering control plane protection, RBAC, network policies, security contexts, and container image security.
Building and Deploying a Secrets Plugin on Docker Swarm for Dynamic Secrets
Learn to create and deploy a dynamic secrets plugin for Docker Swarm, integrating with HashiCorp Vault for runtime secret value determination. Enhance your distributed services' security and flexibility.
Docker Security Insights - Vulnerabilities and Best Practices
Explore Docker security vulnerabilities, countermeasures, and best practices for production environments. Learn about container risks, secrets management, content trust verification, and open-source library considerations.
Building Apps in Kubernetes: The Unforgiving Sea of Containerization and the Lifesaver Tools
Explore key security challenges in Kubernetes app development and learn practical solutions using open-source tools. Gain insights from real-life examples to navigate the ecosystem confidently.