Cyber Risk Management - Understanding Impact on Audits, Regulation and Board Engagement
Explore evolving cyber risk management audits, regulations, and board engagement. Learn about changing expectations, regulatory impacts, and effective preparation strategies for future cybersecurity challenges.
The Surge of BEC Attacks and How to Mitigate Damages
Explore BEC attacks, their impact, and effective mitigation strategies through real-world case studies. Learn response procedures and recommendations to protect your organization from these prevalent cyber threats.
You See Honey, I See Beehive - Developing Honey Networks
Explore end-to-end honey networks for breach defense, combining honeypots, security sensors, and continuous monitoring. Learn open-source and enterprise options for networks of any size.
Through the Eyes of the Adversary - How to Build a Threat Intel Program
Learn to build an effective threat intelligence program by understanding adversary perspectives, focusing on key components and serving organizational stakeholders.
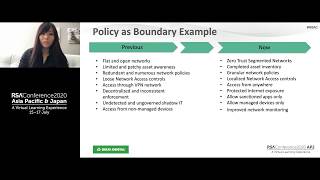
A Simplified and Practical Approach to Pursuing a Zero Trust Architecture
Practical guide to implementing zero trust architecture, focusing on identity, policy, and people. Learn design principles for a flexible, resource-efficient approach to enhance security.
Cyberespionage - Targeted Attacks Abusing Third-Party Cloud Services
Explore how APT groups exploit cloud services for cyberespionage, examining real-world cases, attack strategies, and implications for defenders and researchers across Windows and Android platforms.
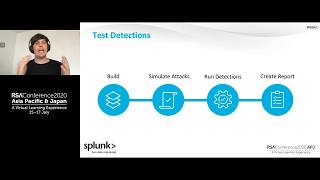
Detection as Code - Detection Development Using CI/CD
Learn modern detection engineering using CI/CD pipelines to automate rule testing. Explore Attack Range for simulating adversary attacks and streamline your security workflow.
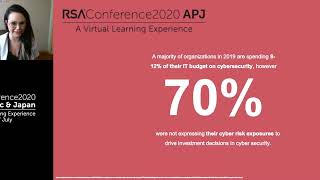
Getting the Security and Flexibility Balance Right in a COVID-19 World
Explore balancing security and flexibility in remote work during COVID-19, addressing challenges, mitigating risks, and implementing effective cybersecurity strategies for organizations.
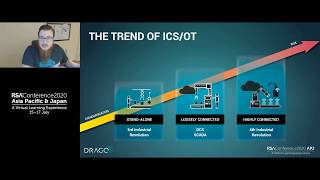
Forced Digital Transformation and the Realities to ICS - OT Cybersecurity
Explore ICS/OT cybersecurity challenges and solutions in the wake of forced digital transformation, covering threat landscapes, risk mitigation strategies, and long-term planning approaches.
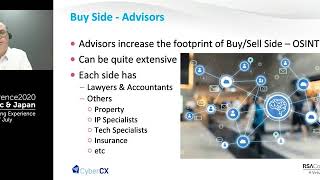
Securing Your M&A Activity with Cybersecurity Due Diligence
Learn to conduct cybersecurity due diligence for M&A activities, including program components, metrics for informed decisions, and strategies for both buy and sell sides to protect and evaluate effectively.
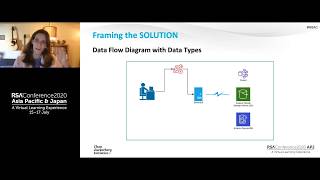
Build Privacy into Your Products and Gain User Trust
Learn strategies to integrate privacy policies and infrastructure into products, enhancing user trust and regulatory compliance while fostering growth and empowering users to understand data usage.
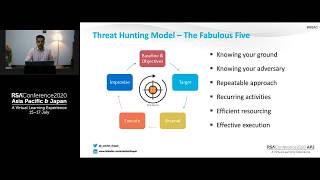
Threat Hunting - Demystified
Demystifies threat hunting as a cyber-defense strategy, exploring its implementation, phases, and best practices to effectively combat unknown threats in cybersecurity.
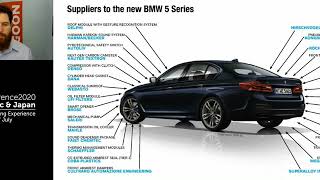
Taking Control of Cyber-Supply Chain Security
Explore cyber-supply chain security risks, best practices, and policy recommendations. Learn about Software Bill of Materials and its role in managing software dependencies and vulnerabilities.
Drone Penetration Testing and Vulnerability Analysis Framework
Explore an open-source framework for drone security testing, covering attack types and vulnerability analysis. Learn to assess and enhance drone safety in various applications.
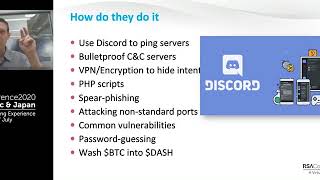
Two Weeks with a Russian Ransomware Cell
Insights from two weeks of dialogue with Russian ransomware operators, revealing their methods, motivations, and advice for IT security, with implications for future cybersecurity strategies.
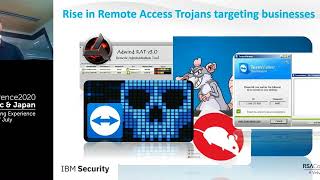
Hacking People's Mind - When Threat Actors Master Social Engineering
Explore the evolving landscape of social engineering in cybersecurity, focusing on new attack vectors, their sophistication, and strategies for fraud prevention teams to counter these emerging threats.
Seven Deadly Sins of Security Communication Part 2
Explore effective security communication strategies, learn to develop targeted plans, and gain insights on avoiding common pitfalls in large-scale security initiatives.
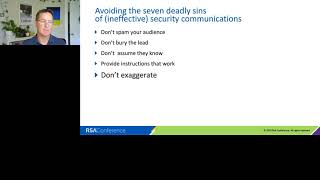
Seven Deadly Sins of Security Communication Part I
Improve security communication effectiveness by analyzing document elements like headings and calls to action, with examples of impactful messaging to drive desired behavioral changes.
Access Control Design Best Practices
Learn best practices for designing robust access control systems in web applications, covering anti-patterns, principles, and practical examples for secure implementation.
How to Get the Most Value out of Your Penetration Test
Maximize penetration test value: Learn strategies for internal buy-in, aligning with business goals, choosing testers, and evaluating results. Gain practical insights from industry expert Ed Skoudis.

Coordinated Vulnerability Disclosure - You’ve Come a Long Way, Baby
Explore new research on coordinated vulnerability disclosure, examining perspectives of researchers and organizations to understand behaviors, preferences, and practices in software flaw reporting.