Strengthening the Industrial Ecosystem: Free OT Cybersecurity Resources
Discover free OT cybersecurity resources to mitigate risks in industrial environments, addressing financial and expertise gaps for small/medium organizations.
The Risk of Trust - Social Engineering Threats and Cyber Defense
Explore social engineering threats and enhance cyber defenses in the digital trust economy. Gain actionable insights to protect against evolving risks in financial and social interactions.
Beyond the Code - SBOM and Supply Chain Security
Explore supply chain security, focusing on Software Bill of Materials (SBOM) and its role in enhancing software transparency and risk management in modern development practices.
Oh My Phish - Cybersecurity Awareness and Phishing Prevention
Explore advanced phishing techniques and defense strategies with cybersecurity experts Theram and Dhruv Bisani in this insightful Security BSides London presentation.
Security Is Key - The Vulnerabilities of API Security
Explore API security vulnerabilities and learn essential strategies to protect your systems from potential threats in this informative talk by Joe Wrieden.
How Privacy Engineering Can Streamline the M&A Process
Explore how Privacy Engineering principles and advanced methodologies can streamline M&A processes, mitigate risks, and provide crucial insights during early acquisition stages.
Implementing Email Attachment Security
Explore email attachment security implementation using pyminigip and AWS integration. Learn risks, solutions, and benefits for enhanced protection in business scenarios.
Supply Chain Security for Open Source Projects
Explore supply chain security strategies for open-source projects, enhancing protection against vulnerabilities and ensuring robust software development.
Presenting the OSTIF Independent Security Audit Impact Report
Explore OSTIF's 2022 security improvements to critical open source projects, funded by OpenSSF. Learn about the initiative's background and key outcomes.
Future Open Source LLM Kill Chains - Security Risks and Mitigation Strategies
Explore potential security risks in open-source AI ecosystems, focusing on LLM vulnerabilities and kill chains. Learn mitigation strategies to protect against sophisticated adversaries in the evolving AI landscape.
Securing the Gateway and Mitigating Risks in LLM API Integration
Explore strategies for safeguarding LLM API integrations, addressing security vulnerabilities, and implementing robust risk mitigation measures in AI-powered applications.
OWASP Low-Code/No-Code Top 10 - LCNC Security Risks
Explore the top 10 security risks in low-code/no-code platforms with expert Michael Bargury, gaining insights to protect your applications and data in this rapidly evolving landscape.
XZ Backdoor - Navigating the Complexities of Supply Chain Attacks Detected by Accident
Explore the intricacies of supply chain attacks through the lens of the XZ Backdoor incident, uncovering detection methods and implications for cybersecurity professionals.
The Magic of Application Security Posture Management and Its Future Frontier
Explore ASPM's role in fortifying application defenses, from proactive risk mitigation to predictive analytics, and its future potential with AI and blockchain integration.
Five and a Half Actions to Mitigate Software Supply Chain Threats
Discover five crucial actions to protect your software supply chain from threats, including insights from Commerzbank's use of Google Cloud's Assured OSS.
A Glimpse into DevSecOps - Building a Secure NodeJS Service
Explore DevSecOps through building a NodeJS service, focusing on security integration throughout development and deployment. Learn practical insights and best practices for robust, secure software creation.
The Iceberg - How to Mitigate Risks in Your OSS Projects
Explore strategies to mitigate risks in open-source software projects and understand the expanding attack surface in modern development environments.

Can LLMs Keep a Secret? Testing Privacy Implications of Language Models
Explore privacy risks of interactive LLMs, examining evaluation frameworks and proposing research directions for improved privacy auditing and mitigation strategies.
Articulating Risk to Senior Management - Enabling Informed Decision-Making
Explore effective strategies for communicating cybersecurity risks to senior management, enabling informed decision-making and fostering a culture of security awareness within organizations.
Data Science for Risk Mitigation in a Global Economy - ODSC East 2019
Data science strategies for global risk mitigation: standardized frameworks, scaling solutions, market size management, model monitoring, cloud variability, agility, and cross-geographic data governance.
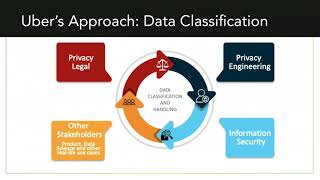
Privacy by Design for Agile Development - Uber's Approach
Integrating privacy by design principles in agile development at Uber: challenges, strategies, and practical approaches for ensuring data protection in a fast-paced tech environment.