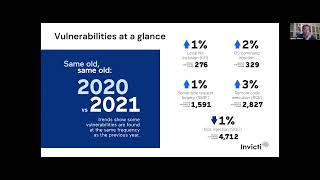
Worrisome Web Vulnerability Trends in the Race to Innovation
Explore concerning web vulnerability trends amid rapid innovation, examining their impact on security and discussing strategies for mitigation and protection.
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.
Supply Chain Security with Dependency Track
Explore supply chain security using Dependency Track with experts Anandan, Bhargava, and Duster. Learn strategies to mitigate risks and enhance software security in this informative session.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
Taking Steps Towards Community Wildfire Preparedness
Learn practical strategies for wildfire preparedness, including home protection measures and community-level management approaches, from expert panelists discussing the future of wildfire mitigation.
Imagining the Next 9/11 - Future Threats and Prevention Strategies
Experts discuss potential future threats, exploring scenarios that could rival 9/11's impact and strategies to prevent them. Insights on emerging risks and proactive measures for national security.
Internet Banking Safeguards Vulnerabilities - AppSecEU 2016
Explore internet banking vulnerabilities, attack patterns, and safeguards. Learn about transaction authorization best practices, user authentication, and regulatory requirements for secure online banking.
Mantra OS - Penetration Testing Tools and Methodologies
Explore Mantra OS's penetration testing tools for web application security, including DDoS, SQL injection, and man-in-the-middle attacks. Learn practical methodologies and controlled environment testing techniques.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.
OWASP A9: Using Components with Known Vulnerabilities - A Year Later
Explore real-world case studies and industry trends on managing component vulnerabilities in applications, with insights on best practices and challenges in following OWASP A9 guidelines.
Android and iPhone Risks and Solutions
Explore mobile security risks and effective solutions for Android and iPhone devices, enhancing your understanding of smartphone vulnerabilities and protection strategies.
How to Secure Your App With AppSweep
Learn to scan and secure your app against vulnerabilities using AppSweep, a powerful tool for identifying and addressing security issues in mobile applications.
Dependencies: Do's and Don'ts - Managing Application Dependencies Securely
Learn best practices for managing dependencies in software development, balancing security risks with benefits to team velocity and business value. Discover preventive measures to minimize vulnerabilities.
Hidden Vulnerabilities in Open Source
Explore hidden vulnerabilities in open source software with experts from Palo Alto Networks, uncovering potential risks and learning strategies for enhanced security.
A Different Kind of S3 - First Line Security of the Supply Chain
Explore innovative approaches to supply chain security, focusing on first-line defense strategies and cutting-edge solutions for robust protection against emerging threats.
Securing Open Source Through Threat Modeling
Learn to identify attack surfaces and secure open source projects through threat modeling. Discover techniques to find vulnerabilities, analyze risks, and enhance software security.
Authenticating Supply-chain Metadata - Building Remote Code Attestations on GitHub
Explore techniques for authenticating supply-chain metadata and building remote code attestations on GitHub, enhancing software security and integrity in the development process.
Rising Threat - Securing Your Open-Source Pipeline
Explore strategies to secure open-source pipelines, addressing vulnerabilities, dependencies, and best practices for robust cybersecurity in software development.
Malicious Package Trends Compared with Malware Evolution
Explore malicious package trends and their parallels with malware evolution, gaining insights into cybersecurity challenges and strategies for protecting software supply chains.
Google SLSA and NIST SSDF - Emerging Software Supply Chain Security Best Practices
Explore emerging best practices for software supply chain security, focusing on Google's SLSA framework and NIST's SSDF guidelines to enhance your organization's cybersecurity posture.
Securing Your Open Source Supply Chain
Explore strategies for securing the open source supply chain, focusing on best practices and tools to mitigate risks in software development and deployment.