Attacking the WebAssembly Compiler of WebKit
Explore vulnerabilities in WebKit's WebAssembly compiler, focusing on recent updates and new features. Learn about potential security risks and attack surfaces in browser implementations.
Realtime Communications, Realtime Risks
Explore WebSocket security risks, vulnerabilities in enterprise applications, and a new Burp Suite extension for improved pentesting of real-time communications.
16 Zero-Day Vulnerabilities Affecting CODESYS Framework Leading to Remote Code Execution
Découverte de 16 vulnérabilités zero-day dans CODESYS, un framework logiciel pour automates programmables industriels, affectant potentiellement des millions d'appareils dans divers secteurs industriels.
Stealing With Style - Using CSS to Exploit ProtonMail & Friends
Explore critical vulnerabilities in privacy-focused webmail providers, including email theft and remote code execution, through CSS exploitation techniques in ProtonMail, Tutanota, and Skiff.
Prototype Pollution Leads to RCE - Gadgets Everywhere
Explore how Prototype Pollution vulnerabilities in JavaScript can lead to remote code execution, analyzing Node.js core code and NPM packages for potential security risks.
The Return of Peer to Peer Computing
Exploring peer-to-peer computing concepts, code, and applications developed by Pythonistas in response to surveillance concerns, with focus on decentralized systems and strong cryptography.
Rehabilitating Pickle
Explore Pickle's security risks, potential defenses, and alternatives for safe Python object serialization in distributed systems.
Diving Into Spooler - Discovering LPE and RCE Vulnerabilities in Windows Printer
Uncover critical vulnerabilities in Windows Printer Spooler, exploring potential LPE and RCE exploits. Learn from past attacks and discover hidden security risks in this essential system component.
Prototype Pollution Leading to Remote Code Execution in NodeJS
Delve into prototype pollution vulnerabilities in Node.js, exploring how they enable remote code execution, analyzing real-world exploits, and understanding recent security mitigations.

Hacking Millions of Modems and Investigating Modem Security Vulnerabilities
Dive into a real-world investigation of modem vulnerabilities, ISP security flaws, and the concerning centralization of broadband infrastructure through a personal hacking incident analysis.
Exploiting Localhost APIs From The Browser - Zero-Day Vulnerability and Attack Techniques
Discover how browser-based attacks exploit localhost services through a zero-day vulnerability, featuring live demonstrations of remote code execution and novel attack techniques targeting developers behind firewalls.
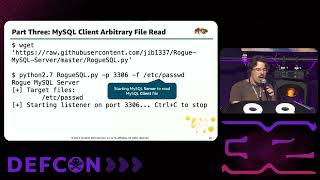
Atomic Honeypot - A MySQL Honeypot That Drops Shells
Discover how a weaponized MySQL honeypot server exploits vulnerabilities to counter-attack malicious clients, featuring innovative use of CVE-2023-21980 and CVE-2024-21096 for defensive security research.
Fuzzing Windows RDP Client for Vulnerabilities - A Research Journey
Explore Windows RDP client vulnerability research: from initial steps to uncovering remote code execution flaws. Learn about fuzzing tools, overcoming challenges, and recommendations for RDP security.
CertifiedDCOM - The Privilege Escalation Journey to Domain Admin with DCOM
Uncover a critical DCOM vulnerability allowing remote privilege escalation to Domain Admin in Windows networks. Learn about DCOM internals and exploit techniques for Active Directory takeover.
I Am Whoever I Say I Am - Infiltrating Identity Providers Using a 0-Click Exploit
Explore unauthenticated remote code execution in popular IAM solutions, covering past attacks, audit approaches, and vulnerability chaining for infiltrating identity providers.
Reverse Engineering and Hacking Ecovacs Robots - Security Vulnerabilities and Privacy Concerns
Dive into the security vulnerabilities of Ecovacs robots, exploring broken encryption, unauthorized camera access, and privacy concerns while learning techniques for privacy-preserving usage and rooting.
Outlook Unleashing RCE Chaos: Exploiting CVE-2024-30103
Dive into the critical Outlook security vulnerabilities, exploring remote code execution exploits through COM objects, NTLM leaks, and essential mitigation strategies for enterprise protection.
Leveraging HTTP Request Smuggling for Authentication Bypass and Remote Code Execution
Delve into HTTP Request Smuggling vulnerabilities, exploring real-world cases of authentication bypass and remote code execution in enterprise applications, with practical detection and mitigation strategies.
Exposing Critical Threats in Cellular Modem Security - Telit Vulnerabilities Analysis
Uncover critical security vulnerabilities in Telit cellular modems, including remote code execution flaws, SMS-based attacks, and MIDlet compromise methods that affect millions of connected devices.
Insecure Remote Operations: Windows Living Off the Land Techniques - Session 8
Dive into Windows remote operations security, exploring protocols, APIs, and admin tools through real-world examples. Learn powerful techniques for both defensive and offensive security operations.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.