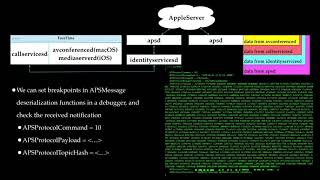
Towards Discovering Remote Code Execution Vulnerabilities in Apple FaceTime
Explore FaceTime's vulnerabilities through reverse engineering, focusing on call initialization, connection processes, and potential attack surfaces for remote code execution.
Achieving Linux Kernel Code Execution Through a Malicious USB Device
Explore Linux kernel exploitation via malicious USB devices, focusing on CVE-2016-2384 vulnerability. Learn about USB-based attacks, payload delivery, and mitigation strategies.
SAP RCE - The Agent Who Spoke Too Much
Explore SAP vulnerabilities: authentication bypass, OS command injection, and privilege escalation. Learn to decrypt sensitive files, manipulate security reports, and implement protective measures.
Exploring and Exploiting the SQLite
Explore SQLite vulnerabilities, auditing strategies, and fuzzing techniques. Learn about Magellan 2.0, shadow tables, and bypassing defense mechanisms for remote code execution in Chrome and SQLite binaries.
Over the Air Baseband Exploit - Gaining Remote Code Execution on 5G Smartphones
Explore 5G network security, baseband vulnerabilities, and remote code execution on smartphones through hands-on research, methodology, and live demonstrations.
The Hidden RCE Surfaces That Control the Droids
Uncover hidden vulnerabilities in Android OS libraries that process incoming files, potentially leading to remote code execution attacks on various system applications.
Server-Side Template Injection - RCE for the Modern Web App
Explore techniques to recognize and exploit template injection vulnerabilities, leading to remote code execution in web applications. Learn automated detection methods and application-specific exploits.
Discover Vulnerabilities with CodeQL
Explore CodeQL's static and taint analysis capabilities to uncover vulnerabilities, including potential RCE flaws. Learn key concepts for effective code analysis and security testing.
A Pre-Auth RCE on Leading SSL VPNs
Unveiling critical vulnerabilities in leading SSL VPNs, including pre-auth RCEs and backdoors. Demonstrating exploitation techniques, post-exploitation strategies, and discussing mitigation measures for enterprise security.
IOT RCE - A Study With Disney
Explore IoT device vulnerabilities using Disney's Circle and Foscam as case studies. Learn novel attack techniques, including SSL bypasses, SSID injection, and cloud routing abuse. Discuss IoT devices' use of offensive tools.
CoreOS Arbitrary Code Execution
Explore CoreOS vulnerabilities and arbitrary code execution techniques with insights from security experts Brian Redbeard and Patrick Baxter in this Shmoocon 2017 presentation.
Story of an RCE on Apple Through Hot Jar Swapping
Discover how Frans Rosen achieved remote code execution on Apple through hot jar swapping. Learn about the research, exploit, and analysis behind this impressive security finding.
Beyond the Borders of Scope
Explore unconventional recon techniques for bug bounty programs, focusing on out-of-scope assets to uncover unique vulnerabilities in core applications.
A Journey From JNDI-LDAP Manipulation to Remote Code Execution Dream Land
Explore JNDI/LDAP vulnerabilities and exploitation techniques, from basic concepts to advanced remote code execution methods in Java-based enterprise applications.
Diving Into Spooler - Discovering LPE and RCE Vulnerabilities in Windows Printer
Uncover critical vulnerabilities in Windows Printer Spooler, exploring potential LPE and RCE exploits. Learn from past attacks and discover hidden security risks in this essential system component.
Is WebAssembly Really Safe? - Wasm VM Escape and RCE Vulnerabilities Have Been Found in New Way
Explore WebAssembly security vulnerabilities through a new fuzzing framework, focusing on VM escape and RCE risks in Wasm runtimes for edge computing and web applications.
Delegate to the Top - Abusing Kerberos for Arbitrary Impersonations and RCE
Explore Kerberos delegation vulnerabilities in Windows networks, learning techniques for unauthorized impersonation and remote code execution. Gain insights into potential security risks and mitigation strategies.

Black Hat USA 2025
Black Hat USA 2025

Black Hat USA 2023
Black Hat USA 2023

Black Hat Asia 2025
Black Hat Asia 2025

Black Hat Europe 2024
Black Hat Europe 2024