
Linux Red Team Persistence Techniques - SSH Keys, Web Shells and Cron Jobs
Explore Linux persistence techniques using SSH keys, web shells, and cron jobs. Learn to maintain system access across restarts and credential changes for effective red team operations.
Windows Red Team Credential Access Techniques - Mimikatz & WCE
Explore Windows credential access techniques using Mimikatz and WCE to dump passwords and hashes from memory. Learn post-exploitation methods for red team operations and penetration testing.
Windows Red Team Persistence Techniques - Persistence With PowerShell Empire
Explore Windows Red Team persistence techniques using PowerShell Empire for maintaining access to targets. Learn about this post-exploitation framework and its features for bypassing protections.
Linux Red Team Exploitation Techniques - Exploiting WordPress & MySQL
Aprenda técnicas de exploração de equipe vermelha para identificar e explorar vulnerabilidades em servidores Linux com aplicações web, focando em WordPress e MySQL.
Windows Red Team Exploitation Techniques - Luckystrike & PowerShell Empire
Explore Windows Red Team exploitation techniques for initial access, including creating malicious macro documents and setting up a C2 server with PowerShell Empire & Starkiller.
Red Team Reconnaissance Techniques
Explore active and passive reconnaissance techniques for Red Team operations, including information gathering on organizations, infrastructure, and personnel to support targeting and adversary lifecycle phases.
Red Team Adversary Emulation With Caldera
Explore automated Red Team adversary emulation using MITRE Caldera, a framework built on ATT&CK for simulating attacks and testing organizational security defenses.
Red, Blue, and Purple AI - Augmenting Cybersecurity Teams with Practical AI Tools
Explore practical AI tools for red, blue, and purple teams in cybersecurity. Learn strategies to empower your security team with AI-driven solutions and create effective prompts for various security tasks.
Under the Radar: How We Found 0-Days in the Build Pipeline of OSS Packages
Explore critical vulnerabilities in OSS build pipelines, including 0-day discoveries in major projects. Learn about attack trees, mitigations, and 'Living Off the Pipeline' components for enhanced security.
Red Team Frameworks and Methodologies
Explore industry-standard frameworks and methodologies for planning and executing successful Red Team operations, enhancing your cybersecurity skills and knowledge.
The Hacker Hippocampus: Meet Your Brain on Games
Explore the history and impact of gamification in infosec, its effects on brain stimulation, and how it's revolutionizing learning and skill development for security professionals.
TL;DR: Applying AI to Security - Condensed Overview of AI Applications in Cybersecurity
Explore AI's impact on security: AppSec, red/blue team tactics, threat modeling. Condenses extensive research into practical applications for rapid understanding of AI in cybersecurity.
Operationalized Purple Teaming - Red Zone Space
Learn to operationalize collaboration between security teams, improving threat detection and response through Purple Team exercises. Explore practical techniques for maturing your security program using real-world examples.
I'm Not Pink, I Prefer Purple
Exploración del Purple Team en ciberseguridad: interacción Red Team vs Blue Team, Pirámide del dolor, integración del Framework Mitre & Attack y aprovechamiento del modelo Purple Team para mejorar la seguridad.
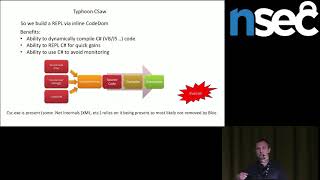
Quick Retooling with .NET Payloads
Explore dynamic .NET implants for red teams, focusing on flexible retooling, OpSec, and overcoming static defenses using DLRium Managed Execution toolkit.
Looking Forward - Finding the Right Balance for INFOSEC
Exploring the future of cybersecurity, balancing technology and talent, and addressing challenges in the industry through automation, red teaming, and strategic focus.
Go Purple! Adopt Purple Team Strategy to Augment Application Security Programs
Explore purple team strategies to enhance app security programs, bridging defensive and offensive approaches for effective collaboration and improved security outcomes.
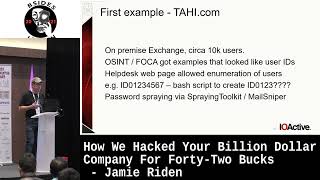
How We Hacked Your Billion Dollar Company For Forty-Two Bucks
Discover how a small investment can expose major vulnerabilities in billion-dollar companies. Learn about red teaming, user enumeration, and password spraying techniques used by ethical hackers.
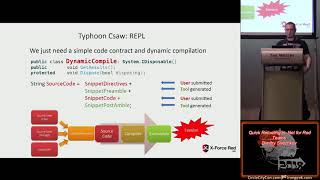
Quick Retooling in Net for Red Teams
Learn offensive recon and live retooling techniques for red teams using .NET, exploring dynamic compilation, code generation, and stealthy payload delivery methods.
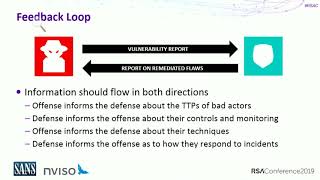
Live Adversary Simulation - Red and Blue Team Tactics
Explore live adversary simulation techniques, enhancing communication between red and blue teams for effective cybersecurity. Learn to perform threat simulations, map APT phases, and implement purple teaming strategies.
Hands-On Purple Team Exercises
Hands-on workshop on purple team exercises, combining red and blue team roles. Practice adversary emulation, threat detection, and defense improvement in a simulated environment.