reNgine - An Automated Reconnaissance Framework
Explore an automated reconnaissance framework for efficient cybersecurity assessments, enhancing vulnerability detection and streamlining security workflows.
Information Gathering With Shodan
Demonstración práctica del uso de Shodan para recopilación de información y reconocimiento en pruebas de penetración, explorando sus filtros y capacidades de búsqueda de dispositivos conectados a Internet.
HackTheBox Arctic Machine Walkthrough
Comprehensive walkthrough for successfully exploiting the Arctic machine on HackTheBox, demonstrating penetration testing techniques and vulnerability exploitation in a controlled environment.

Raven1 VulnHub CTF Walkthrough - Boot-To-Root
Comprehensive walkthrough of Raven1 CTF challenge from VulnHub, demonstrating boot-to-root exploitation techniques for ethical hacking and penetration testing practice.
Ghost in Your Supply Chain - APT Attacks on Taiwan's Financial Sector
Explore APT attacks on Taiwan's financial sector, focusing on supply chain vulnerabilities. Learn about MDM platform exploitation, JIRA abuse, and malware-free attacks. Gain insights into island-hopping techniques and comprehensive threat mapping.
How AI Impacts Reconnaissance and Bug Bounties in Cybersecurity
Exploring AI's impact on cybersecurity, this interview covers its role in bug bounties, potential risks, job market effects, and defensive strategies against malicious AI use.
Certified Ethical Hacker (CEH) Exam Prep - Step-by-Step Breakdown to Certification - Day 1
Master ethical hacking skills and prepare for CEH certification with a comprehensive overview, key domain practice, and exam strategies. Gain insights into reconnaissance, scanning, and web application hacking.
New Methods of Recon - Enhancing Reconnaissance Techniques
Refine and expand your reconnaissance toolkit with top hacker OrwaGodfather's precise tactics, enhancing your bug hunting capabilities.
Certified Ethical Hacker (CEH) Exam Prep - Step-by-Step Breakdown to Certification - Day 2
Master ethical hacking techniques, explore key domains, and prepare for the CEH exam with hands-on exercises, real-world scenarios, and expert guidance. Enhance your cybersecurity skills and career prospects.
How to Build a Secure Recon Network Using Tailscale
Build a secure recon network with Tailscale to protect your offensive tools, safeguard data, and enhance your bounty hunting capabilities.
Active Directory Enumeration with BloodHound
Automate and visualize Active Directory enumeration using BloodHound. Learn to streamline the process of identifying vulnerabilities and attack paths in AD environments.
Beginner to Advanced Bug Bounty Hunting Course - 2022
Comprehensive ethical hacking course covering web application vulnerabilities, penetration testing techniques, and programming skills for aspiring bug bounty hunters and security professionals.
Pivoting and Exploitation in Docker Environment
Demostración de técnicas de pivoting, explotación y escalada de privilegios en entornos Docker con múltiples redes. Incluye metodologías de pentest y superación de obstáculos en diferentes configuraciones de red.
Lemon Booster - Automatizando desde la UI
Automatización del reconocimiento en programas de Bug Bounty con Lemon Booster: herramienta con interfaz visual para ejecutar, analizar y monitorear resultados, agilizando el proceso de búsqueda de vulnerabilidades.
MagicRecon - Bug Bounty Space
Exploración de MagicRecon, una herramienta para recolección de datos y búsqueda de vulnerabilidades en pentesting y Bug Bounty. Enfoque en la importancia de la fase de reconocimiento en hacking ético.
No Win32_Process Needed - Expanding the WMI Lateral Movement Arsenal
Explore advanced WMI lateral movement techniques beyond Win32_Process, expanding the arsenal for threat actors and enhancing defensive strategies against sophisticated attacks.
I Know What Your Microsoft Mainframe Did Last Summer
Explore Active Directory forensics, lateral movement, and reconnaissance techniques. Learn to hunt for clues without AD logs using open-source tools in this hands-on session with real-world incident insights.
Exploiting Windows Group Policy for Reconnaissance and Attack
Explore Windows Group Policy vulnerabilities, reconnaissance techniques, and attack paths. Learn defensive strategies to protect against Group Policy exploitation.
Prisoner Number Six
Explore Docker container escape techniques through live demonstrations, covering reconnaissance, exploiting vulnerabilities, and gaining system access. Learn practical cybersecurity skills for container environments.
ReconPi
Explore ReconPi, a tool for efficient reconnaissance in cybersecurity, with insights on its inspiration, functionality, and practical applications.
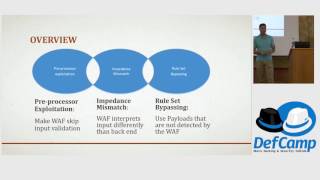
Web Application Firewall Bypassing - DefCamp - 2016
Aprende técnicas avanzadas para evadir firewalls de aplicaciones web, incluyendo métodos de reconocimiento, explotación de discrepancias y bypass de reglas para pruebas de penetración efectivas.