Scaling Argo Security and Multi-Tenancy in AWS EKS at The New York Times
Explore NYT's approach to scaling Argo security and multi-tenancy in AWS EKS, focusing on architectural patterns, IAM integration, and solutions for scaling challenges in a multi-cluster environment.
From the Cluster to the Cloud: Lateral Movements in Kubernetes
Explore techniques for lateral movement from Kubernetes containers to cloud resources, covering RBAC misconfigurations, authentication methods, and real-world incidents. Learn prevention and detection strategies.
Beyond Cluster-Admin - Getting Started with Kubernetes Users and Permissions
Learn to implement users and permissions in Kubernetes clusters, covering user provisioning methods, RBAC for fine-grained access control, and strategies for both managed and self-hosted environments.
Kubernet-Bees: How Bees Solve Problems of Distributed Systems
Explore fascinating parallels between honey bee colonies and distributed systems, uncovering nature-inspired solutions for Kubernetes challenges and future innovations.
Kubernetes Environments Visualization - Strategies and Solutions at GitLab
Explore GitLab's approach to visualizing Kubernetes environments, managing access, and leveraging the GitLab platform for effective environment management and resource visualization.
Securing Your Infrastructure as Code Pipeline
Explore techniques for securing Infrastructure as Code pipelines, including static analysis, RBAC, and open-source tools like Open Policy Agent and Sigstore, to enhance productivity and compliance.
In-use Protection for Kubernetes Resources: PV, PVC, Secret, and Beyond
Explore Kubernetes resource protection mechanisms, focusing on PV, PVC, and Secrets. Learn about RBAC, Finalizers, and new features like In-use Protection and Secret Protection for enhanced security.
Kubernetes Authentication and Authorization at Robinhood - Lessons from Reductions, Migrations, and Designing Automation
Explore Robinhood's journey in implementing least privilege for Kubernetes RBAC, including challenges, solutions, and lessons learned in managing authentication and authorization.
Kubernetes Security 101: Best Practices to Secure Your Cluster
Learn best practices for securing Kubernetes clusters, covering control plane components, worker nodes, CIS Benchmarks, RBAC, audit logs, and network policies to enhance cluster protection.
Kubernetes Cluster Security and Usability: Best Practices and Common Pitfalls
Practical guide to securing Kubernetes clusters, covering common misconfigurations, scalable security approaches, and best practices for different deployment scenarios and threat models.
Policy as Code: A Game-Changer for Stack Security
Explore "Policy as Code" and its impact on stack security. Learn about access control models, policy engines, and how to integrate authorization into your codebase for enhanced application security.
Living off the Land Techniques in Managed Kubernetes Clusters
Explore advanced techniques for exploiting managed Kubernetes clusters, including privilege escalation, lateral movement, and security control bypasses using cluster middleware and components.
Designing a Multitenancy Kubernetes Strategy That Fits Your Organization
Explore strategies for multi-tenant Kubernetes clusters, addressing resource sharing, access control, security, and cost management. Learn to overcome challenges and avoid pitfalls in enterprise deployments.
The Art of Debugging Inside Kubernetes Environments
Mastering Kubernetes debugging: Strategies, tools, and techniques for troubleshooting common errors in deployments, RBACs, NetworkPolicies, and more. Enhance your skills to build robust, easily debuggable applications in K8s environments.
Deep Dive into Open Policy Administration Layer (OPAL) - Authorization in Software
Explore advanced authorization with OPAL, covering the shift from RBAC to ABAC, policy-based systems, and decoupling authorization from code for improved security and efficiency.
A Wander Through the World of Container Security
Explore container security, from Docker to Kubernetes, covering breakout vulnerabilities, networking challenges, and RBAC. Gain insights into potential threats and future attack vectors in containerized environments.
How to Secure Your Node.js Containers on Kubernetes With Best Practices
Discover best practices for securing Node.js containers on Kubernetes, covering cluster protection, OIDC implementation, and application-specific security measures for robust DevOps deployments.
What's in Helm v3?
Explore Helm v3's key updates: Tiller removal, RBAC integration, enhanced security, chart repository changes, and improved upgrade strategy using three-way strategic merge patches.
Building Flux's Multi-Tenant API with K8s User Impersonation
Explore Kubernetes multi-tenancy using Flux as an example. Learn RBAC, impersonation, and kubeConfig secrets to enable safe collaboration across namespaces and clusters.

Ansible Tower: Enterprise-Level Infrastructure Management
Centralize infrastructure management with a web-based GUI, featuring RBAC, job scheduling, and graphical inventory control for enterprise-level Ansible usage.
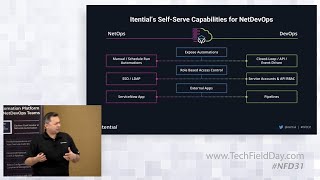
How Itential Helps NetDevOps Teams Expose and Deliver Self-Service Network Automations
Discover how to empower NetDevOps teams with self-service network automation capabilities through Itential's Operations Manager, enabling secure API exposure, RBAC integration, and ServiceNow platform integration.