Tackling Software Supply Chain Security as an Organization - Episode 128
Explore organizational approaches to software supply chain security with experts discussing solutions, initiatives, and best practices for managing risks and improving visibility.
Software Supply Chain Security: Definition and Importance - Episode 1
Explore the key pillars of software supply chain security in this comprehensive podcast episode. Gain insights into problem definition, essential terms, and practical implementation strategies for enhancing your organization's security posture.
Malicious Packages and Malicious Intent - Episode 123
Explore malicious attacks, open source security, and practical tips for improving company safety with Liran Tal, director of developer advocacy at Snyk and Github Star.
Detection as Code - Buzzword or Panacea?
Explore the reality of Detection-as-Code in cybersecurity. Separate hype from facts and understand its potential benefits for blue teams and threat detection programs.
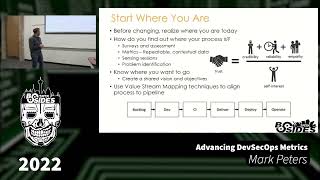
Advancing DevSecOps Metrics - Creating a Clear Path to Improved Performance
Integrate a clear path to improved performance by advancing DevSecOps metrics. Learn to deconstruct core metrics for accelerated delivery and increased customer value.
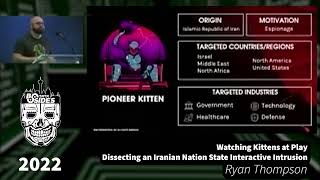
Dissecting an Iranian Nation State Interactive Intrusion - Watching Kittens at Play
Dissect an Iranian nation-state intrusion, gaining insights into adversarial tactics. Learn threat hunting techniques to uncover and counter sophisticated cyber attacks in your environment.
Why You Can Still Get Hacked Even After Signing Your Software Artifacts
Explore artifact poisoning tactics in software supply chains and learn prevention methods, including secure artifact signing, to protect your CI/CD pipeline from malicious injections.
Defense in Depth: Refocusing on Defensive Security Techniques
Explore defensive product security techniques, emphasizing defense-in-depth and supply chain security. Learn key aspects to consider in your application security strategy.
Mapping Your External Attack Surface: Illuminating Hidden Vulnerabilities
Illuminate hidden assets and vulnerabilities in your external attack surface using powerful reconnaissance tools. Proactively defend your digital perimeter and stay ahead of potential threats.
Inclusive by Design - Revolutionizing Accessibility
Revolutionize accessibility through inclusive design principles. Learn strategies to create digital experiences that cater to diverse user needs and abilities.
Breaking Chains: Overcoming Impostor Syndrome in Open Source Contributions
Discover strategies to overcome impostor syndrome and confidently contribute to open source projects. Learn to break mental barriers and unleash your potential in the tech community.
Building a DeGoogled, Privacy-Friendly, and Open Source Mobile Ecosystem - The Story Behind /e/OS
Discover the journey behind /e/OS, a privacy-focused, open-source mobile ecosystem designed to be free from Google's influence.
How Patents Remain a Threat to Open Source
Explore patent threats in open innovation with insights from legal and technology experts on current challenges and strategies.
Open Source Supply Chain Security for Enterprises
Explore enterprise-level open source supply chain security strategies with insights from JPMorgan Chase's Product Security Director.
The Inclusive Codebase: Engineering Accessibility in Open Source Software
Explore strategies for integrating accessibility into open source software development, fostering inclusivity and enhancing user experiences for all.
Breaking Barriers: The Art of Gamified Security Training
Explore gamified security training techniques to enhance cybersecurity skills effectively and affordably, breaking barriers in traditional learning approaches.
The Need for Software Bills of Materials (SBOMs) - Why You Should Disclose Your Software Usage
Explore the importance of Software Bills of Materials (SBOMs) in modern software development and understand their role in enhancing transparency and security.
The Myriad Paths to Improving Open Source Security
Explore diverse approaches to enhance open source security with expert insights from Rory McCune at SOOCon23 Security.
Do You Know the Health of Your OSS Dependencies? Introducing OSSF Scorecard API
Explore the OSSF Scorecard API to assess and improve the health of your open-source software dependencies, enhancing overall security.
Modelling Threats Out in the Open Source - SOOCon23 Security
Explore open-source threat modeling techniques to enhance software security and identify potential vulnerabilities in your projects.
Regulation by Telemetry - How to Fix OS Security by 2030
Explore strategies to enhance OS security through telemetry-based regulation, aiming for improved cybersecurity measures by 2030.