AppSec Contractual Sins - Identifying and Addressing Security Issues in Contracts
Explore common AppSec contractual pitfalls and best practices for securing software development agreements in this DefCamp 2023 presentation by Canon's EMEA Information Security Manager.
The State of Cybersecurity - 2023 Year in Review
Insights on 2023's cybersecurity landscape, including attacker techniques, defense strategies, and impact on executive decisions, from Mandiant's incident response experiences.
Navigating the Software Supply Chain Defense Landscape
Explore software supply chain security tools and frameworks, their integration, and how to select the right combination for comprehensive protection against rising cyber threats.
How Entertainment Shapes Future Tech Trends
Explore how entertainment drives tech adoption, influencing development priorities and societal acceptance of innovations like AR and AI, with insights from a VFX industry expert.
Exciting New Features in nRF Connect SDK 2.6.0 - Webinar Overview
Explore new features in nRF Connect SDK 2.6.0, including Matter 1.2 support, Wi-Fi enhancements, and improved development tools. Demos showcase Devicetree Visual Editor, Wi-Fi throughput, and nPM1300 functionality.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security strategies for new technologies, emphasizing the importance of product security in today's cyber landscape and the need for innovative, affordable approaches.
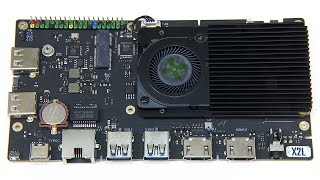
Radxa X2L - Low-Cost x86 SBC with RP2040 Review and Demo
Comprehensive review of Radxa X2L, an x86 single board computer with RP2040 microcontroller. Covers unboxing, specs, performance tests, and unique features like onboard Raspberry Pi Pico functionality.
Automated Simulation-Based Flow for Low-Cost FPGA-Accelerated Devices with Zephyr on BeagleV-Fire
Explore FPGA acceleration with Zephyr on BeagleV-Fire: Learn to design custom peripherals, integrate with firmware, and simulate using Renode for efficient low-power, high-performance systems.
Structured Scorecard Results: Tailor Your Own Supply-Chain Security Policies
Learn to customize OpenSSF Scorecard for tailored supply-chain security assessments using Structured Results feature. Explore practical examples and use cases for automated policy-driven analysis.
Practical SBOM Management with Zephyr and SPDX
Learn to identify, assess, and manage software components in Zephyr applications using SBOM standards and tools. Enhance security practices and respond effectively to vulnerabilities in embedded systems.
Compound Interest - Dealing with Two Decades of Technical Debt in Embedded Linux
Explore strategies for managing technical debt in the GPIO subsystem of the Linux kernel, focusing on improvements in serialization, hot-pluggability, and API optimization while maintaining legacy support.
The 5 Ws and H of Open Source Community - Panel Discussion
Experts discuss the 5 Ws and H of open source communities, exploring key aspects, real-world examples, and how to get involved in this dynamic ecosystem.
The Past, Present, and Future of Cross-Site and Cross-Origin Request Forgery
Explore the evolution of Cross-Site Request Forgery attacks, their impact on applications, and effective defense strategies. Learn about vulnerabilities in API-based systems and best practices to prevent CSRF.

OWASP Juice Shop - An Open Source Software and Security Fairytale
Explore the evolution of OWASP Juice Shop, a pioneering hacking training platform, from its inception as a pet project to becoming an OWASP Flagship project, with insights into its future developments.
My Favorite Ethical Hacking Books
Discover essential ethical hacking books recommended by a top hacker. Gain insights into web application security, bug bounty hunting, and penetration testing to enhance your cybersecurity skills.
Hypnosis - Virtual Reality Unplugged
Explore hypnosis as a natural psychological phenomenon and its potential for self-improvement. Learn how understanding cognitive mechanisms can unlock mental wellness through self-hypnosis techniques.
The End of DevSecOps? - Leveraging New Tools and AI in Engineering-First Security
Explore how Generative AI and new tools can simplify communication, reduce toil, and integrate security seamlessly into engineering processes, moving beyond traditional DevSecOps.
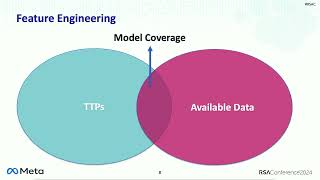
Detecting Website Intrusion and Account Compromise with Machine Learning
Explore machine learning techniques for detecting website intrusions and account compromises, covering data analysis, feature engineering, and real-time integration in open environments.
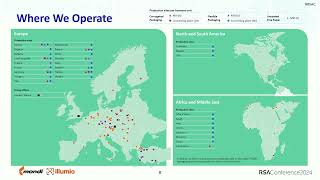
How Visibility and Segmentation Can Improve Your Sleep - Cybersecurity for IT and OT Environments
Explore strategies for better cybersecurity through risk assessment, environment separation, and simplified policies, leading to improved peace of mind in IT and OT landscapes.
GUAC 101 - Introduction to Graph for Understanding Artifact Composition
Explore GUAC, a tool for generating software bills of materials (SBOMs) and vulnerability scanning in cloud-native environments, enhancing security and compliance.
The GPL and the Legal Limits of Blender Usage
Explore the GPL license's impact on Blender usage, including its history, legal implications, and potential future scenarios. Gain insights into open-source software and its effects on creators and businesses.