An Open Source Telco Cloud Stack to Accelerate Cloud Native Operator Model Adoption
Explore an open-source Telco Cloud stack for 5G CNF support, featuring cloud-native infrastructure, scalability, and automation. Learn about its ecosystem integration and see a demo of distributed lab testing.
Dissecting the 0-Day Supply Chain Vulnerability in Argo CD
Explore the discovery and implications of a critical 0-day vulnerability in Argo CD, including attack methods, remediation steps, and its impact on the ecosystem.
Making Your Apps and Infrastructure Services Failure-Resilient with Dapr
Explore Dapr's role in enhancing microservices resilience, applying global policies for failure recovery across apps and infrastructure, regardless of deployment location or programming language.
Securing Your Container Native Supply Chain with SLSA, GitHub and Tekton
Practical guide to securing container native supply chains using SLSA principles, in-toto attestations, and step-by-step demos for achieving SLSA Level 2 in Tekton and Github Actions.
Distributing Supply Chain Artifacts with OCI and ORAS Artifacts
Explore secure distribution of supply chain artifacts using OCI & ORAS Artifacts. Learn about managing artifact relationships, lifecycle management, and evolving registry capabilities for cloud-native environments.

Securing Web Services with Let's Encrypt and Cert Manager
Automate SSL/TLS certificate management for web services using Let's Encrypt and Cert Manager, enhancing security and simplifying deployment in cloud-native environments.
Securing Shopify's Software Supply Chain - Mitigating Supply Chain Attacks
Explore techniques for securing software supply chains, including cloud-based defenses, trust establishment, and malicious behavior detection, drawing from Shopify's experiences.
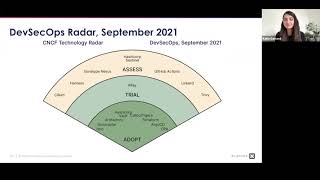
CNCF End User Technology Radar for DevSecOps - September 2021
Explore DevSecOps trends and recommendations from CNCF's End User Community. Gain insights on security solutions, micro-segmentation, and balancing security with developer experience in cloud-native environments.
Certs Magic - Exploring Cloud Native Security Certifications
Explore the world of cloud native certifications with expert Walid Shaari, gaining insights into career advancement and industry-recognized credentials.

The Beginner's Guide to Blind XSS - Cross-Site Scripting
Learn to identify and exploit Blind XSS vulnerabilities, a critical web security flaw. Discover tools like XSS Hunter and gain practical skills for ethical hacking and bug bounty hunting.
Breaking ML Services: Finding Zero-Days in Azure Machine Learning
Uncover critical vulnerabilities in Azure Machine Learning, including credential leaks, information disclosure, and persistence techniques. Learn assessment methods for cloud-based MLaaS platforms and shared responsibility models.
Cybersecurity Integration from the Beginning - Perils and Benefits
Explores challenges and benefits of integrating cybersecurity from project inception, offering insights on overcoming resistance, developing secure designs, and building value chains in early-stage cybersecurity implementation.
Overcoming Barriers in Security DSLs with BabbelPhish - Empowering Detection Engineers
Explore BabbelPhish, an innovative approach using large language models to bridge natural language queries and security DSLs, streamlining threat detection and making detection-as-code platforms more accessible.
Building Secure Hybrid Mobile Applications - A Security Professional's Guide
Learn to assess and secure hybrid mobile apps by understanding threat models and vetting external libraries, enhancing your ability to build robust applications.
Security Risks of Low-Code/No-Code Applications - What Could Go Wrong?
Explores security risks of low-code/no-code platforms used by business professionals. Presents research findings, demonstrates common security issues, and introduces OWASP framework for mitigating risks in business-led development.
Passwords: Policies, Securing, Cracking, and More
Explore password security essentials, from creating strong policies to understanding cracking techniques. Learn to secure passwords in AD and AAD, and discover why they remain crucial despite MFA adoption.
Perfect Vulnerability Reports and Still Getting Hacked - Limitations of Security Tools
Explore limitations of vulnerability detection tools, challenges in vulnerability management, and strategies for improving application security despite imperfect reporting systems.
Authentik - Open Source Self-Hosted Authentication System with OIDC and SAML
Explore Authentik, an open-source authentication system. Learn installation, configuration, reverse proxy setup, forward authentication, and OIDC implementation for enhanced security.
The Importance of Engineering Privacy From the Start
Explore strategies for protecting user data and identity in software development, emphasizing the ethical responsibility of engineers as stewards of sensitive information.
Hiding in Plain Sight - The Untold Story of Hidden Vulnerabilities
Uncover limitations of vulnerability scanners and SCA tools through groundbreaking research. Learn about hidden vulnerabilities, scanner blindspots, and the need for holistic software security approaches.
The Attacker's Guide to Exploiting Secrets in the Universe
Explore methods to discover and exploit secrets in git repositories, containers, and compiled apps. Learn about vulnerabilities in API keys and credentials across various environments.